Authorization for staff
Last updated: Nov 3, 2026
All the applications that Fluid Attacks uses must have authorization settings for each user. Thus, Fluid Attacks can apply a least privilege policy at all times. These are some examples:
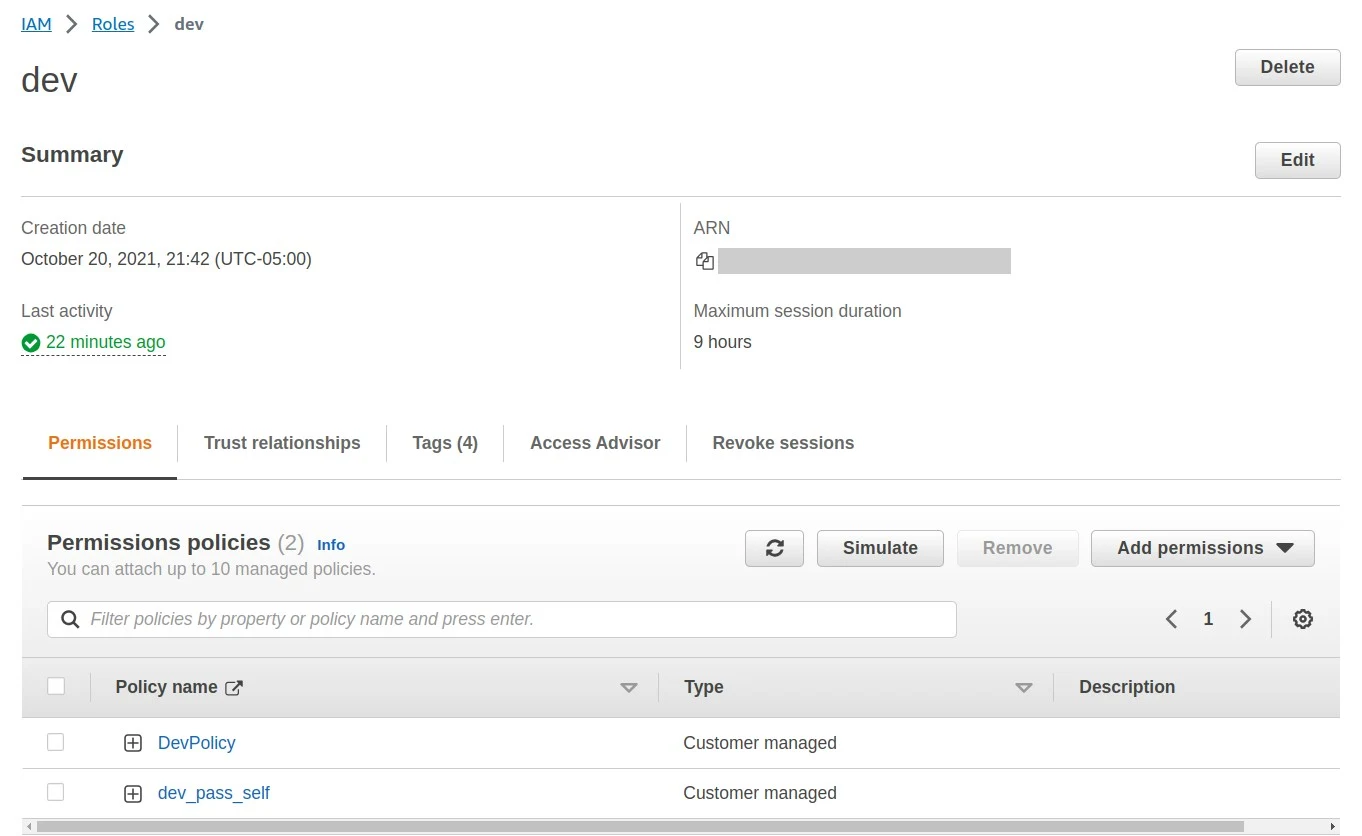
- IAM and KMS: Fluid Attacks uses these two tools widely. With them, Fluid Attacks makes sure that pentesters can only get access to the source code, environments, exploits, and secrets of their assigned projects. Fluid Attacks can easily remove access when necessary, without leaks of users or passwords. With these tools, Fluid Attacks also keeps the production secrets of applications hidden from developers (separation of production and development secrets).
- Infrastructure: Infrastructure components always give the minimum privileges, and only to the applications that need them. Fluid Attacks does not give a service full permissions on all its infrastructure.
- IAM: IAM can give user-level access to the application. Thus, Fluid Attacks can give each talent access only to what they need to do their tasks. It is simple to give or remove access to applications, and no users or passwords leak.