Billing
Last updated: Nov 4, 2026
The billing model uses the monthly activity of the authors. It uses the changes to the source code in the repositories that you registered on the platform.
The billing starts on the first business day of each month, when Fluid Attacks generates the author list of the previous month. Fluid Attacks examines this list manually to remove duplicate authors. There can be duplicates because an author can use other accounts for some commits, in addition to the primary email or account. Then, Fluid Attacks uses this clean list to calculate the billing of the organization for the month.
Fluid Attacks charges all the authors who change the source code of a repository on the platform (additions, modifications, or deletions). Authors who change only files in excluded paths do not pay. Bots count as authors. Fluid Attacks charges them if they contribute to files in the scope. Their code can cause vulnerabilities, and Fluid Attacks tests that code as part of the accuracy SLA. If you do not want to pay for bot contributions, make sure that bots contribute only to excluded paths.
Fluid Attacks bills commits by the date of their merge into the configured branch on the platform. It does not use their creation date. Thus, the code analysis starts from that moment.
Because of this, the billing can include authors who did not make commits during the billed month. This can occur when developers make changes in branches before the final version (pre-release). Then, they integrate these commits into the active branch on the platform. The date when Fluid Attacks sees a commit can be different from its original authorship date.
You can register a repository on more than one branch
(multi-branch support).
Then, Fluid Attacks bills each registered branch independently
for the month in which it sees the merged commits.
Thus,
if an author makes changes that go to different branches
in different months,
Fluid Attacks can bill that author two times.
Changes to the Git history can cause more charges.
Author identification
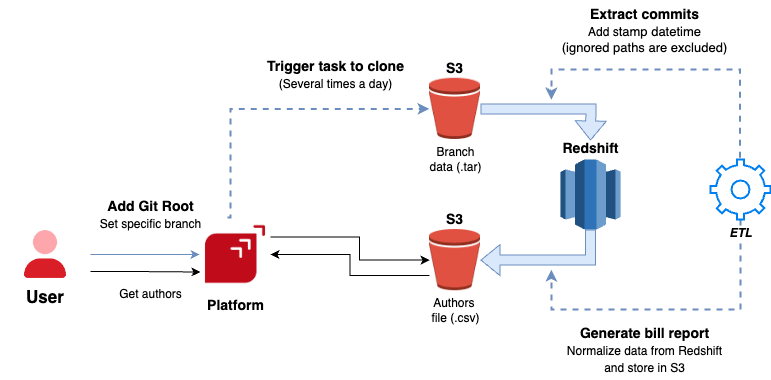
This process gets all the authors (persons or bots) who changed the source code (additions, modifications, deletions). Fluid Attacks counts only the changes that it sees as merged on a date in the previous month. To do this, Fluid Attacks uses the Git history of each repository. It uses only the branch that you configured on the platform. The diagram below shows the procedure to generate the report of authors. The subsections below give the details of author identification in simple words.
Preliminary considerations
Author identification uses these items:
- Git, a distributed version control system.
Git gives the "change history" of code projects.
With Git, you can:
- Save versions of the work of a developer with "commits".
- Record each change, who made it, and when.
- Create branches to work on new features independently, and then merge them into the primary project.
- The synchronization of the commit history from a Git repository with the Snowflake database of Fluid Attacks.
- Snowflake, a single Fluid Attacks database that keeps the complete and permanent history of all the commits. It is the single source of truth for all the analysis.
- DynamoDB, a component that keeps the hash of the last processed commit. This hash tells Fluid Attacks where to continue in the next run. Thus, slow and expensive queries to Snowflake are not necessary.
- The unique commit identifier,
which the system uses to see if a commit is already in Snowflake.
The system uses a combination of
group name,repository nickname, andcommit hash.
Process
The process has these steps:
- Cloning: The system clones the latest version of the Git repository to make sure that it has the most recent history.
- Checking of the starting point:
The system must know the point
from which it records new commits:
(a) The system queries DynamoDB to get the hash of the "commit of reference" (the last commit in Snowflake).
(b) The system searches for the hash in the history of the new clone. Thus, the system makes sure that nobody changed the history. - Scenario 1: The commit of reference exists:
This is the most common and the fastest scenario:
(a) The system finds the commit of reference in the history.
(b) The system iterates through the Git history from the commit of reference. Then, it inserts only the new commits into Snowflake.
(c) DynamoDB keeps the hash of each commit that the system inserts and updates the commit of reference. - Scenario 2: The commit of reference does not exist:
This scenario occurs if someone rewrote the Git history.
The DynamoDB "marker" is then not correct.
In this scenario:
(a) The process does not find the commit of reference. This shows that the integrity of the history changed.
(b) To prevent the loss or duplication of information, the system starts a full synchronization:
(i) It iterates through all of the Git history, from the first commit to the last. For each commit, it checks Snowflake (withgroup name,repository nickname, andcommit hash) to see if the commit is already there.
(ii) If a commit is not in Snowflake, the system inserts it. This method is slower than the method in Scenario 1. But when someone changes the Git history, this method continues to keep the data correct. - Author count: To bill a client, Fluid Attacks validates all the commits that it inserted into Snowflake during the month. Fluid Attacks counts each author of these commits only one time. The total gives the amount that the client must pay.
Billing report generation
In this phase, the process removes duplicate commits and puts together the information from all the repositories of the organization. These lists include the names of the authors, the groups that they contributed to, the commit IDs, and the repository names. The lists show an example for each author. The process does not include the authors who contribute only to files outside the scope of testing.
In the process, a commit is unique when its information has no duplicates. This validation includes fields such as the name of the author, email, date of authorship, and message content. If one of these fields changes, Fluid Attacks can include the commit in the billing.
Then, you can examine these reports on the platform, in the Billing section of your organization and in the Authors section of your groups.
Billing section
Role required: Organization Manager
The Billing section of your organization shows the billable information of each period. For the invoiced amounts, contact your Customer Manager or [email protected].
The top of the section shows these values for the selected period:
- Groups distribution: The number of groups that Fluid Attacks bills in the period, for each plan (Essential and Advanced)
- Authors: The number of billed authors in the period, for each plan
Each author counts only one time, under the highest plan of the groups that the author contributed to. These values do not include author minimums or prorated charges. To validate these charges, contact your Customer Manager.
The section has two tabs: Billing history and Payment methods.
Billing history
The Billing history tab has a period list with the last 12 months. Select a month (for example, 10/2026) to see the billable information of that period.
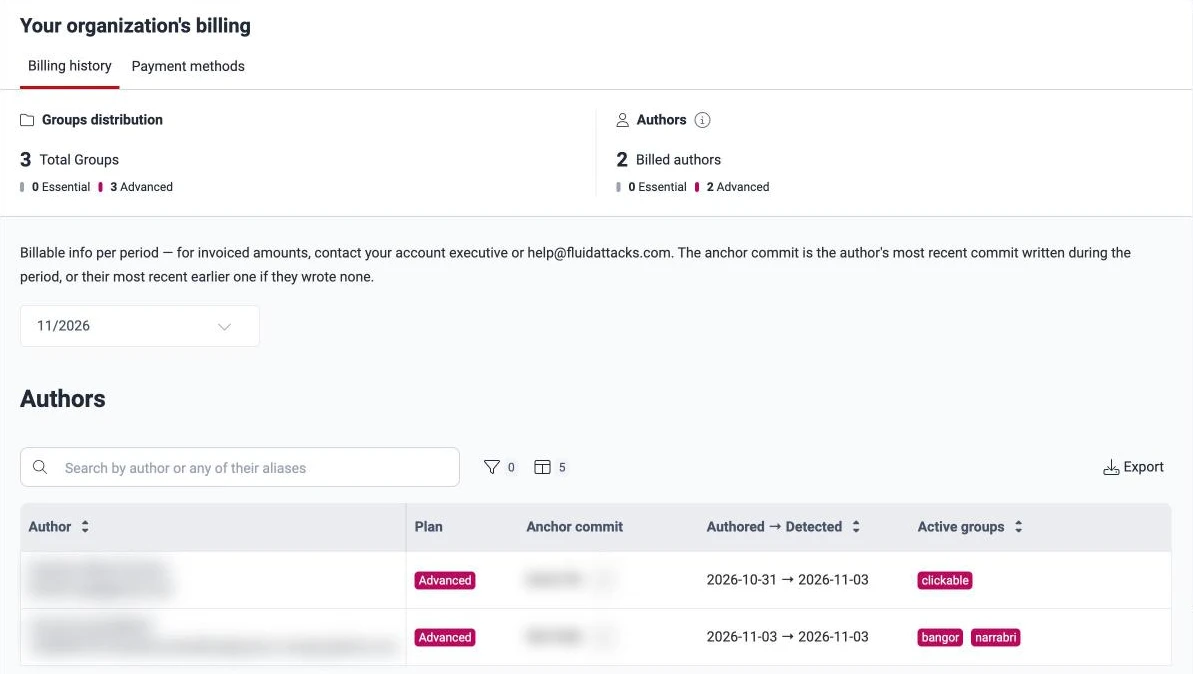
The tab shows the Authors table of the selected period. The table includes the authors of all the plans. It has these columns:
- Author: The name and the email of the author
- Plan: The plan that Fluid Attacks uses to bill the author
- Anchor commit: The commit that Fluid Attacks uses as evidence to bill the author in the period. It is the most recent commit that the author wrote during the period in a group of the highest plan. If the author wrote no commits in the period, it is the most recent commit that the author wrote before the period.
- Authored → Detected: The date when the author wrote the anchor commit, and the date when Fluid Attacks detected the commit
- Active groups: The groups where the author was active. The color of each group shows its plan.
- Repository: The repository of the anchor commit. By default, the table does not show this column.
To show or hide columns of the table, for example Repository, use the columns button next to the filter button.
Use the search field to find an author by name, alias, or email address. Fluid Attacks merges the aliases of an author with a mailmap. Thus, an author with aliases counts as one author, and Fluid Attacks bills the author only one time.
Use the Active groups filter to show only the authors of the groups whose names match the text.
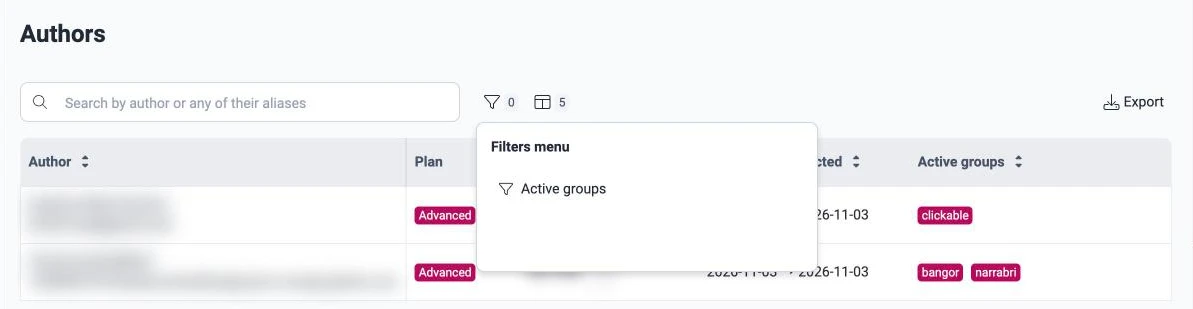
To get all the authors of the period in a CSV file, select Export. The report is available in the Downloads section of the Fluid Attacks platform.
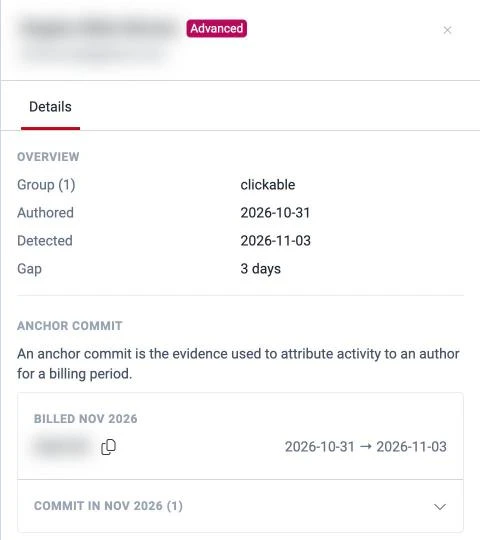
Select an author to see the details:
- Overview: The groups of the author, the Authored date, the Detected date, and the Gap (the number of days between the two dates)
- Aliases: The names and email addresses that the author uses in commits. The Fluid Attacks platform shows this section only when the author has aliases.
- Anchor commit: The commit that Fluid Attacks uses as evidence. Under the anchor commit, you can see the commits of the author in the period. To see more commits, select Load more commits.
Payment methods
The Payment methods tab shows the payment methods of your organization in two tables: Credit card and Other methods.
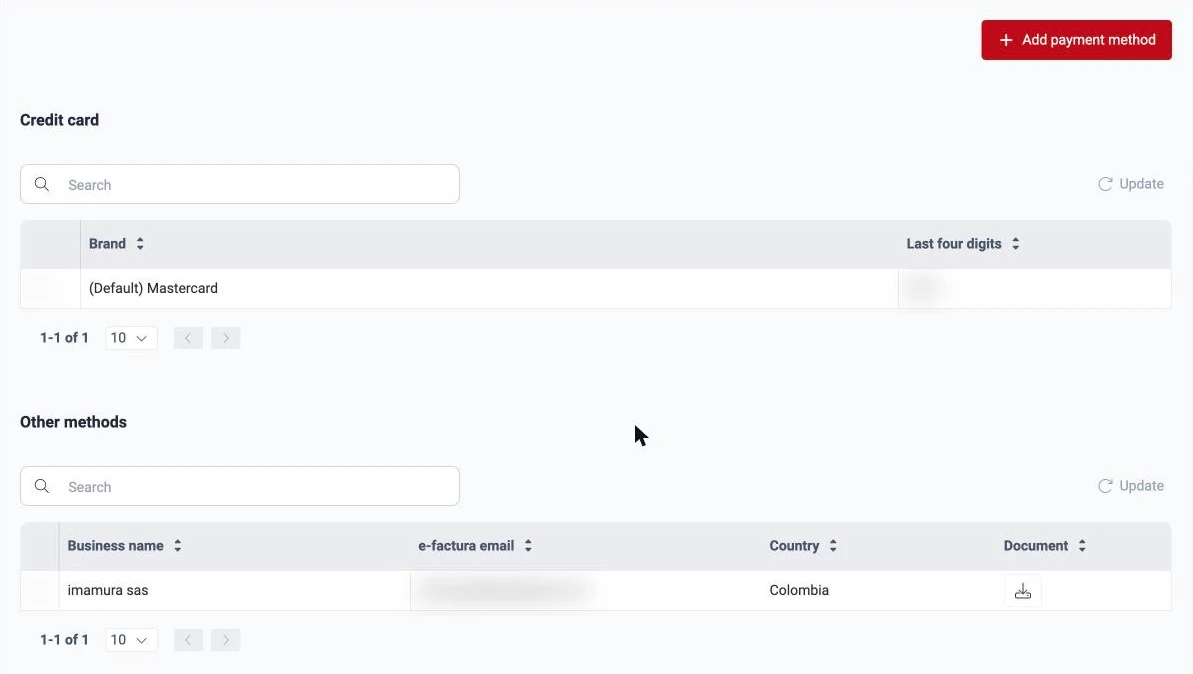
In this tab, you can do these actions:
- Add payment method: Under Select payment method, select Credit card or Other. Then, select the country. For a credit card, Colombia uses ePayco, and other countries use Stripe. For Other, give the business name, the state, and the city. For Colombia, also give the email address. Then, upload the RUT (the tax ID document of Colombia). For other countries, upload the tax ID document.
- Update: On a credit card, this action replaces the card with a new one. On a different payment method, this action changes the business data and the documents.
- Remove: To remove a payment method, contact your Customer Manager. An organization must keep at least one payment method.
When you add a new credit card, it replaces the credit card that your organization has at this time.