CVSSF metric
Last updated: Nov 4, 2026
Some organizations think that a small number of security vulnerabilities is a reason for peace of mind. But the number of security issues is not the important value. The important value is the risk exposure that these issues represent.
For example, an application has ten vulnerabilities with a CVSS score of 1.0. These vulnerabilities do not represent the same risk exposure as one vulnerability with a score of 10.0.
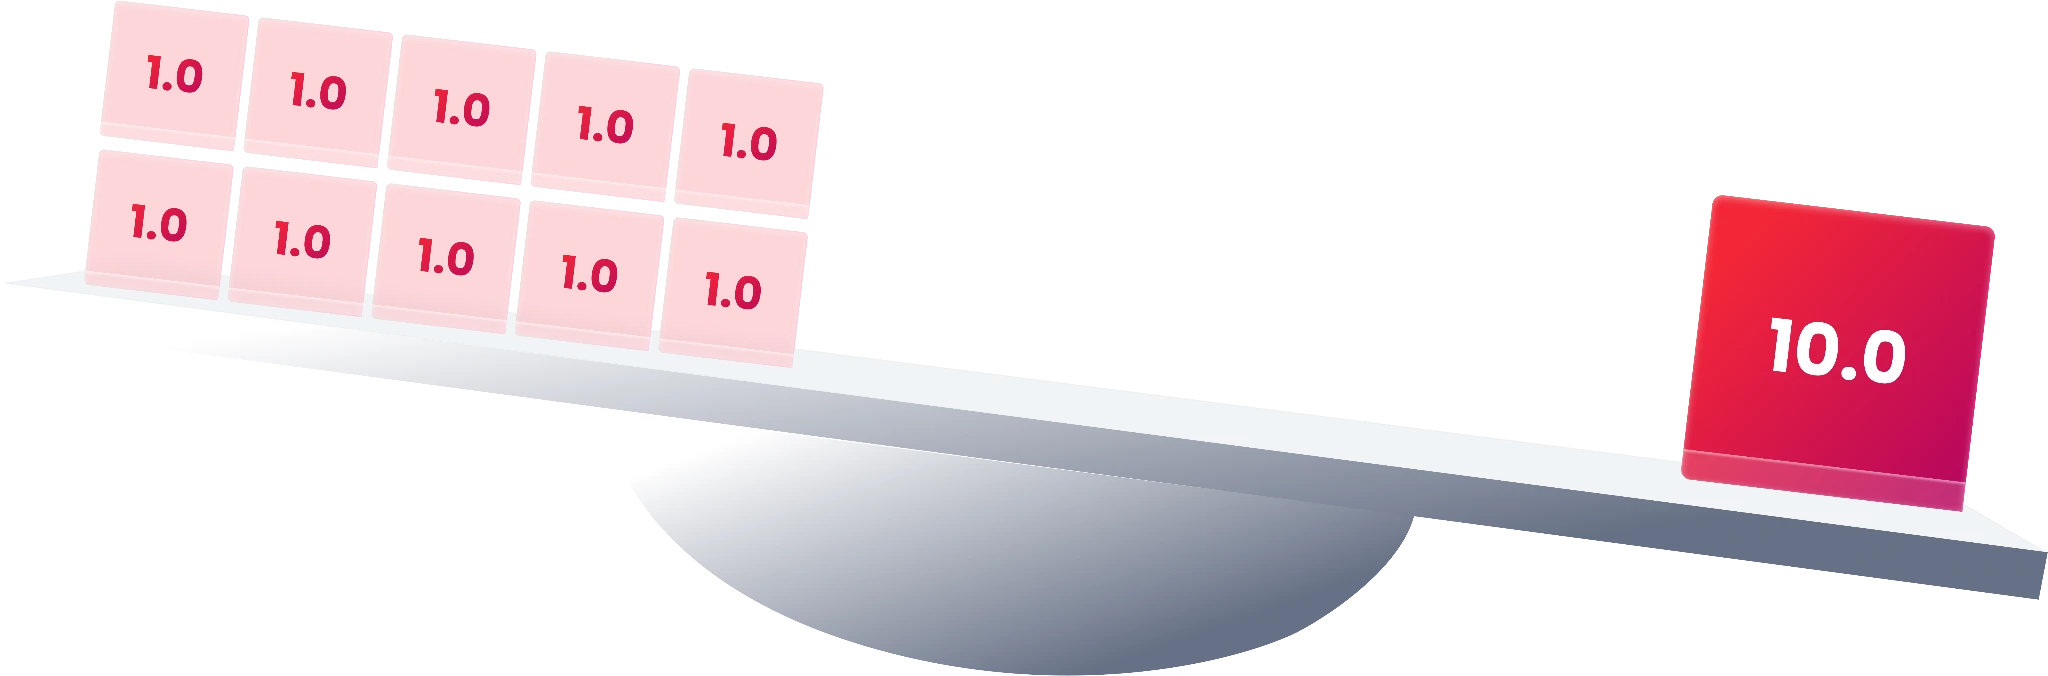
Fluid Attacks created a metric called CVSSF to help organizations prioritize the remediation of their vulnerabilities. The CVSSF metric uses this equation: CVSSF = 4^(CVSS-4). The CVSS value in the equation is the CVSS-BT score of the vulnerability. CVSSF shows a larger difference between values than CVSS. Thus, the vulnerabilities of an application that represent a higher risk exposure are easier to see.
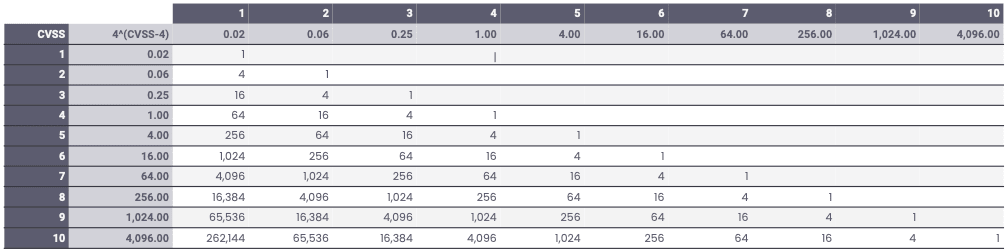
Apply the example above to the equivalences in the table below. When you multiply the quantity of vulnerabilities by their CVSSF score, you do not get the same result of 10.0 that you get with CVSS. The results are 0.2 (10×0.02) on one side and 4,096 (1×4,096) on the other. This large difference is possibly closer to reality.
To learn why Fluid Attacks created the CVSSF metric, read the CVSSF entry on the website.
CVSS-BT score
Learn how Fluid Attacks uses CVSS-BT v4.0 to score the severity of vulnerabilities, and how the Exploit Maturity metric changes the score.
What is SAST?
Identify source code vulnerabilities early with the Fluid Attacks SAST tool, which is recommended by the CASA framework and has a perfect OWASP Benchmark score.