GitLab Peer Reviewer Assistant
Last updated: Oct 27, 2026
Available only for cloud-hosted repositories. Fluid Attacks does not support on-premises installations of GitLab.
Steps to configure the GitLab Peer Reviewer Assistant integration
This guide gives the general steps to configure the GitLab Peer Reviewer Assistant integration in the Fluid Attacks platform. This integration lets an automatic peer reviewer analyze merge requests (MRs) in GitLab and add comments about security vulnerabilities.
To activate this integration, you must have the Maintainer or Owner role for the repository.
1. Initiate the integration within the Fluid Attacks platform
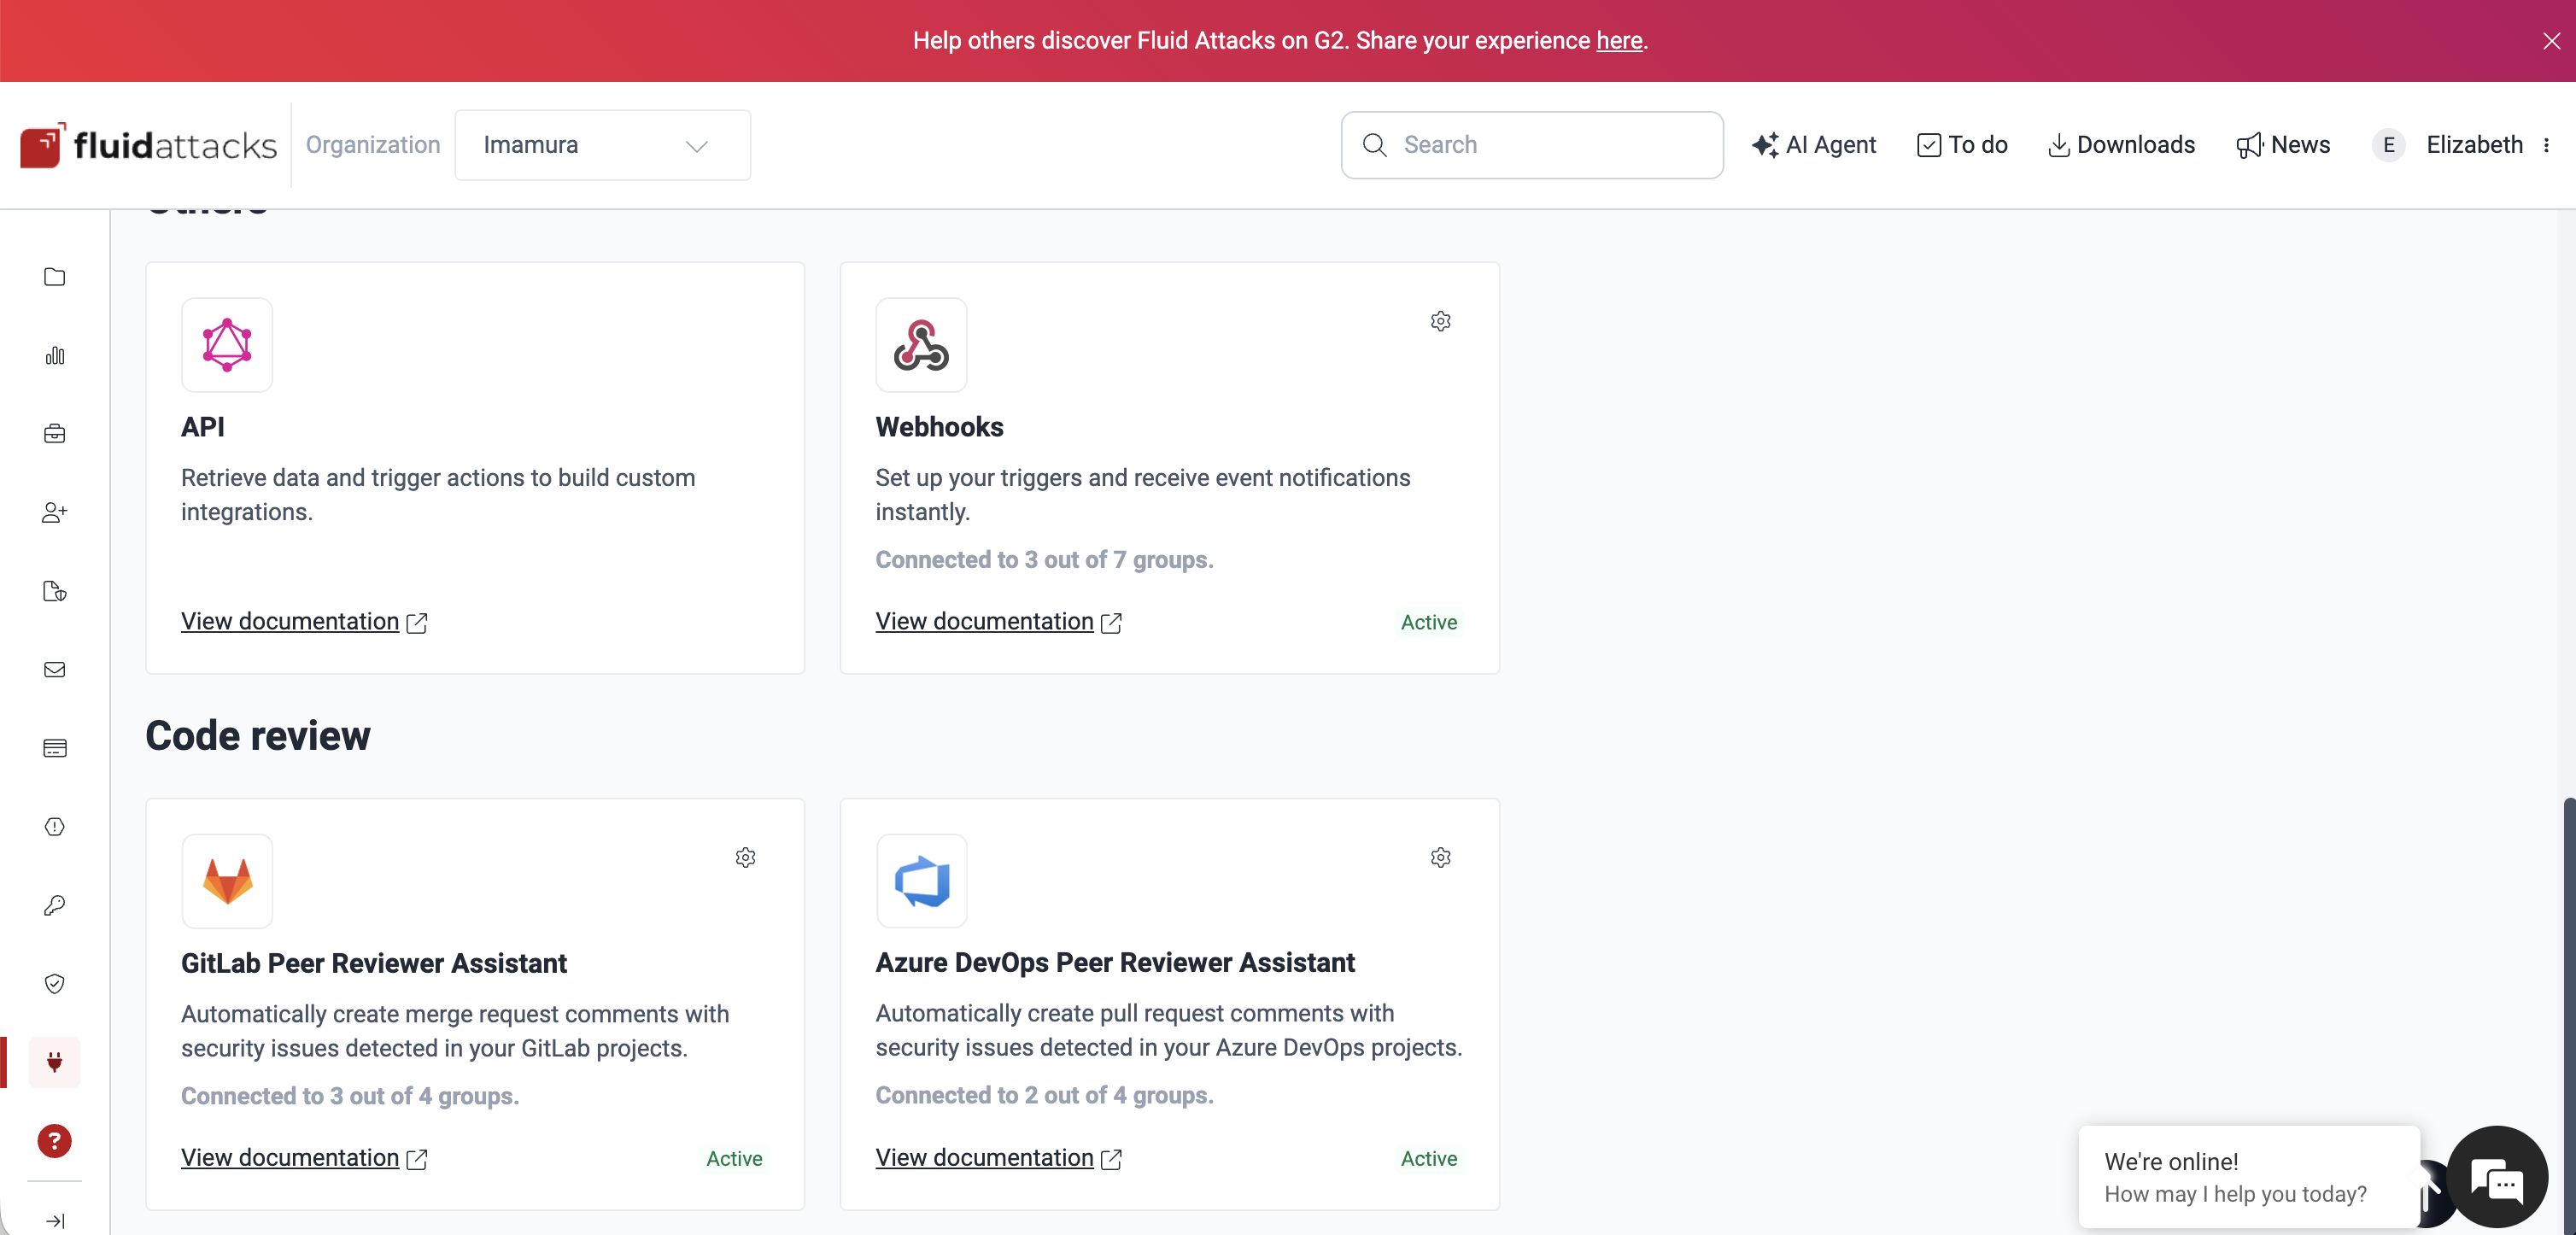
- Go to the Integrations section on the Fluid Attacks platform dashboard.
- Find the GitLab Peer Reviewer Assistant card.
- Click the Use integration button on the card.
2. Connect the integration to an organization group
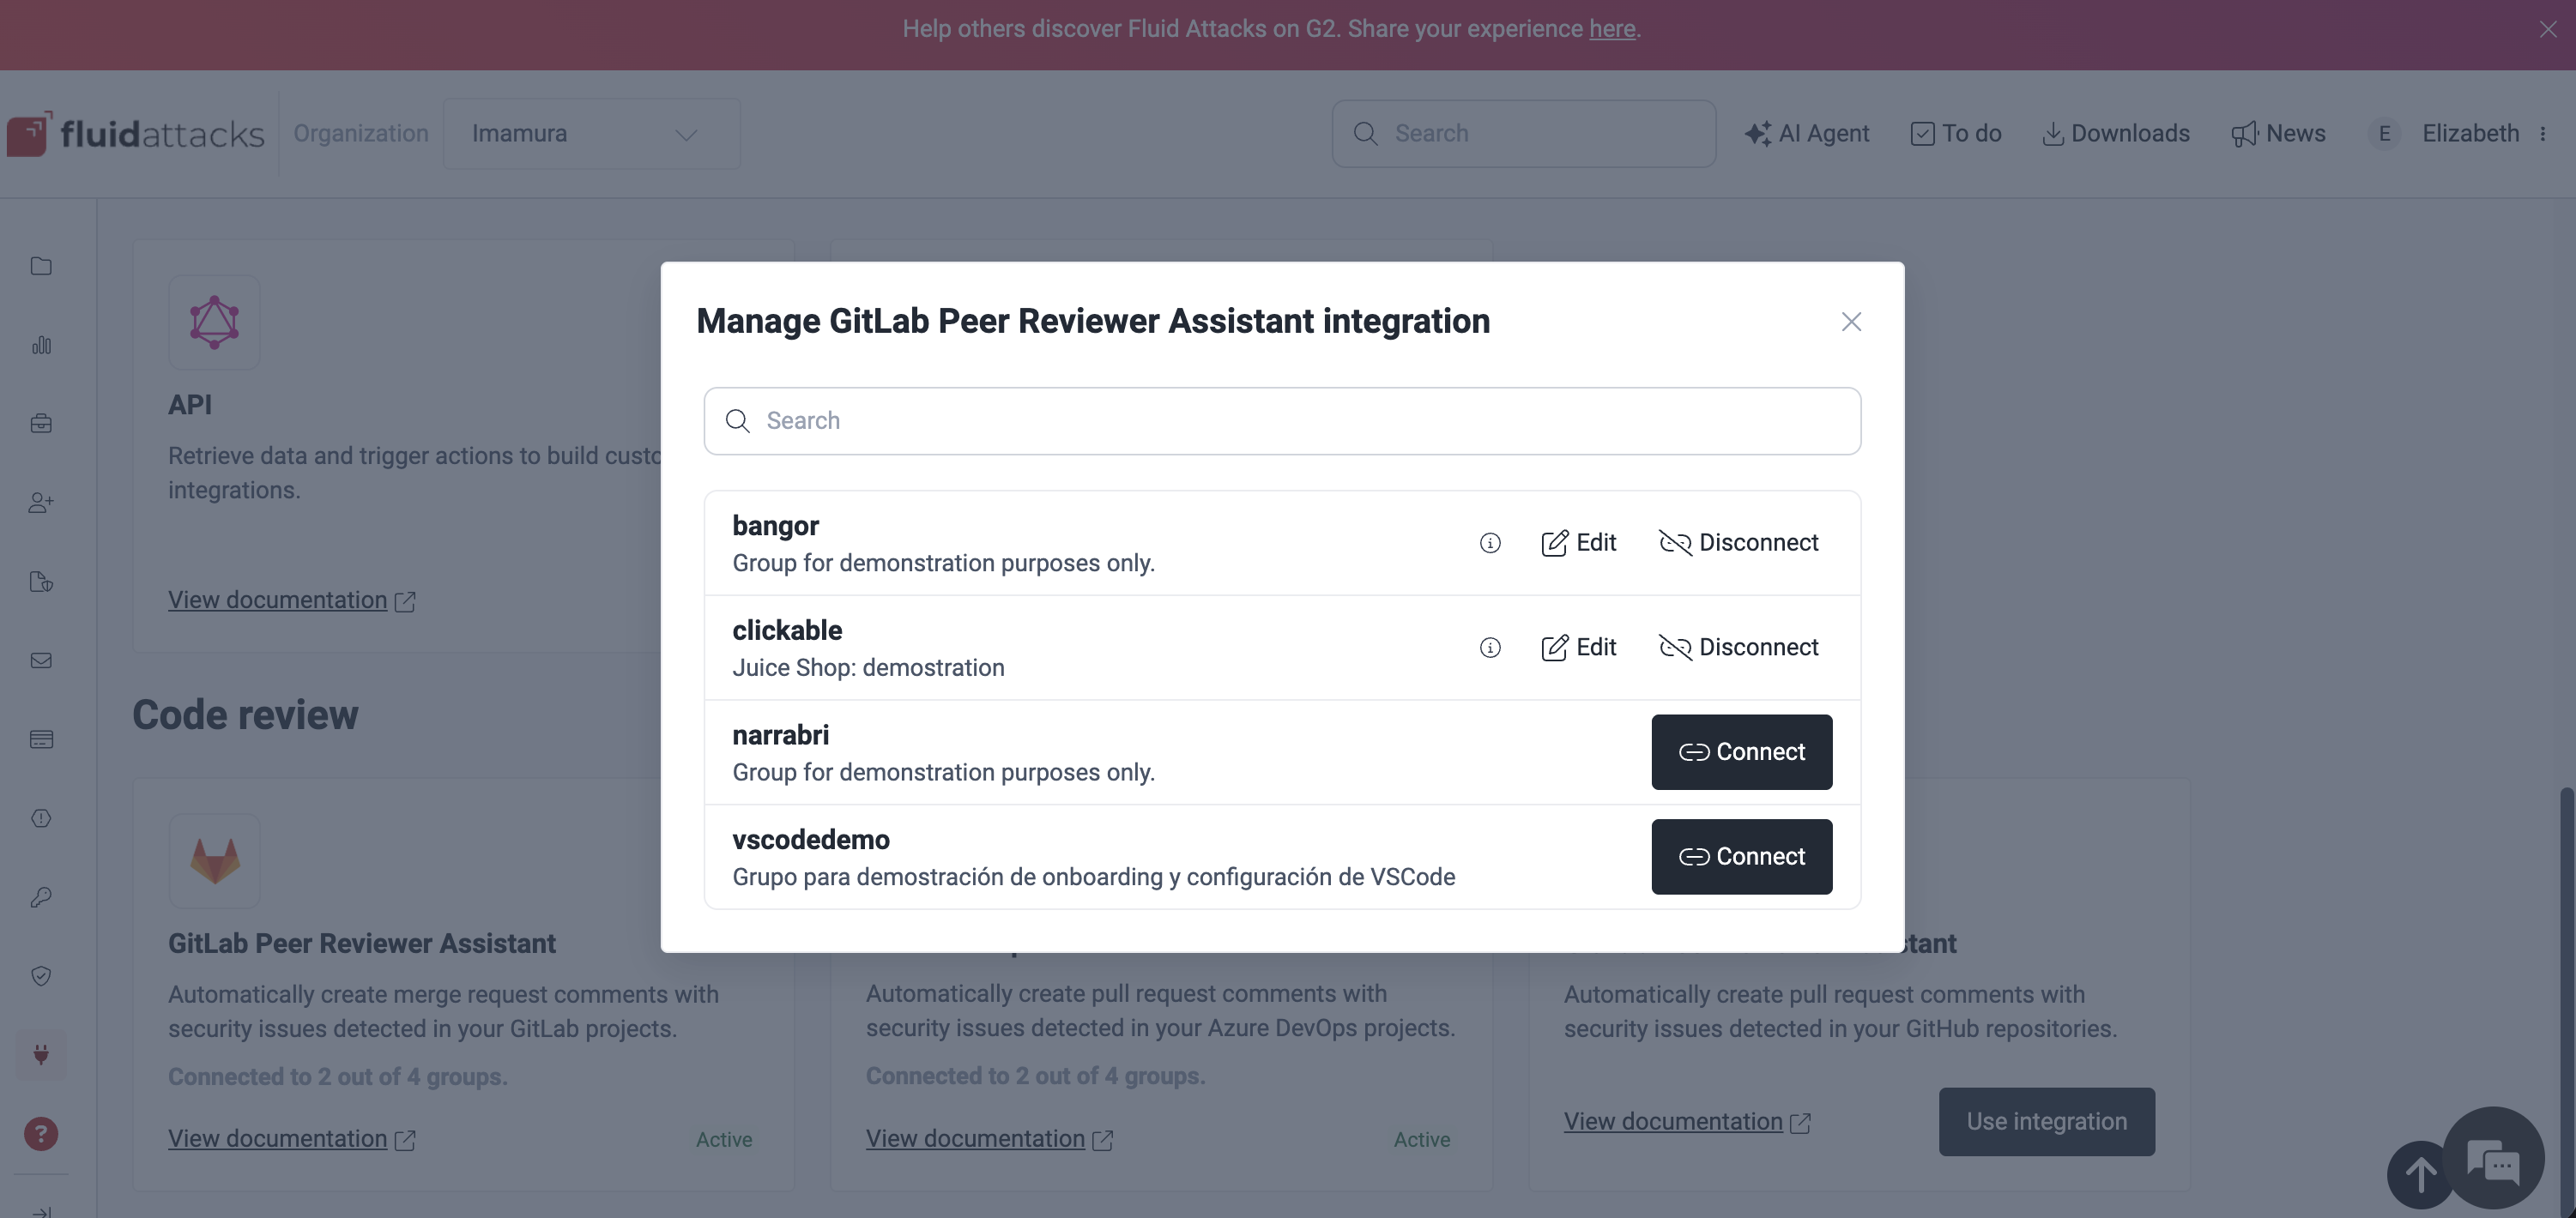
- A window with the title "Choose the Group you want to connect to GitLab Peer Reviewer Assistant integration" appears.
- Select the group in your organization that has the repositories that you want to scan.
- Click the Connect button next to the group that you selected.
3. Authorize the GitLab connection
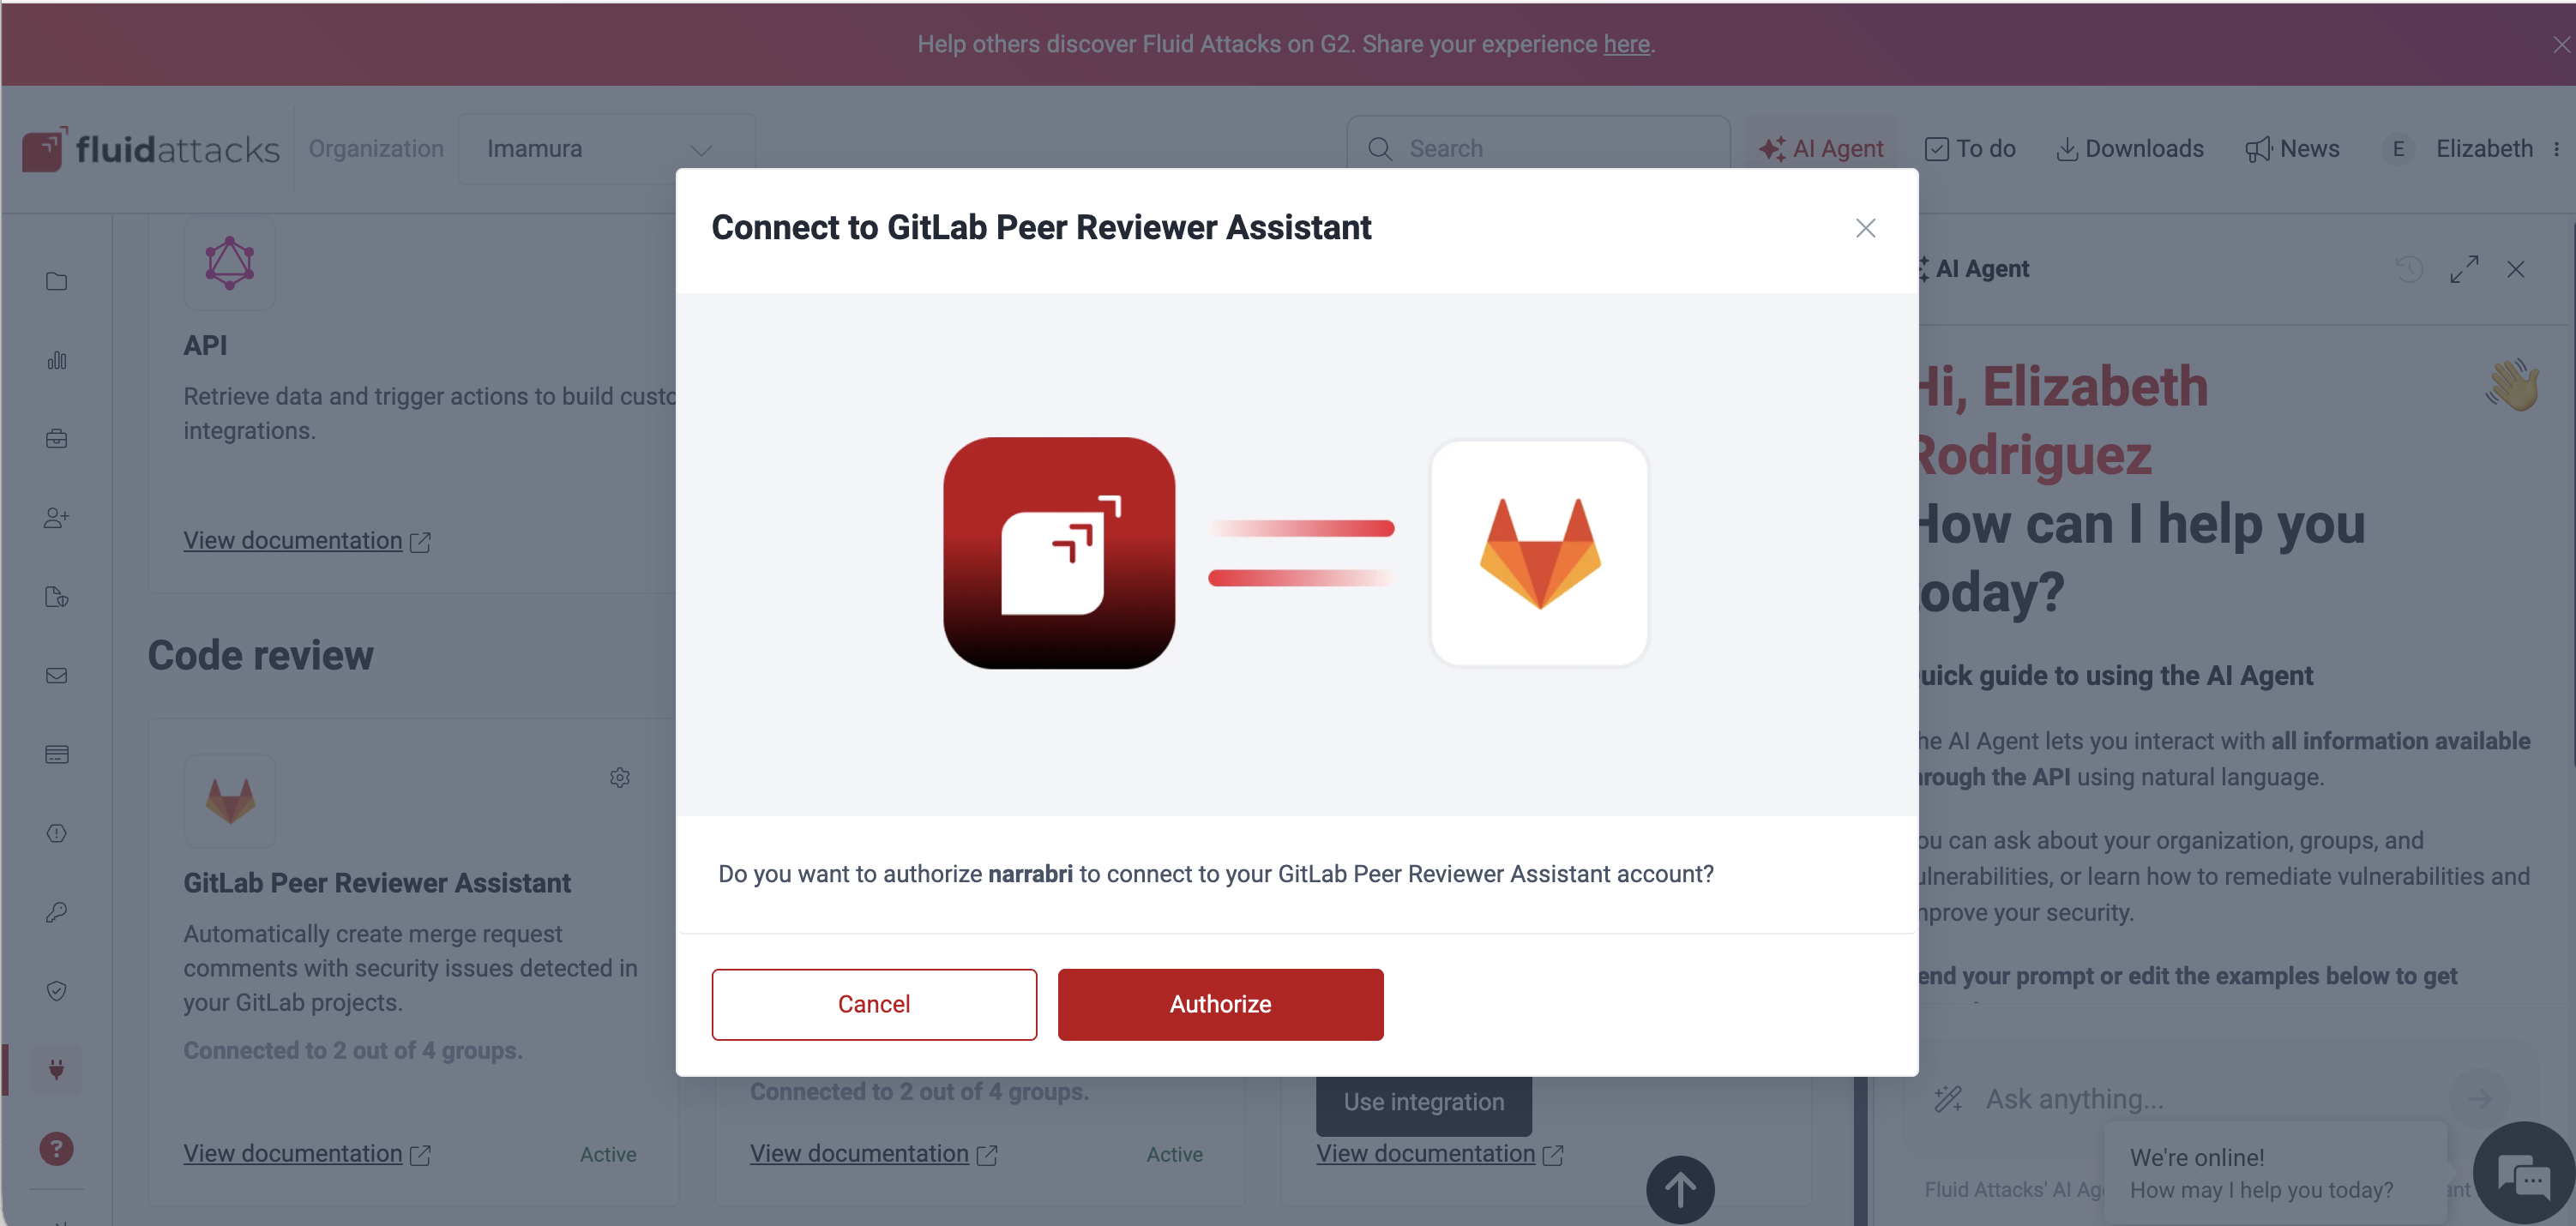
- The authorization dialog "Connect to GitLab Peer Reviewer Assistant" opens.
- Click the Authorize button.
- The platform sends you to GitLab for the OAuth authorization flow.
- Examine the requested permissions.
- Click the authorization button (for example, "Authorize Fluid Attacks - Peer Reviewer"). This gives Fluid Attacks access to your GitLab account.
4. Configure integration details
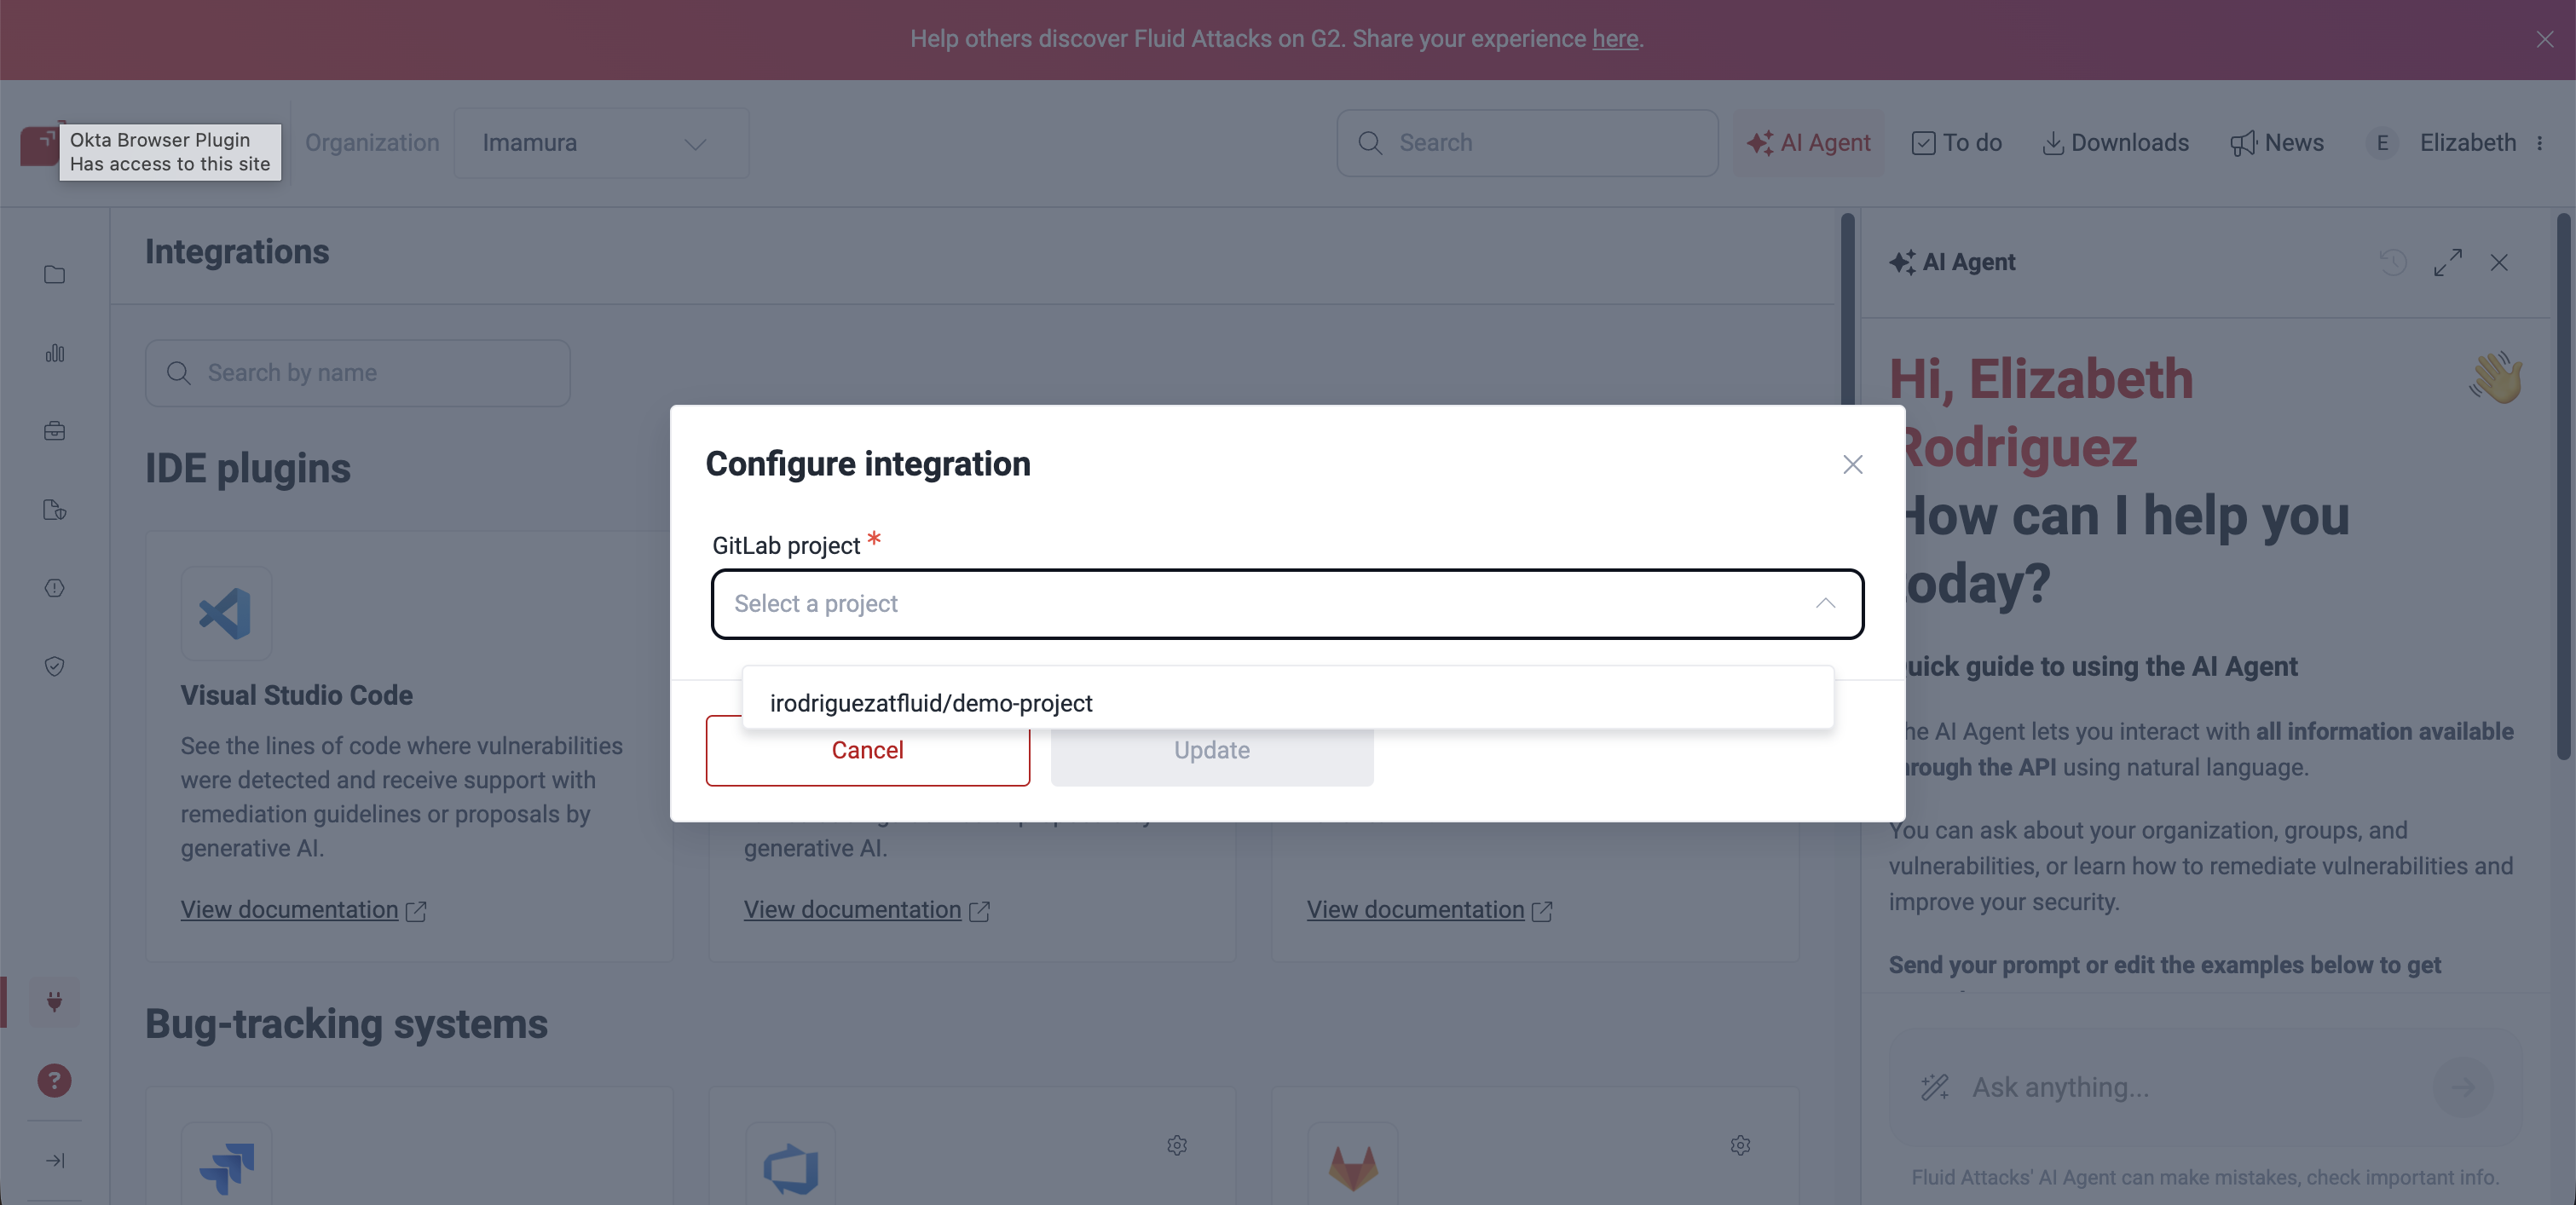
- After a successful authentication, the "Configure integration" dialog opens again in the Fluid Attacks platform.
- GitLab project: Select the GitLab project that the integration monitors.
- Click the Update button to complete the configuration.
- Confirmation: A success message, for example, "Success! You updated the integration set," shows that you completed the configuration.
Integration management and verification
Manage the connected integration
- Go to the GitLab Peer Reviewer Assistant card again.
- Click Edit (or the related management button) for the connected group.
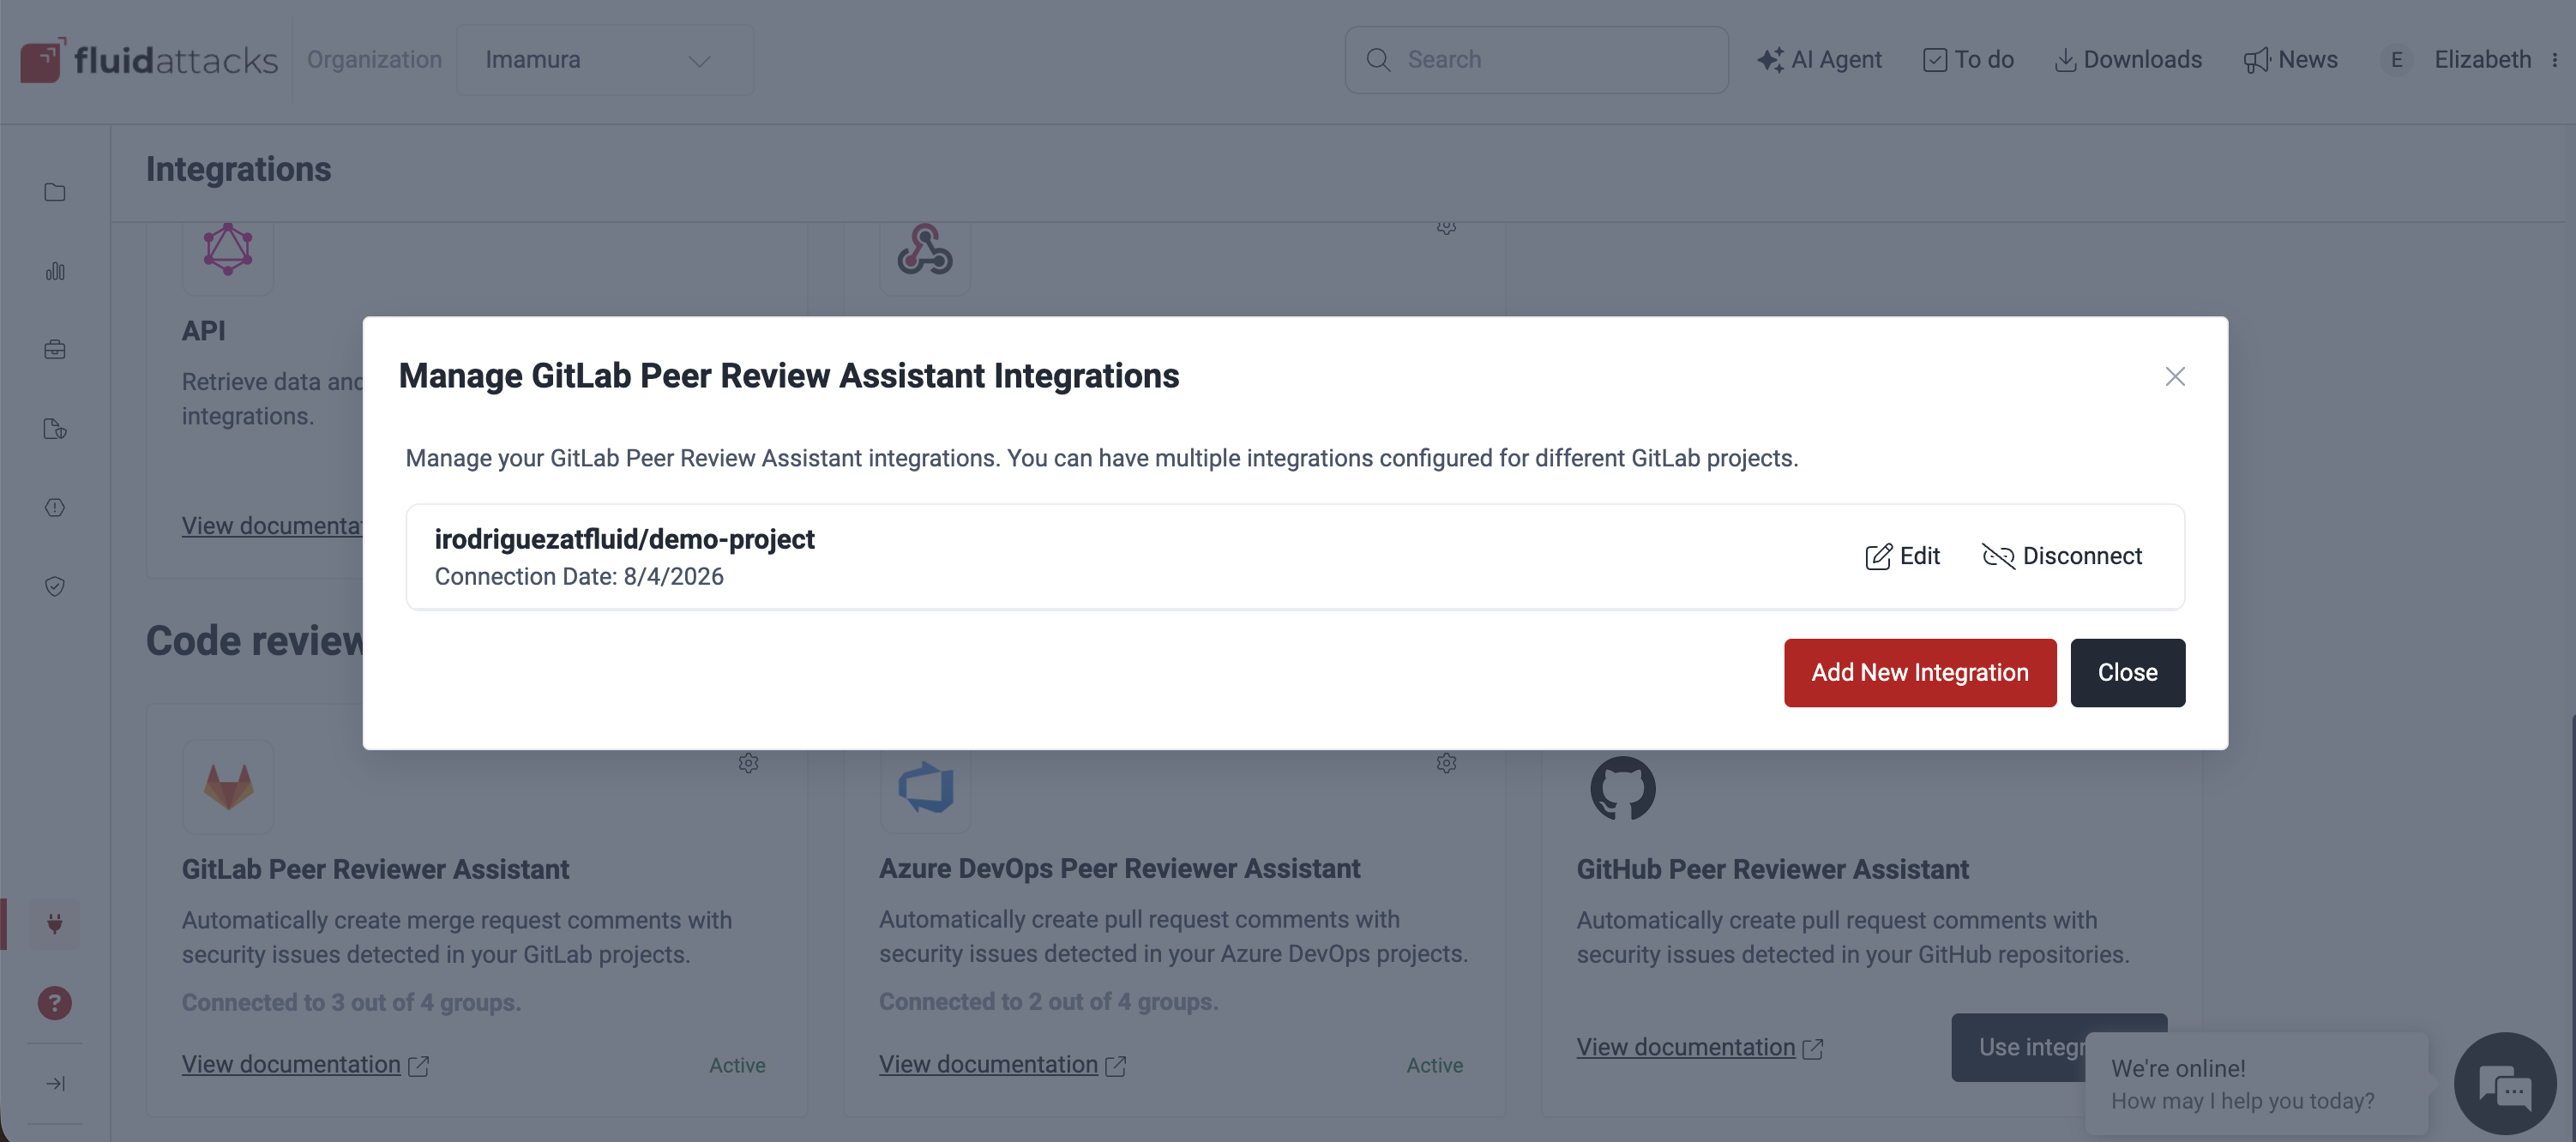
- The "Manage GitLab Peer Reviewer Assistant Integrations" window shows the connected repository and its details.
- From this screen, you can edit the configuration or disconnect the integration. You can also add a new integration for other repositories in the same group.
- Click Close to close the management window.
GitLab service hook verification (optional)
The integration automatically creates a WebHook in your selected GitLab repository. This hook subscribes to merge request events. When a user opens a merge request, the hook starts the Peer Reviewer Assistant. Thus the assistant analyzes each new MR.
Example: Review a GitLab merge request
This example shows a GitLab merge request. In the merge request, the assistant reviews new application code and reports a vulnerability. Then the developer remediates the code, and the assistant validates the updated changes.
1. Create or update a branch with code changes
A developer works in a source branch and introduces changes to the application.
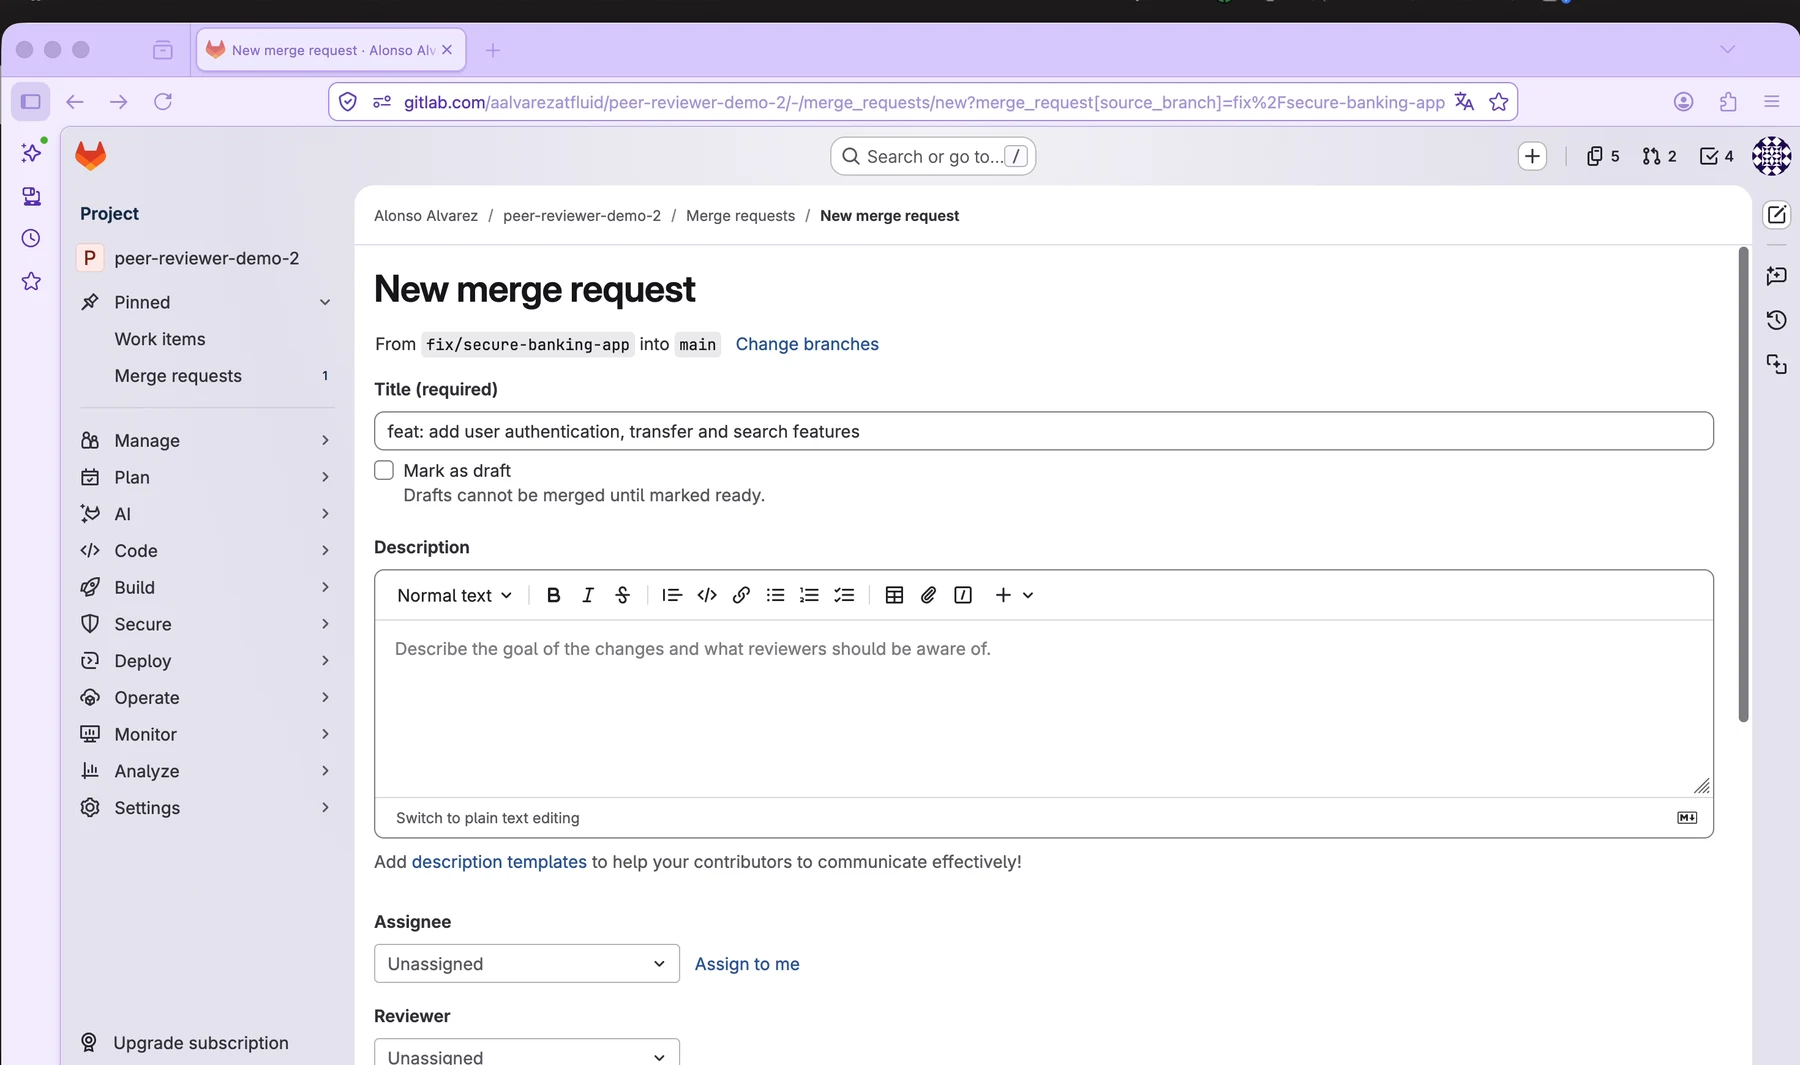
2. Open a merge request
In GitLab, the developer creates a merge request from the source branch into the target branch.
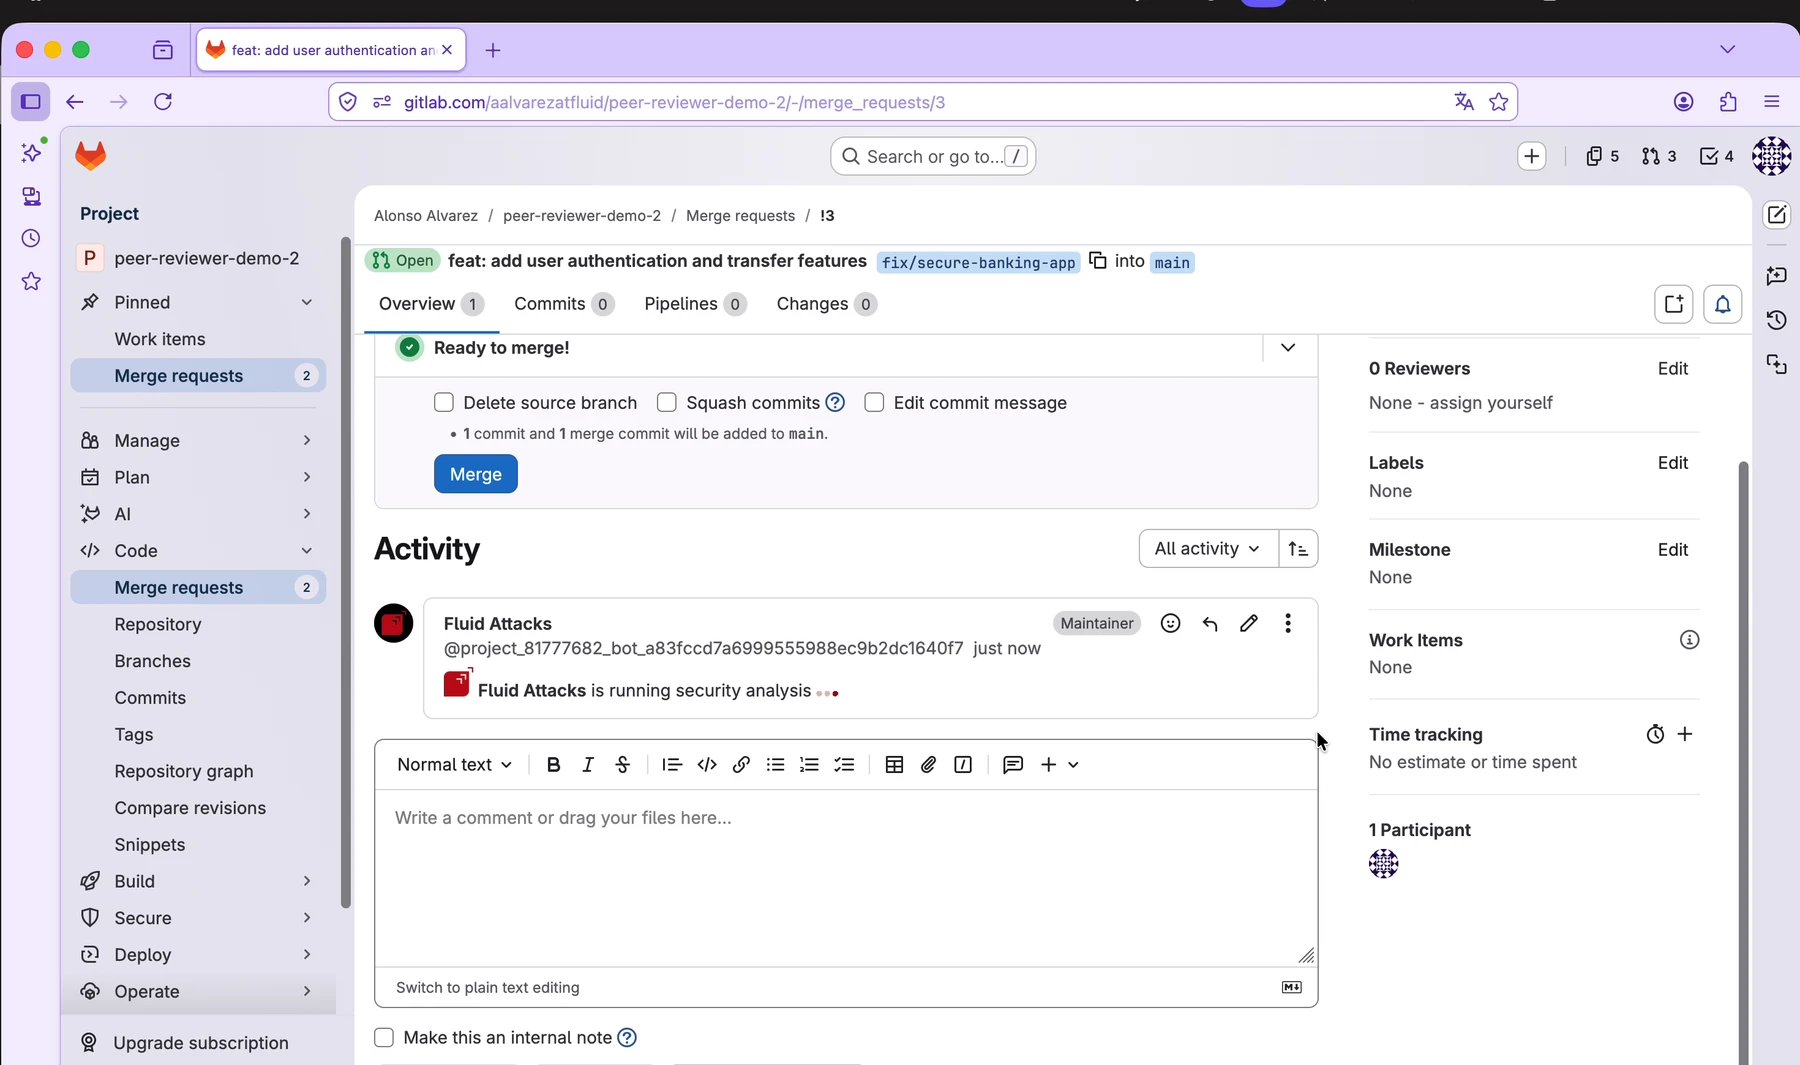
3. Wait for the assistant to analyze the changes
After the developer creates the merge request, Fluid Attacks starts the security analysis and posts an activity message in the merge request.
4. Review vulnerability comments
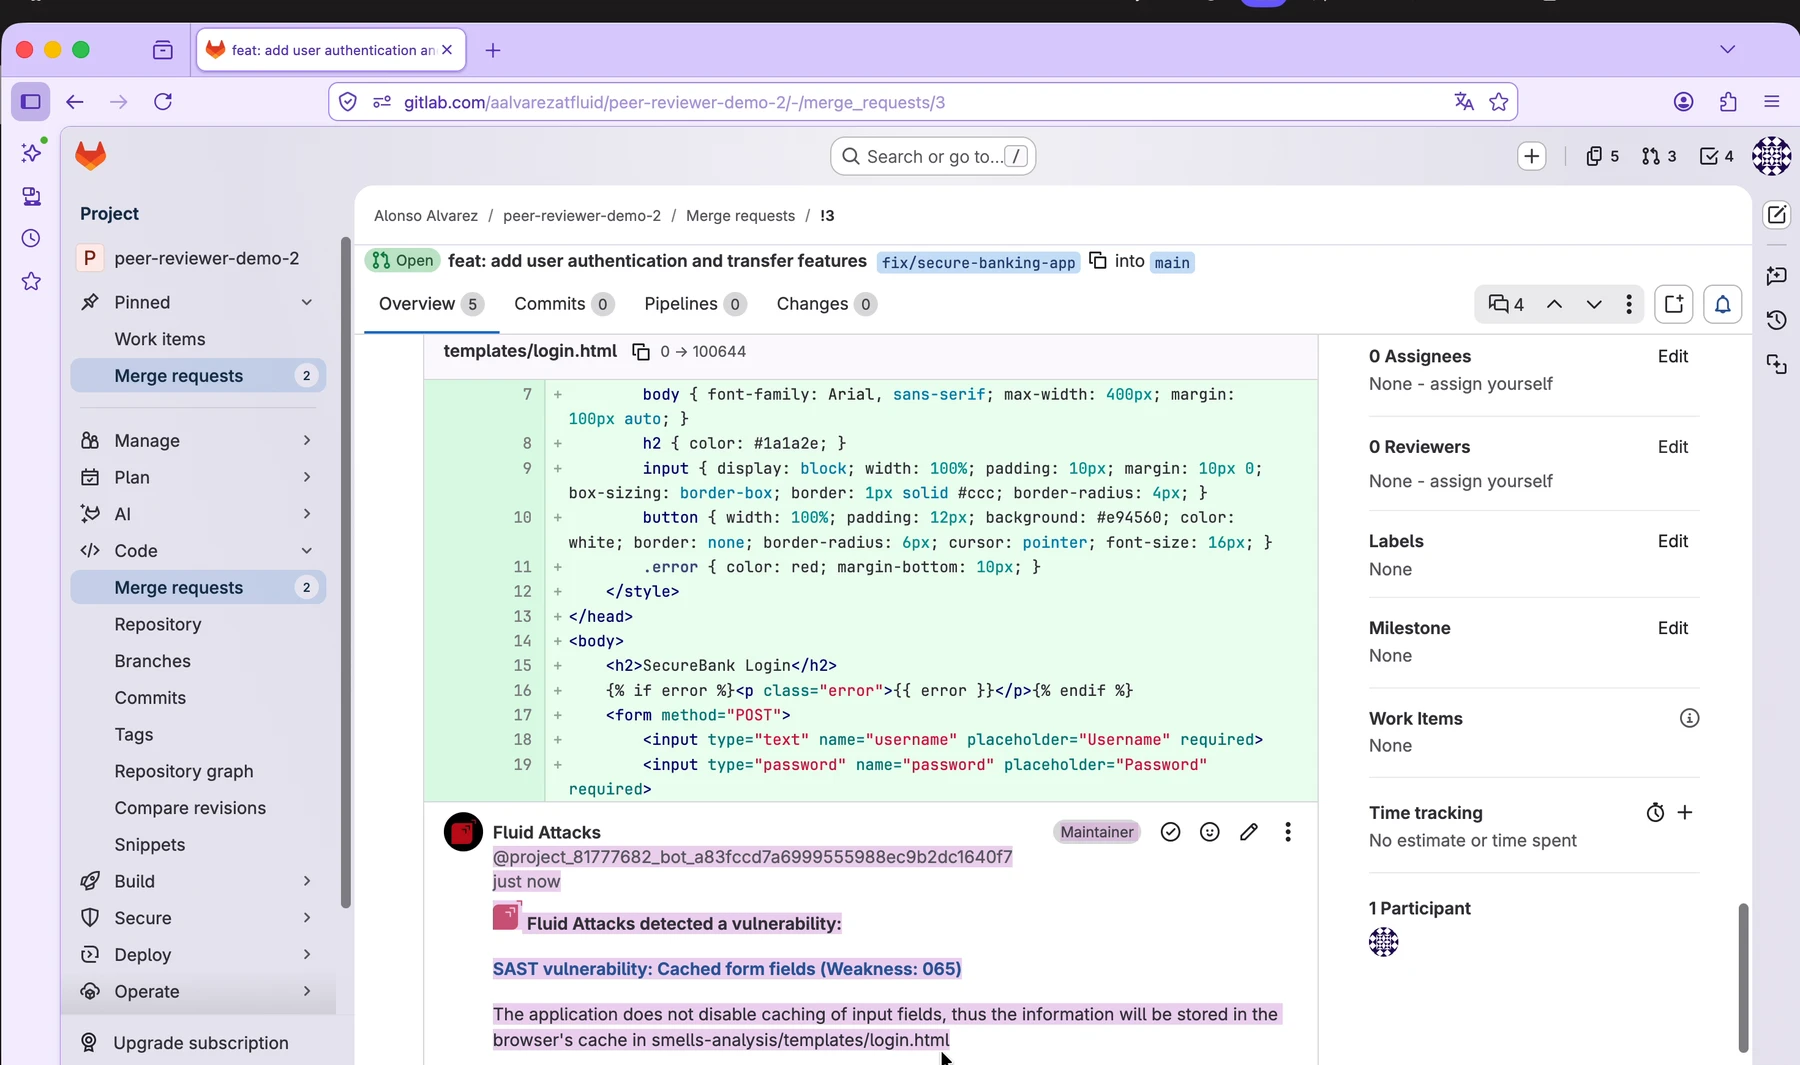
When the assistant detects a vulnerability, it posts a comment in the merge request. The assistant attaches the comment to the related context in the change set. Thus developers can review the vulnerability in the merge request.
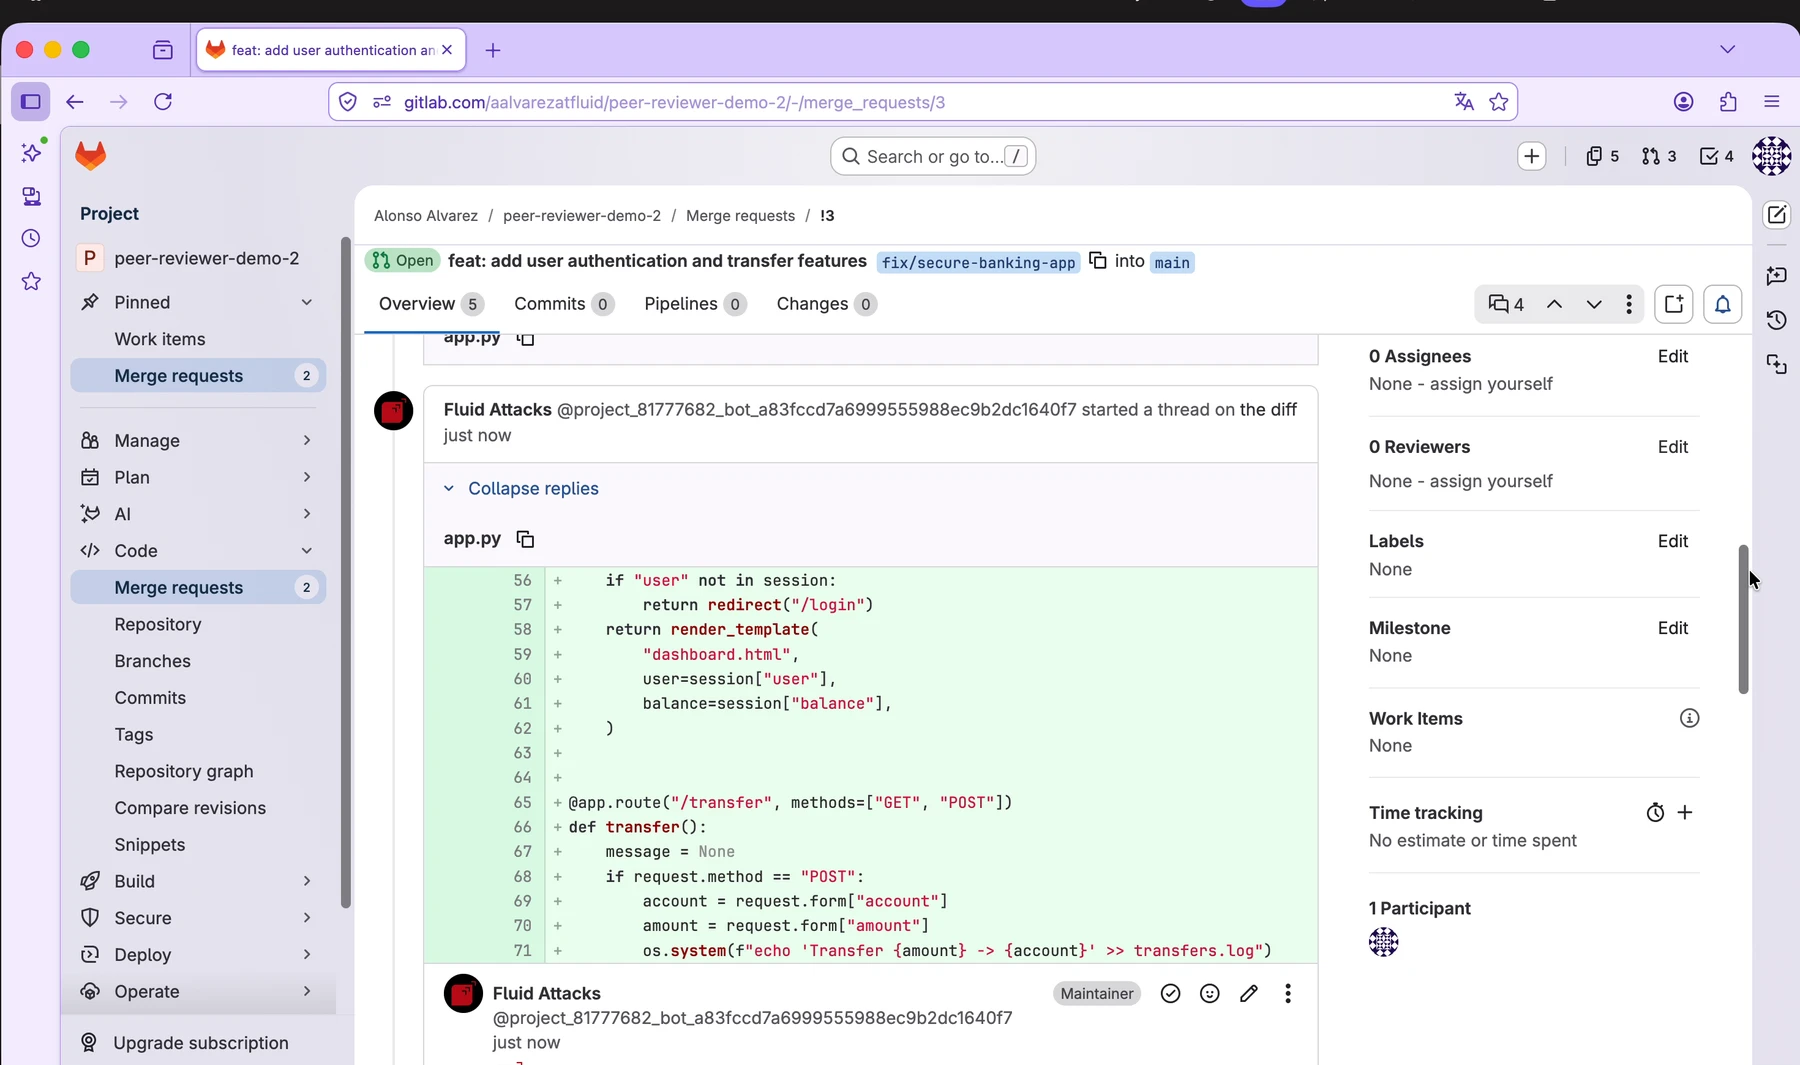
The assistant comment can include the vulnerability category, weakness identifier, affected location, explanation, and remediation guidance.
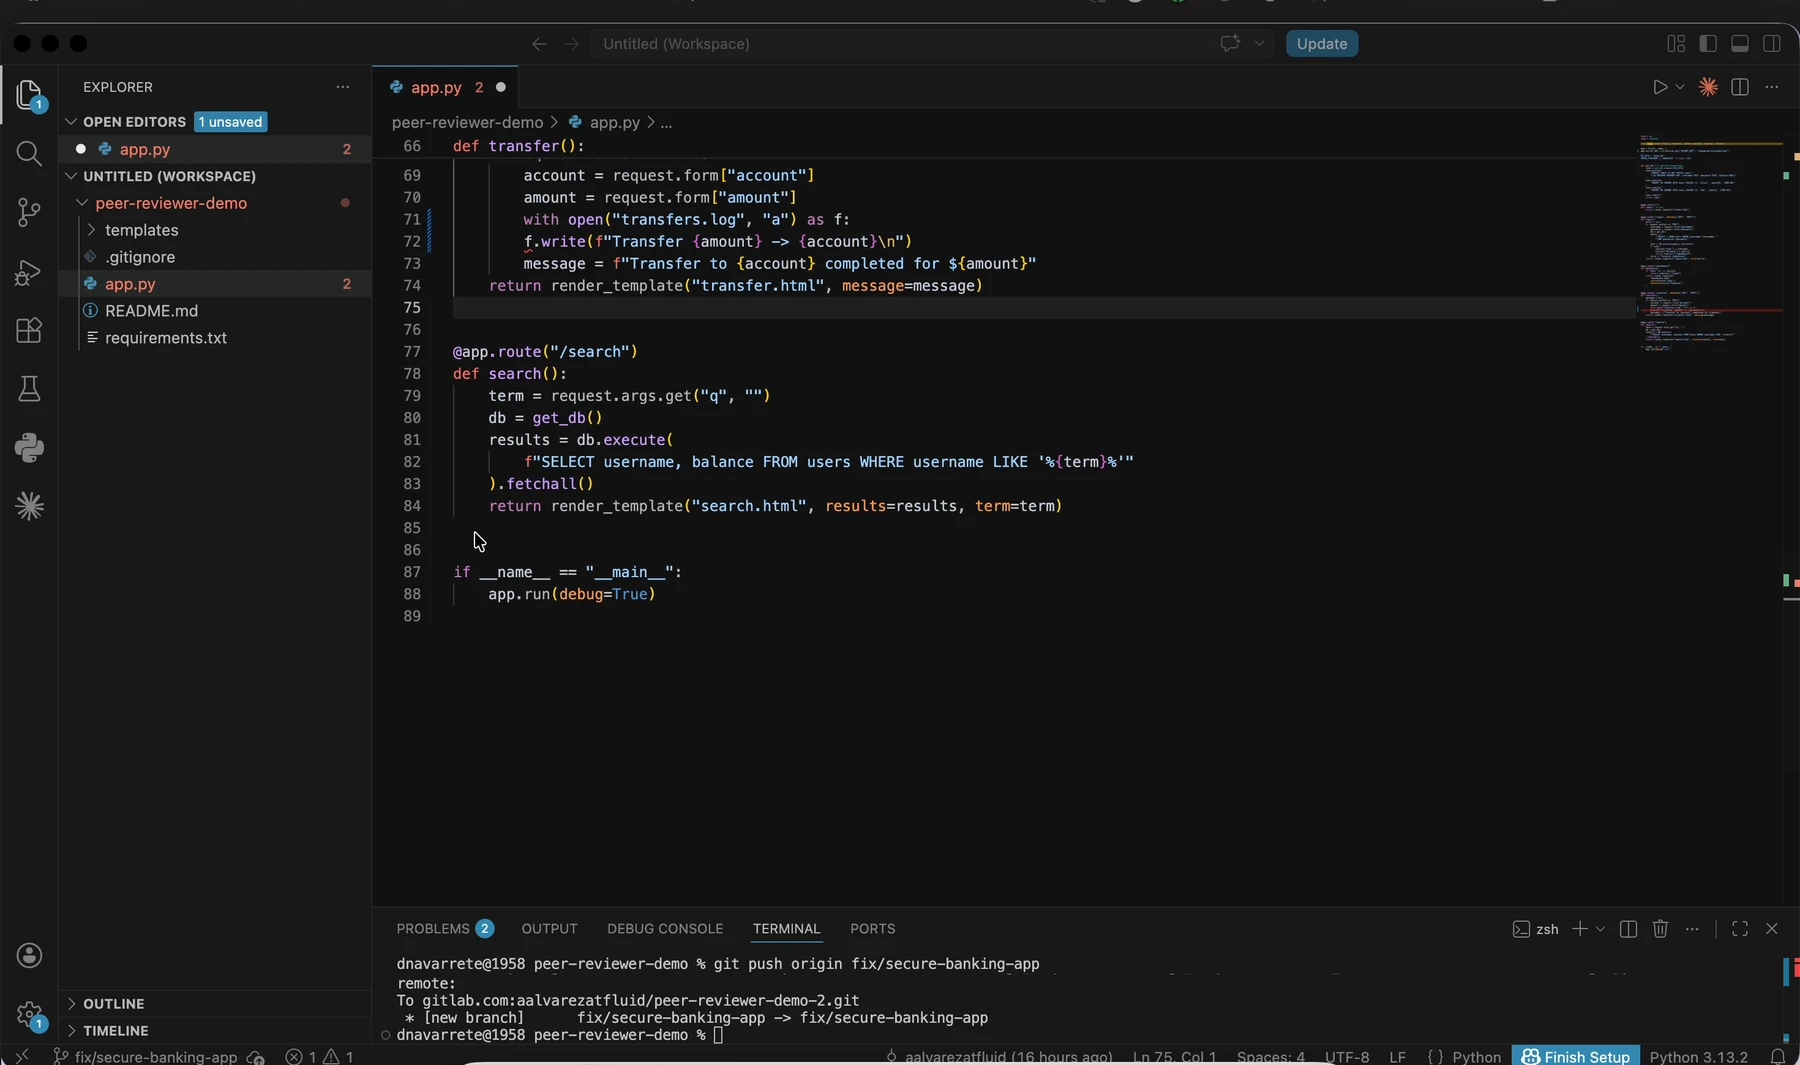
5. Remediate the issue
The developer makes the necessary code changes in the source branch.
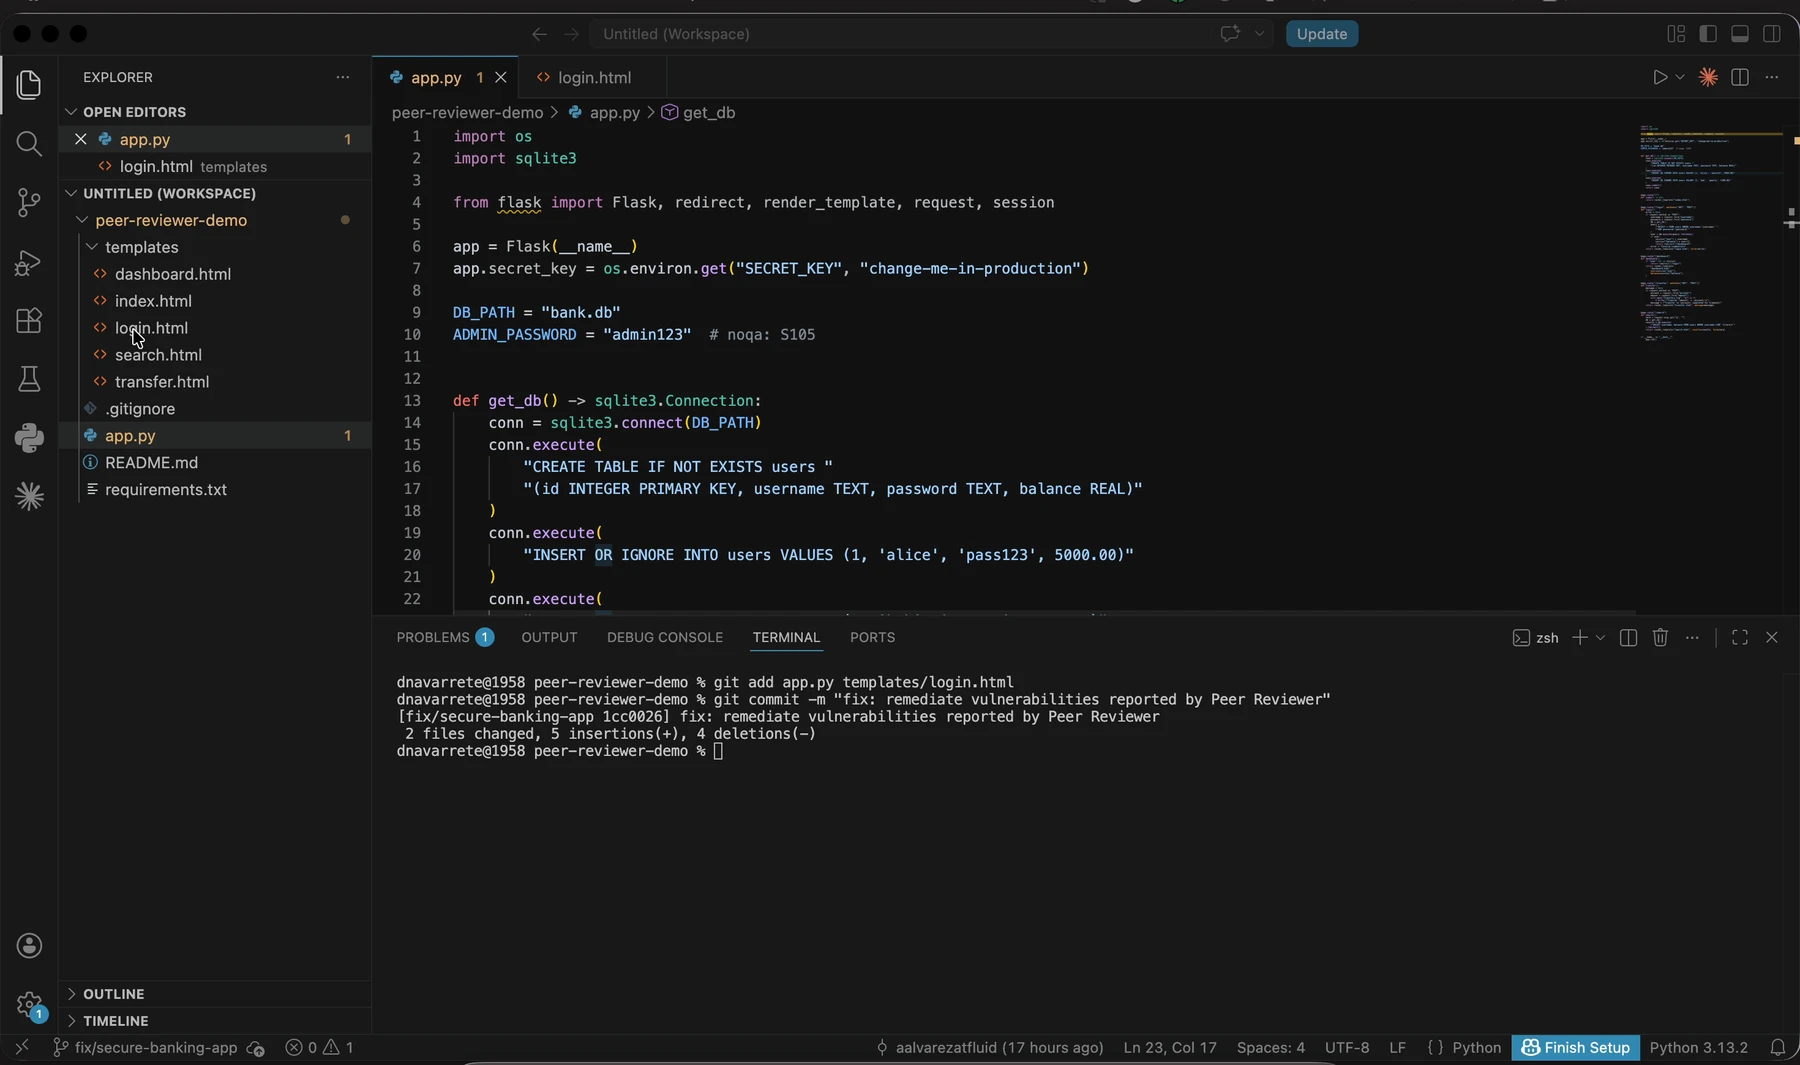
Then the developer commits and pushes the remediated changes to the remote branch.
6. Open a remediation merge request or update the existing one
The developer can compare the updated branch against the target branch again to continue the review.
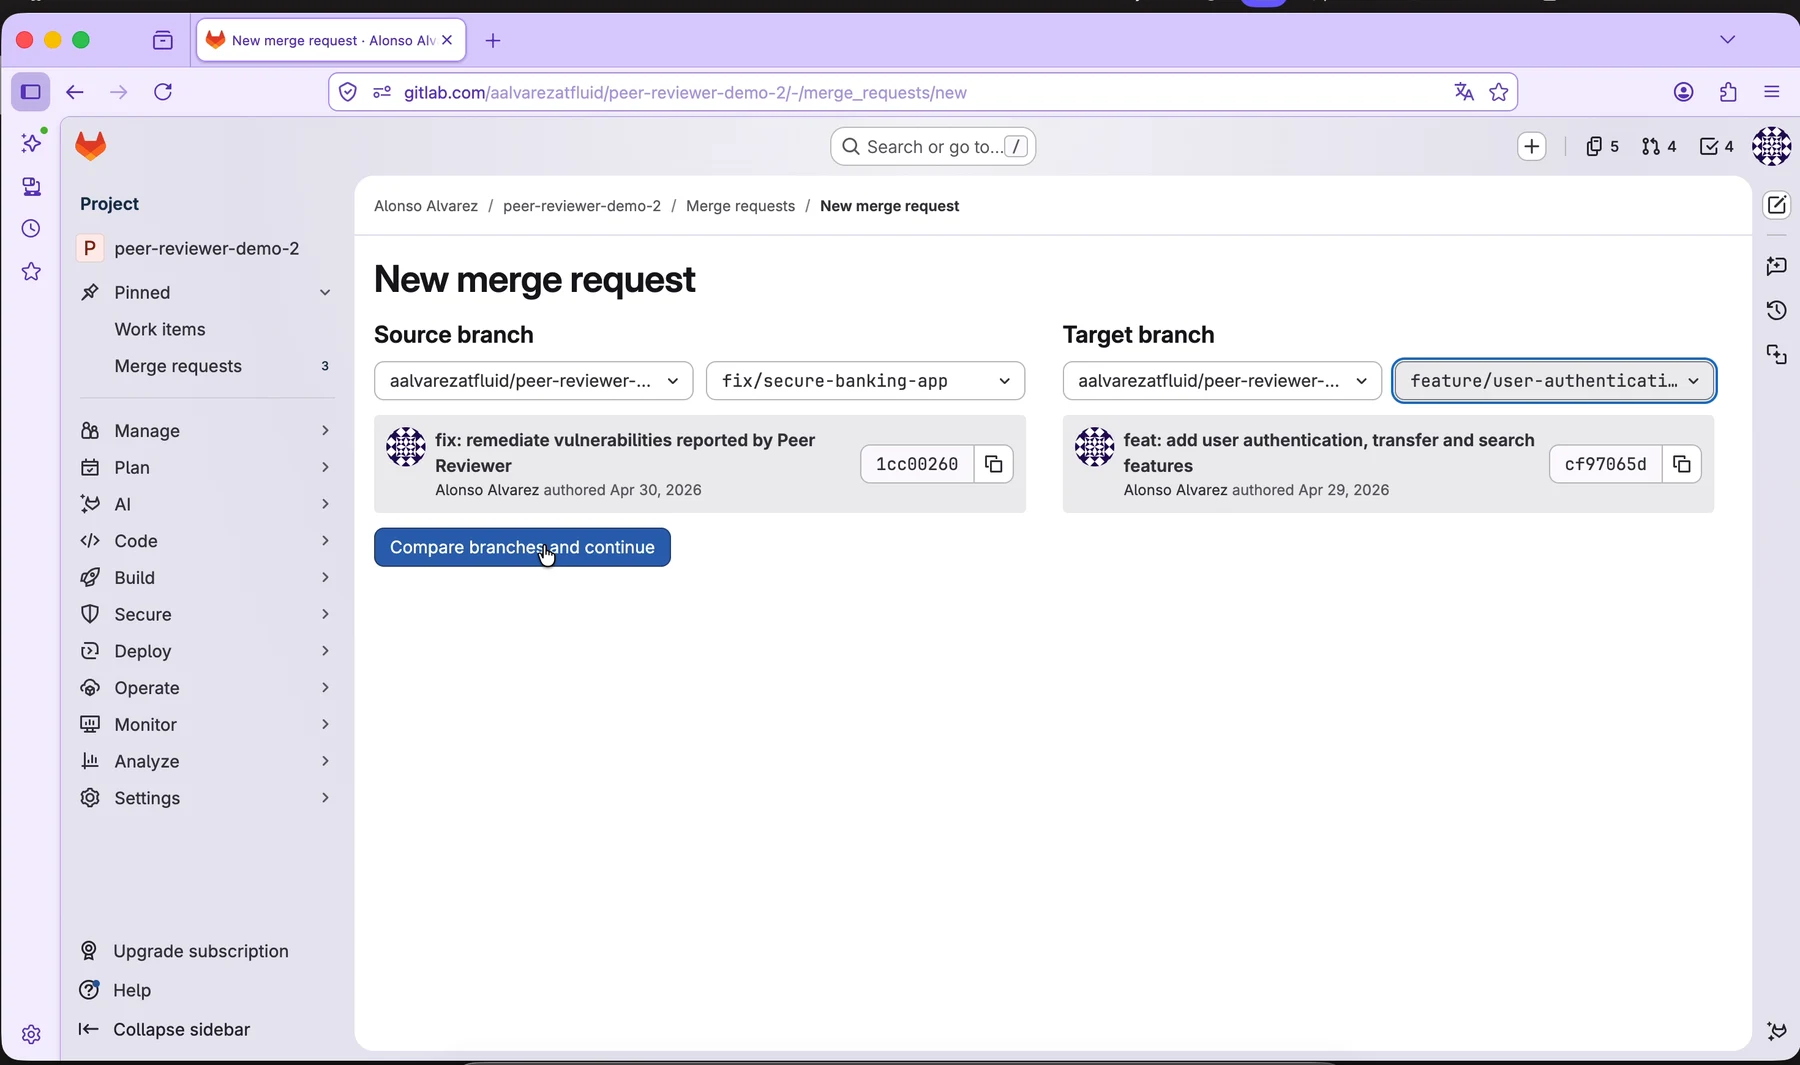
7. Validate the result
The assistant runs the security analysis again for the updated changes.
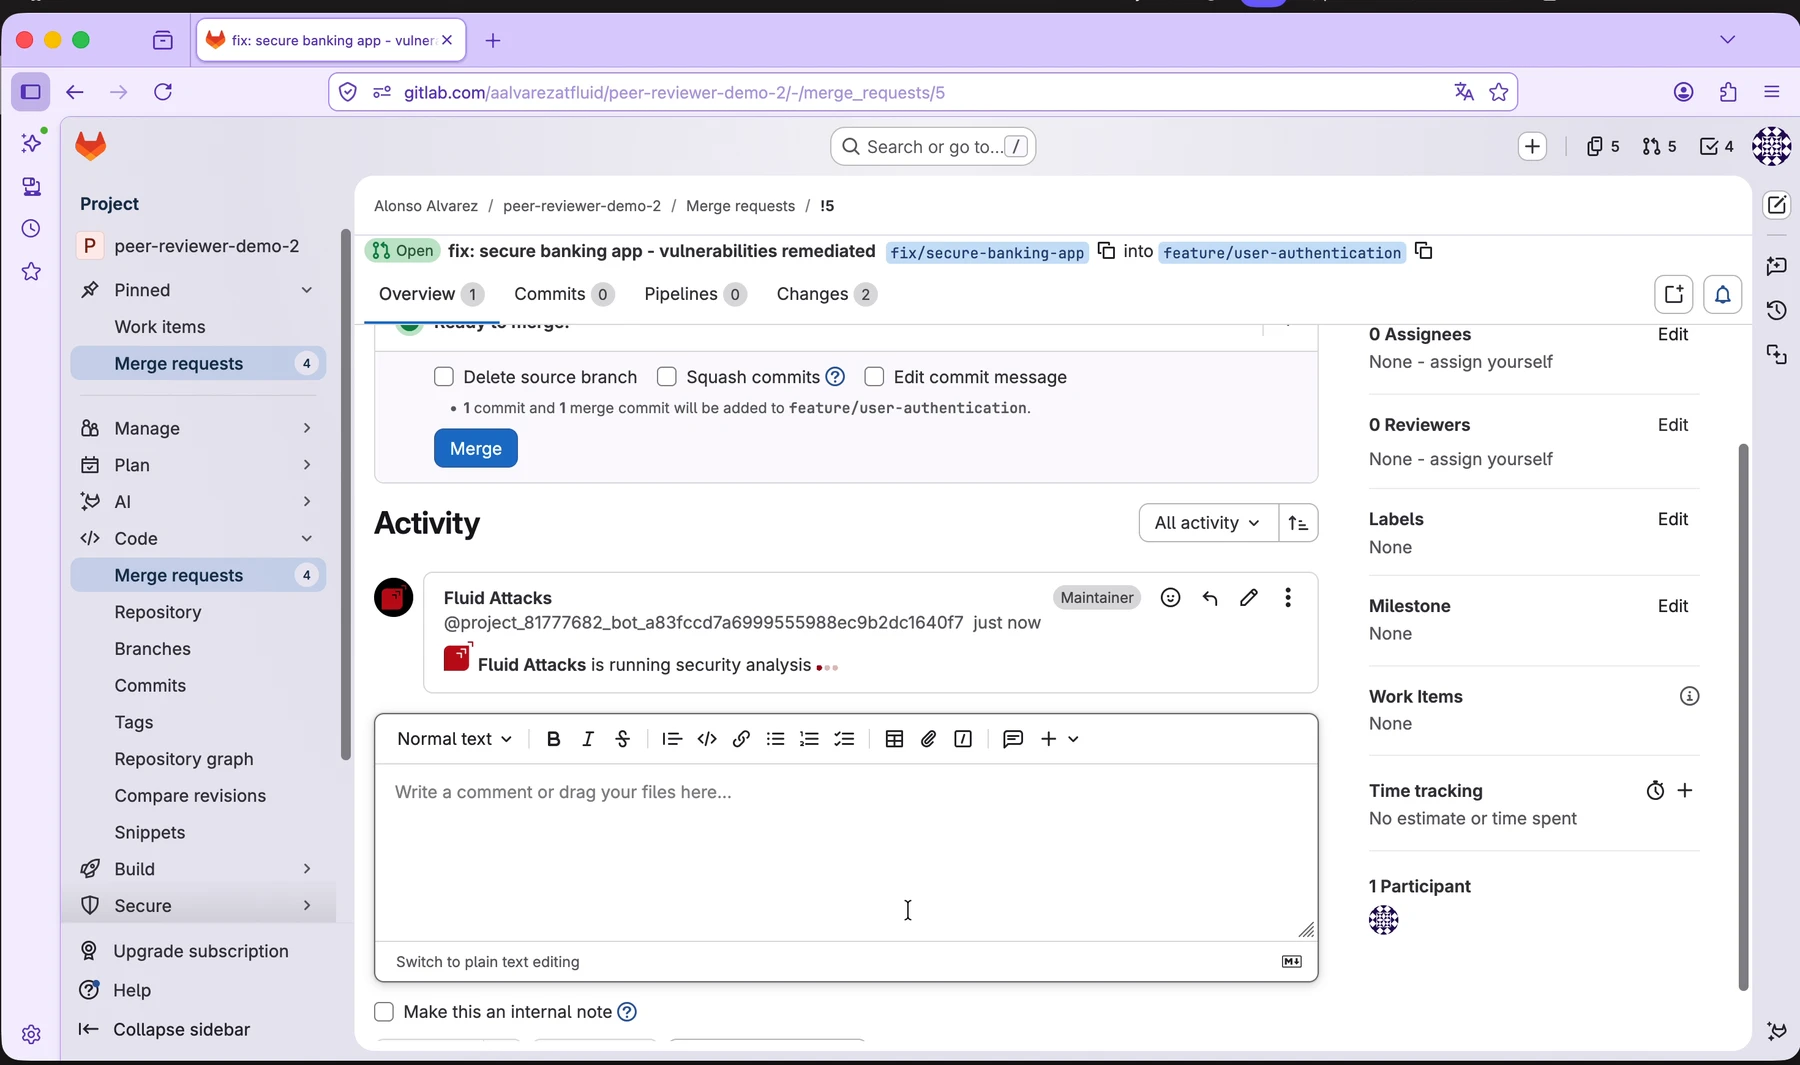
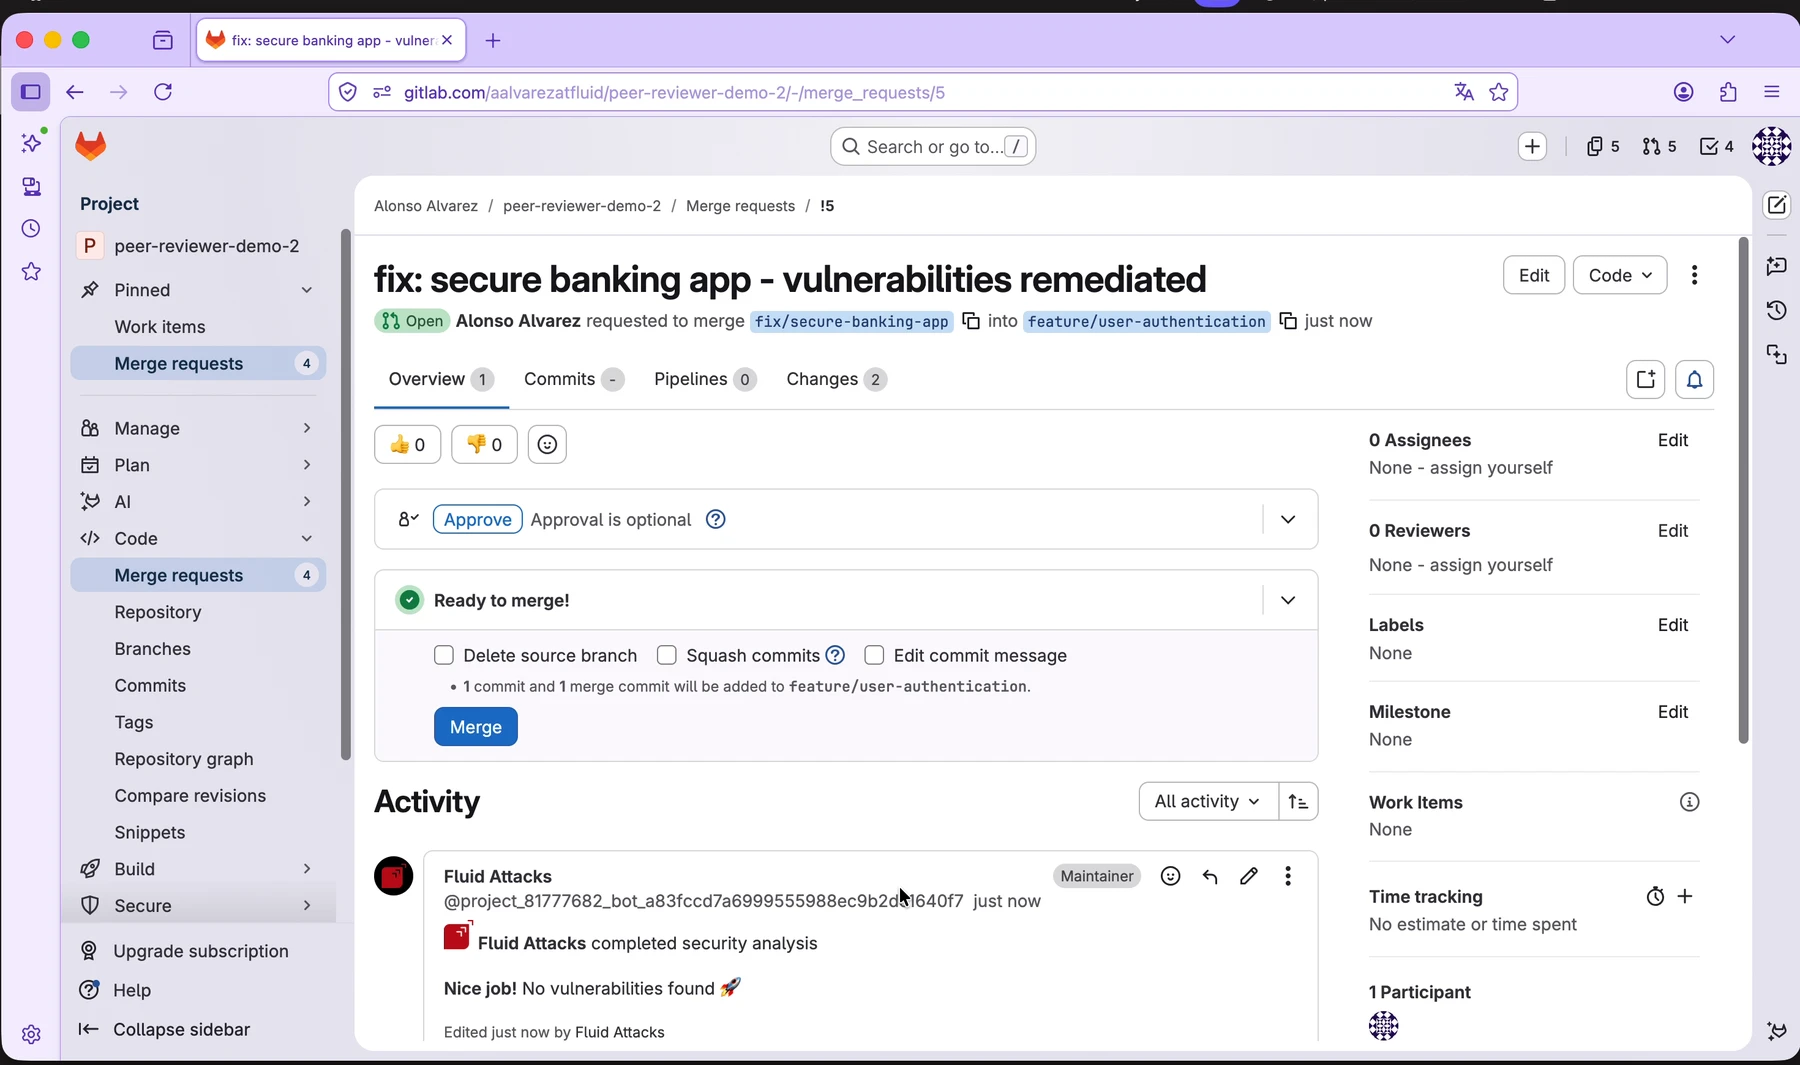
If the assistant does not detect vulnerabilities in the reviewed changes, it posts a message that it found no vulnerabilities.
There is also a guide to integrate with Azure DevOps.
GitHub Peer Reviewer Assistant
Install the Fluid Attacks GitHub App, select the groups that get their pull requests reviewed, and manage or disconnect the connection.
Azure DevOps Peer Reviewer Assistant
Connect your Azure DevOps organization, select the groups that get their pull requests reviewed, and manage or disconnect the connection.