Webhooks
Last updated: Nov 4, 2026
The webhooks of Fluid Attacks are not compatible with Google Chat and Slack.
On the Fluid Attacks platform, Group Managers can add custom HTTP callbacks with a URL (endpoint). The events that occur in the group start these callbacks. When an event occurs, the platform sends an HTTP request to the URL that you configured in the Integrations section. This request tells you that the event occurred. The platform sends notifications only for the events that you selected.
To configure webhooks for a group or to see the current webhooks, go to the Integrations section of your organization. Find Webhooks below Others. Then, click the gear icon.
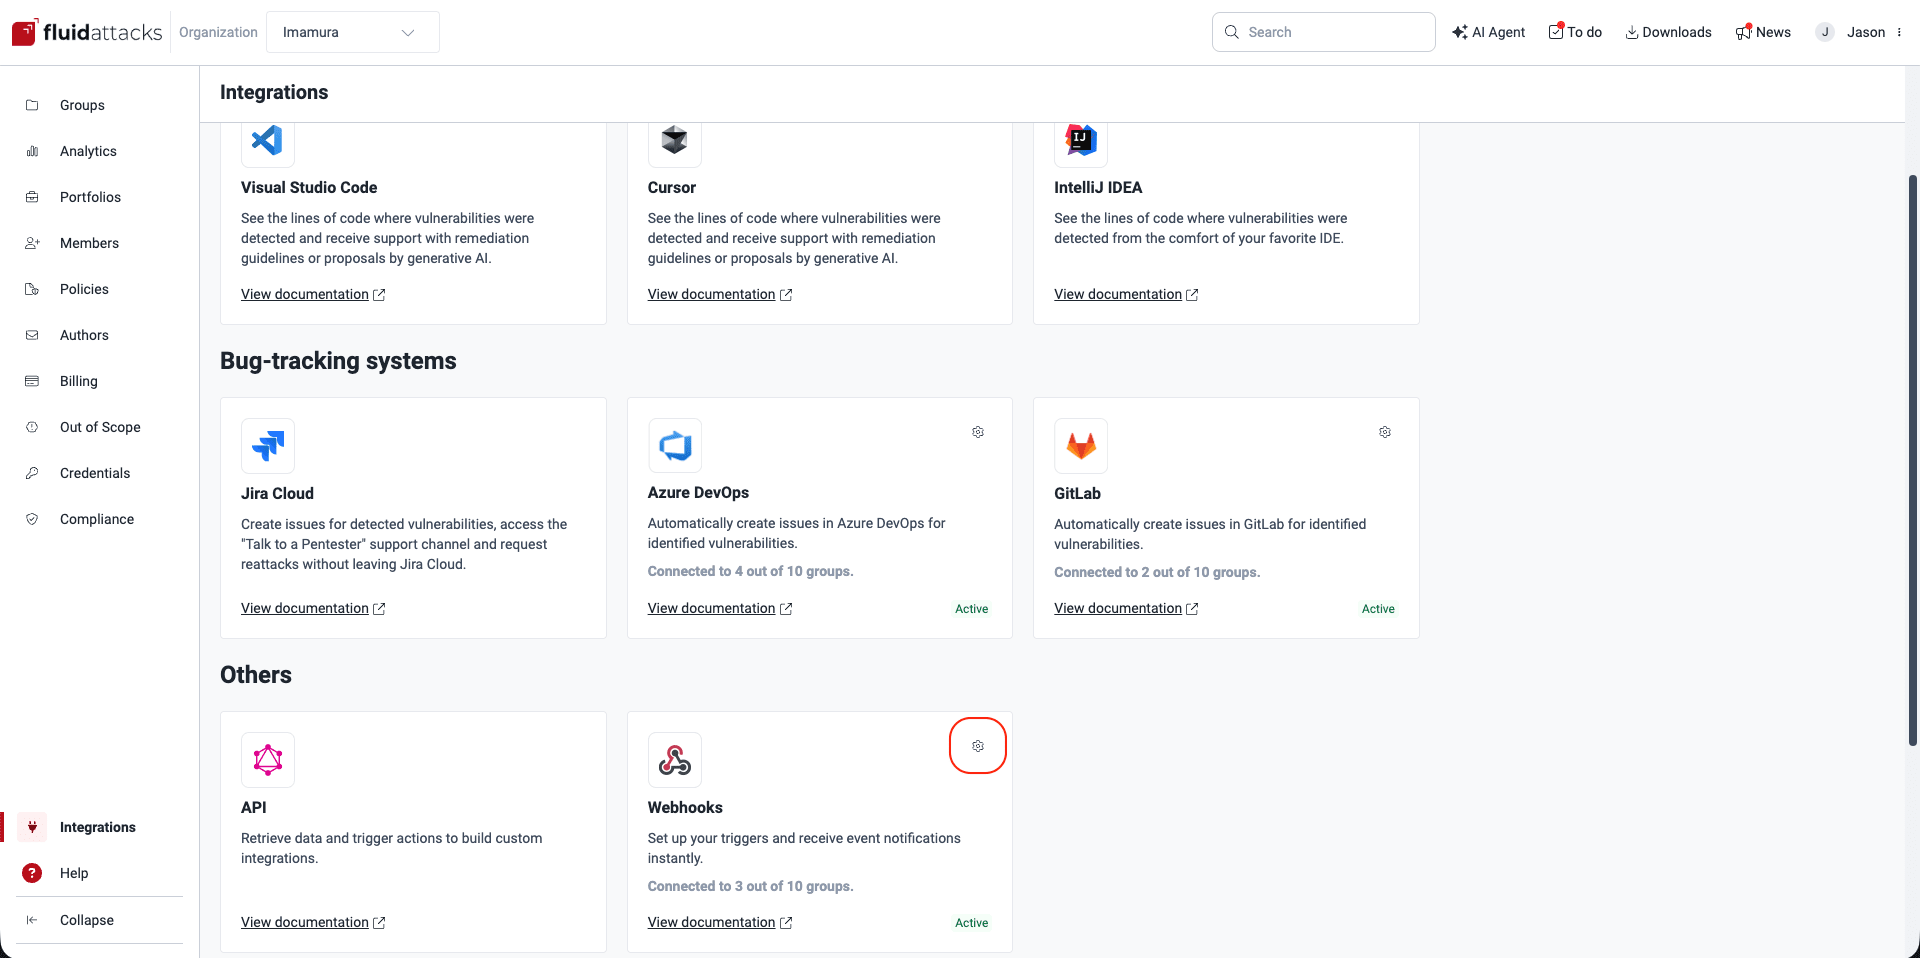
The Webhooks card shows how many of your groups have this integration configured.
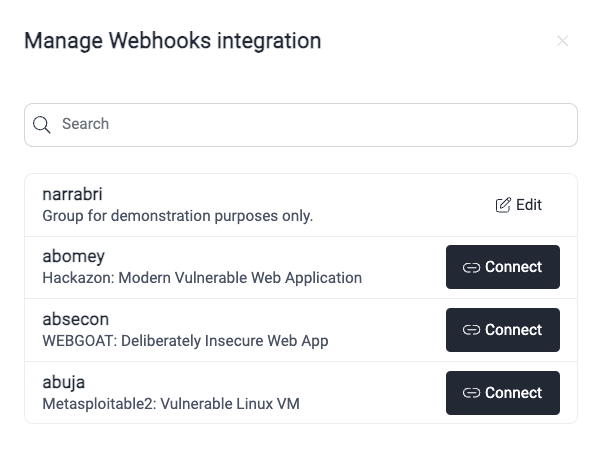
In the pop-up window, you can see the groups that you have access to. If a group already has one or more webhooks, you see the Edit button. If not, you see the Connect button. Each button opens a pop-up window with a table. The section below explains this table.
Understand the Add hooks table
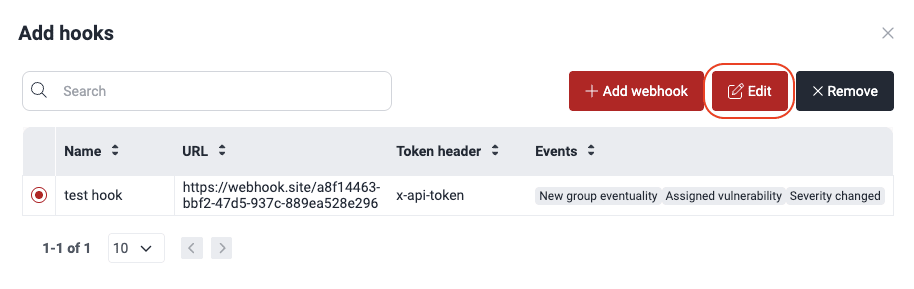
The table in the Add hooks pop-up window shows the endpoints that you configured to get notifications about the events that you selected. This list explains each column:
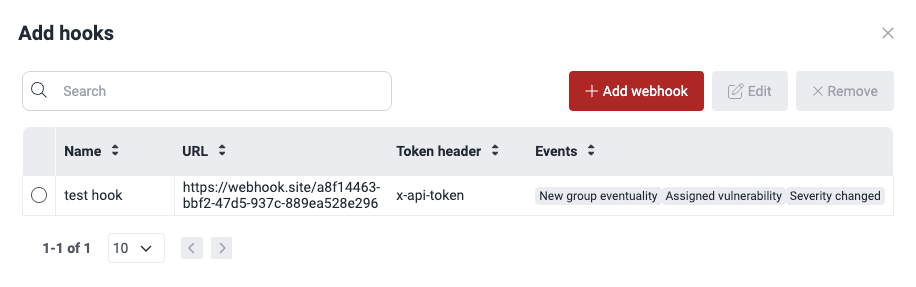
- Name: The name of the webhook
- URL: The endpoint that gets the notifications when one of the selected events occurs
- Token header: The header with your token for the URL
- Events: The list of events that cause notifications when they occur in the group
Events available for webhooks
Events are the actions of the platform that you can get notifications about when they occur in your group. You can configure webhooks for these events:
- Assigned vulnerability: A vulnerability is assigned to a member of the group
- Confirmed false positive: Fluid Attacks confirms that a reported vulnerability is a false positive. This event occurs when your organization requests the false positive. It also occurs when Fluid Attacks finds the false positive with no request from your organization
- Environment removed: An environment is removed from the Scope section
- Event closed: An event is resolved in the group, and Fluid Attacks verified it
- Group token expiration: The Group token is about to expire
- New group event: A new event is reported in the group
- Response to reattacks: Fluid Attacks verifies the status of a vulnerability with a reattack
- Root added: A new root is added to the Scope section
- Root disablement: A root is deactivated
- Severity changed: The severity score changes
- Vulnerability closed: The status of a vulnerability changes from "Open" to "Closed"
- Vulnerability created: A vulnerability is reported to the group
- Vulnerability deleted: A vulnerability is deleted because of a reporting error, or because it was a duplicate or a false positive
Information on each event
When an event occurs, the platform sends an HTTP request to the URL that you set, with this body structure:
{
  "group": "group_name",
  "event": "event",
  "info": {}
}
These are the definitions of the fields:
group: The group where the event occurredevent: The value that identifies the event. The table below shows the value of each eventinfo: An object with more details about the event (the structure of this object is different for each event)
This table shows the value of the event field
and the details of the info object for each event:
| Event | Value of the event field | info object |
| Assigned vulnerability | VULNERABILITY_ASSIGNED | |
| Confirmed false positive | CONFIRMED_ZERO_RISK | |
| Environment removed | ENVIRONMENT_REMOVED | |
| Event closed | EVENT_CLOSED | |
| Group token expiration | AGENT_TOKEN_EXPIRATION | |
| New group event | EVENT_CREATED | |
| Response to reattacks | VULNERABILITY_VERIFIED | |
| Root added | ROOT_CREATED | |
| Root disablement | ROOT_DISABLED | |
| Severity changed | VULNERABILITY_SEVERITY_CHANGED | |
| Vulnerability closed | VULNERABILITY_CLOSED | |
| Vulnerability created | VULNERABILITY_CREATED | |
| Vulnerability deleted | VULNERABILITY_DELETED | |
Test request
When you add or edit a webhook,
the Fluid Attacks platform sends a test request to the URL.
The body of this request has no info object:
{
  "group": "group_name",
  "event": "New hook Added"
}
The value of the event field is New hook Added
when you add a webhook,
and Hook updated when you edit a webhook.
The response of the endpoint must have a 2xx status code.
If it does not,
the platform does not save the webhook.
Manage your webhooks
Role required: Group Manager
The Fluid Attacks platform has three functions to manage webhooks:
Add a webhook
To add a webhook, follow these steps:
-
Go to the Integrations section of your organization.
-
Click the gear in the Webhooks card.
-
Click Connect or Edit next to the group where you want to configure the webhook.
-
Click the Add webhook button.
-
Complete the Add webhook information pop-up window. The list below the screenshot explains the fields.
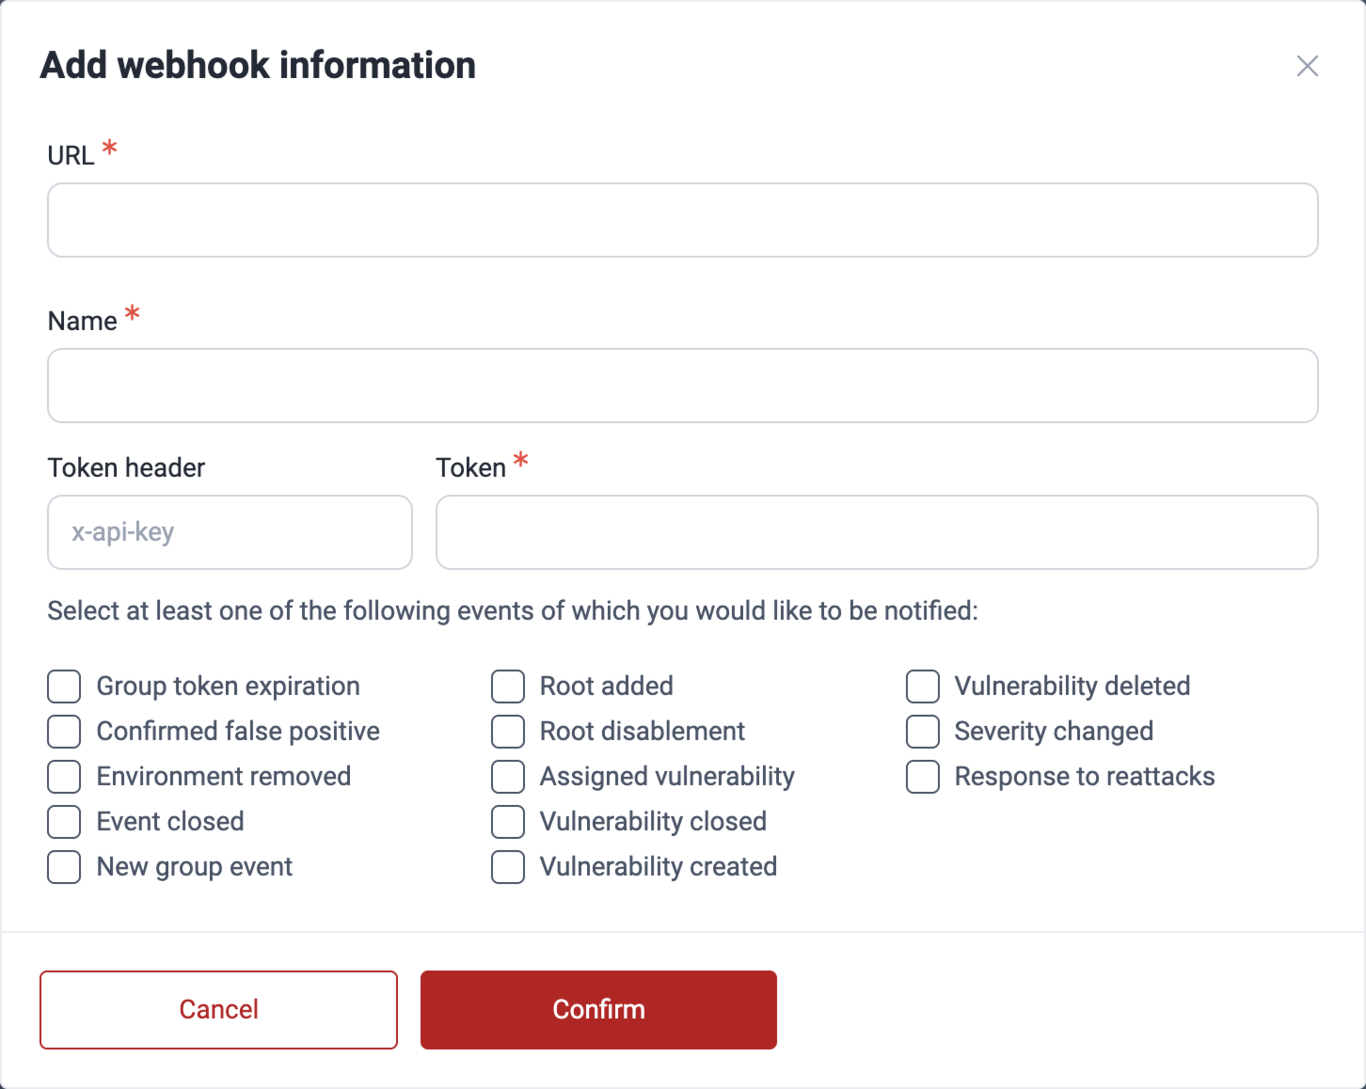
- URL: The URL of the endpoint of the hook where you want to get event notifications
- Name: The name or alias of the webhook
- Token header: The header with the token for that URL (this field is optional, and its default value is x-api-key)
- Token: The security token that is necessary to access the URL (this field is mandatory)
- Events: The group actions that you want to get notifications about. Select a minimum of one. For the definitions, read Events available for webhooks.
- After you complete all the fields, click Confirm. The Fluid Attacks platform sends a test request to the URL. If the test request fails, the platform does not save the webhook and shows an error message.
Edit a webhook
To change the information of a webhook of a group, follow these steps:
-
Go to the Integrations section of your organization.
-
Click the gear in the Webhooks card.
-
Click Edit next to the group where you want to change a webhook.
-
Select the webhook.
-
Click the Edit button.
-
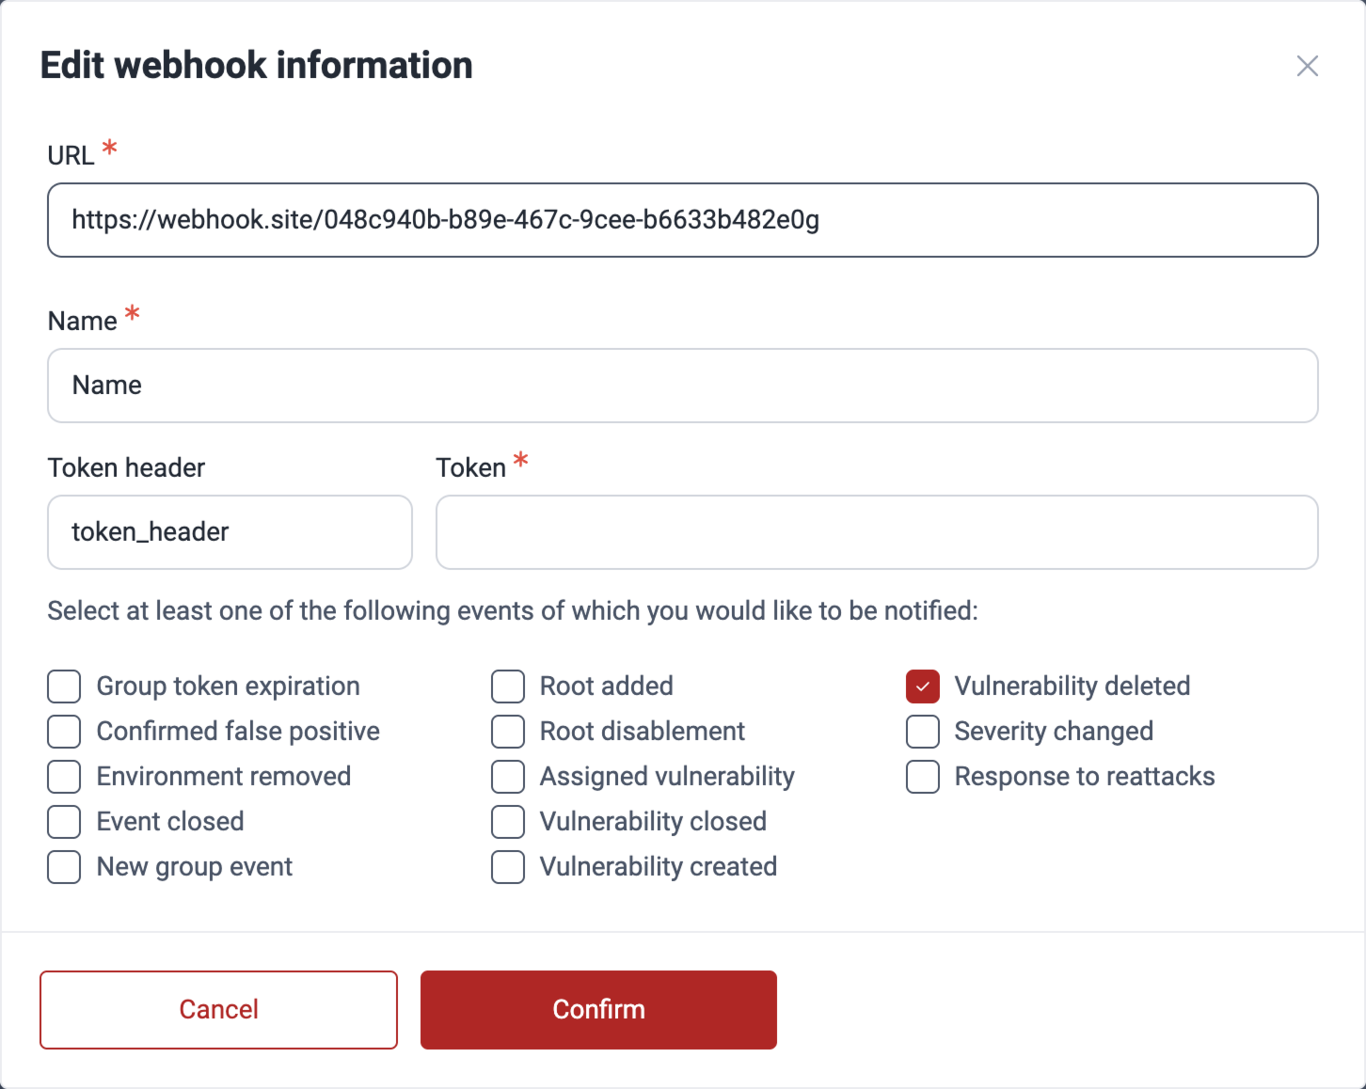
In the new pop-up window, change the configuration of the webhook as necessary. (For the descriptions of these fields, read the instructions to add a webhook.)
-
After you make the changes, click Confirm to save them. The Fluid Attacks platform sends a test request to the URL. If the test request fails, the platform does not save the changes and shows an error message.
Remove a webhook
To remove a webhook that you do not want to keep, follow these steps:
-
Go to the Integrations section of your organization.
-
Click the gear in the Webhooks card.
-
Click Edit next to the group where you want to remove a webhook.
-
Select the webhook.
-
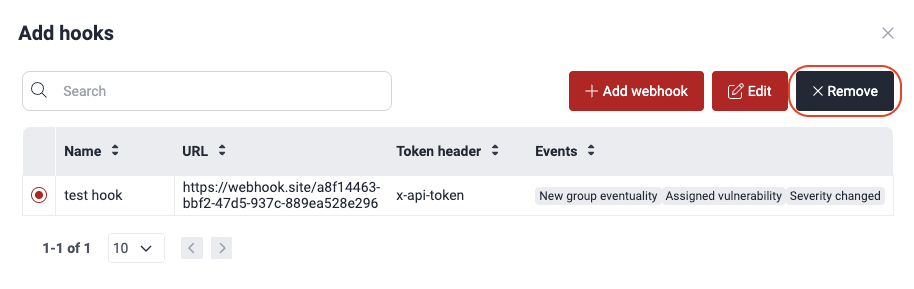
Click the Remove button.
-
A pop-up window asks you if you want to remove the webhook. Click Confirm. The platform removes the webhook from the table.
Error messages
When you add or edit a webhook on the Fluid Attacks platform, the platform validates the webhook. Remember these validations when you do those actions.
If your webhook does not pass one or more checks, you get the related error messages. This table shows the error messages that you can get and their causes:
| Message | Cause |
| Uh oh! The webhook data is invalid. | You did not select an event. Select a minimum of one event. |
| Uh oh! The HTTP protocol is invalid. | The URL uses |
| Entry point already exists | The group has a webhook with this URL. |
| Uh oh! Could not reach the host. | The test request did not get a 2xx status code. The host is not available, or the endpoint rejected the request. For example, the endpoint rejects the request when the token is not correct. |
| Uh oh! Could not find that webhook. | The platform did not find the webhook, or you do not have permission to access it. |
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
API basics
Learn how to authenticate to the Fluid Attacks GraphQL API, query it, and optimize your interactions with it. Includes code examples and best practices.
Stack
Get an introduction to the Stack section, where you can find information about the technology components chosen and used by the Fluid Attacks team.