Create and delete groups
Last updated: Oct 26, 2026
Create a group
Role required: Organization Manager
Your organization is charged per group. Creating a new group and managing it is your organization's decision and responsibility.
On the Fluid Attacks platform, groups are projects that you create for your applications or software products. With groups, you monitor the security assessments and risk exposure of each product separately.
To create a new group, go to your Groups. Click New group. Then, give the characteristics of your new group in the pop-up window.
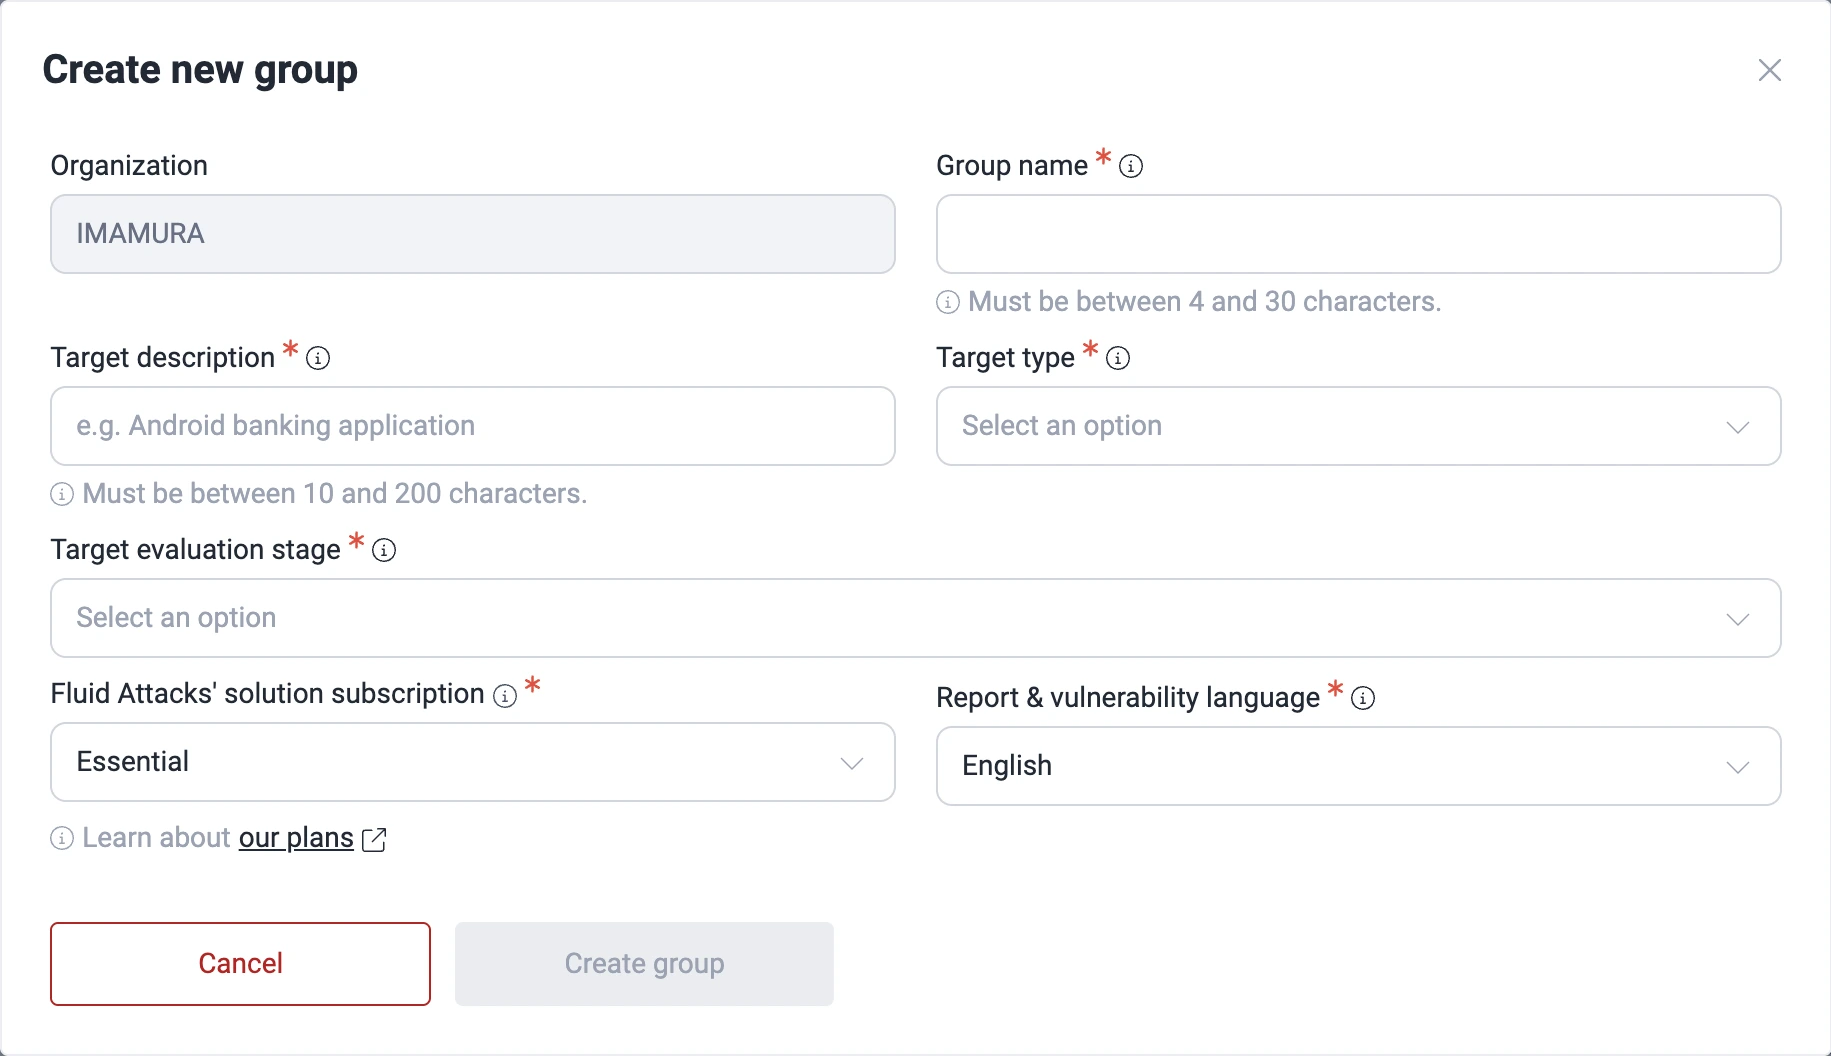
This is a short description of each field:
-
Organization: The name of the organization of the new group
-
Group name: The name of your group, if it is possible, a short name that is easy to remember
Group names should be four to 30 characters.
-
Target description: A description that helps to identify the software development project of the group
Group descriptions should be 10 to 200 characters.
-
Target type: The type of target to test: API, Desktop application, Mobile application, Web application, or Hybrid (web + mobile)
-
Target evaluation stage: The type of environment to evaluate: development, QA, pre-production, or production (you can also select 'Other' and write a different type)
-
Specify evaluation stage: The custom type of environment to evaluate, if you select 'Other' in the previous field
-
Fluid Attacks' solution subscription: The AppSec testing methodology (it can be one of these):
- Essential: Continuous security testing and help with remediation only with the Fluid Attacks SAST, SCA, DAST, and CSPM
- Advanced: Fluid Attacks secures your software with the Essential plan features, plus AI SAST, continuous security testing by pentesters, and help to understand vulnerabilities
-
Report & vulnerability language: The language of your reports
When you complete the configuration of your new group, click Create group. The group shows immediately in your group table, and you can start to work on this vulnerability management project.
Delete a group
Role required: Group Manager
This action will immediately delete the group. It will remove pertinent data for your organization, including key information on detected types of vulnerabilities. This is a destructive action and cannot be undone. Learn about the information Fluid Attacks keeps about the group by reading the page Data retention policy.
When your free trial or subscription expires, Fluid Attacks deletes your related group(s). The warning above also applies in this case.
When a group is not necessary, you can delete it. To delete a group, do these steps:
-
Go to the Scope section of the group.
-
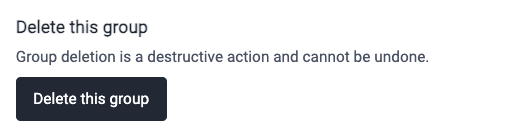
Scroll down to the end of the page to find Delete this group. If you cannot find it, you do not have the Group Manager role in this group. This role is necessary to delete the group.
-
Click Delete this group.
-
In the confirmation pop-up window, type the name of the group and an observation about its deletion. You can also select a reason for the deletion (see the explanation of each option below). Click Confirm to delete the group.
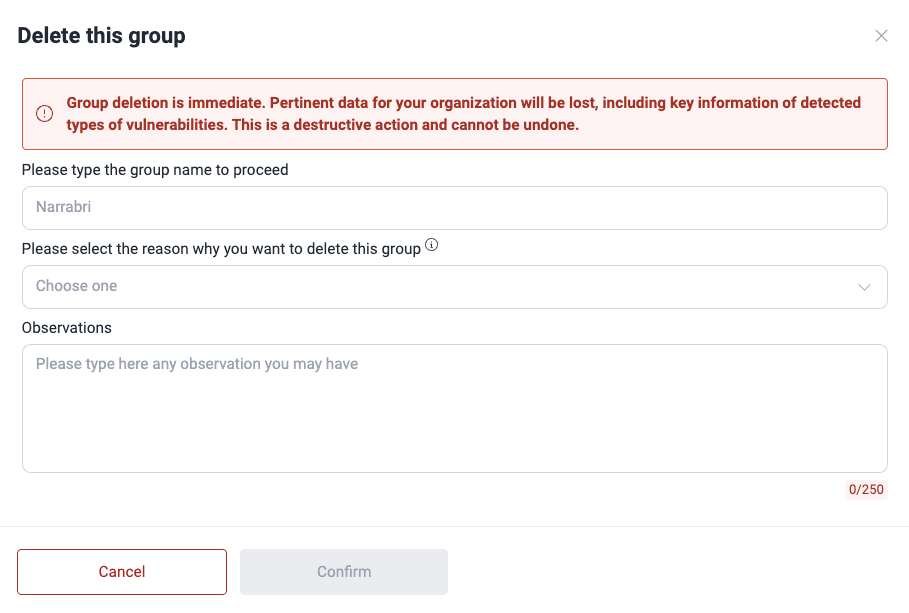
You need to make sure that you want to proceed with the deletion of the group, as there is no way of retrieving information about your group after you complete it.
When the process is complete, the platform members with Group alerts on get an email about the removal.
Provide a reason for group deletion
Role required: Group Manager
When you remove a group, you can select a reason for this action.
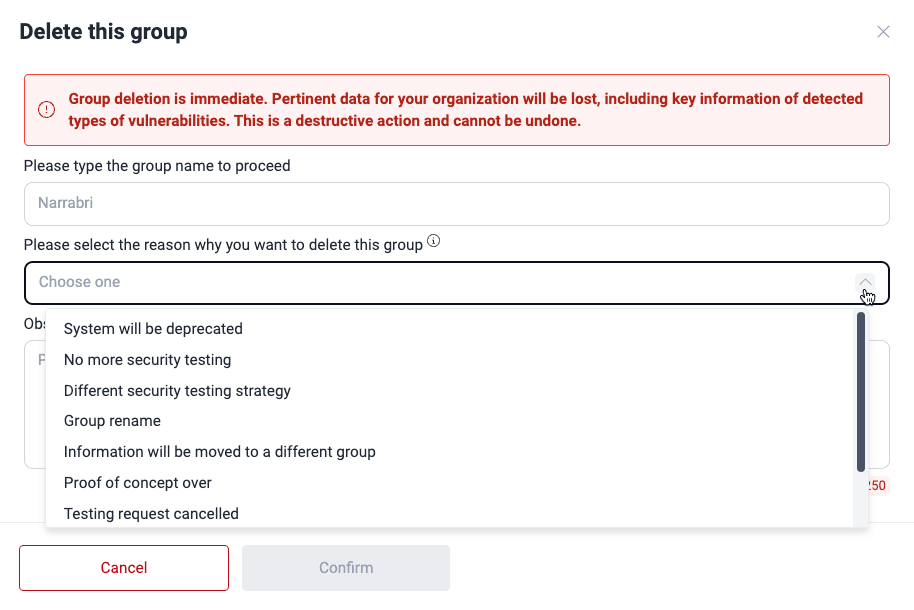
These are the definitions of the reasons in the group deletion form:
- System will be deprecated: Development stops in the repositories of the group.
- No more security testing: More tests of the systems of the group are not necessary for your team.
- Different security testing strategy: Your team decided to change the AppSec testing provider for the systems of the group.
- Group rename: Your team wants to change the name of the group to a better name for the project.
- Information will be moved to a different group: The scope of the group goes to a different group, because the project merges with a different project or because the information must have a new structure.
- Proof of concept over: The proof of concept has ended.
- Testing request cancelled: Your team wants to cancel the security tests of a group before they start.
- Created by mistake: Your team created the group by mistake.
- Other reason not mentioned here: Your team deletes the group for a reason that is not one of the eight previous reasons.
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.