Repositories out of scope
Last updated: Oct 26, 2026
Role required: User, Vulnerability Manager, Organization Manager
Fluid Attacks recommends that you import repositories with Open Authorization (OAuth). With OAuth, you authorize the connection between the platform and your accounts on code repository hosting providers.
The platform supports four providers: Azure, Bitbucket, GitHub, and GitLab. When you enable OAuth, the repositories that are not in a group of your organization are in the Out of Scope section of your organization.
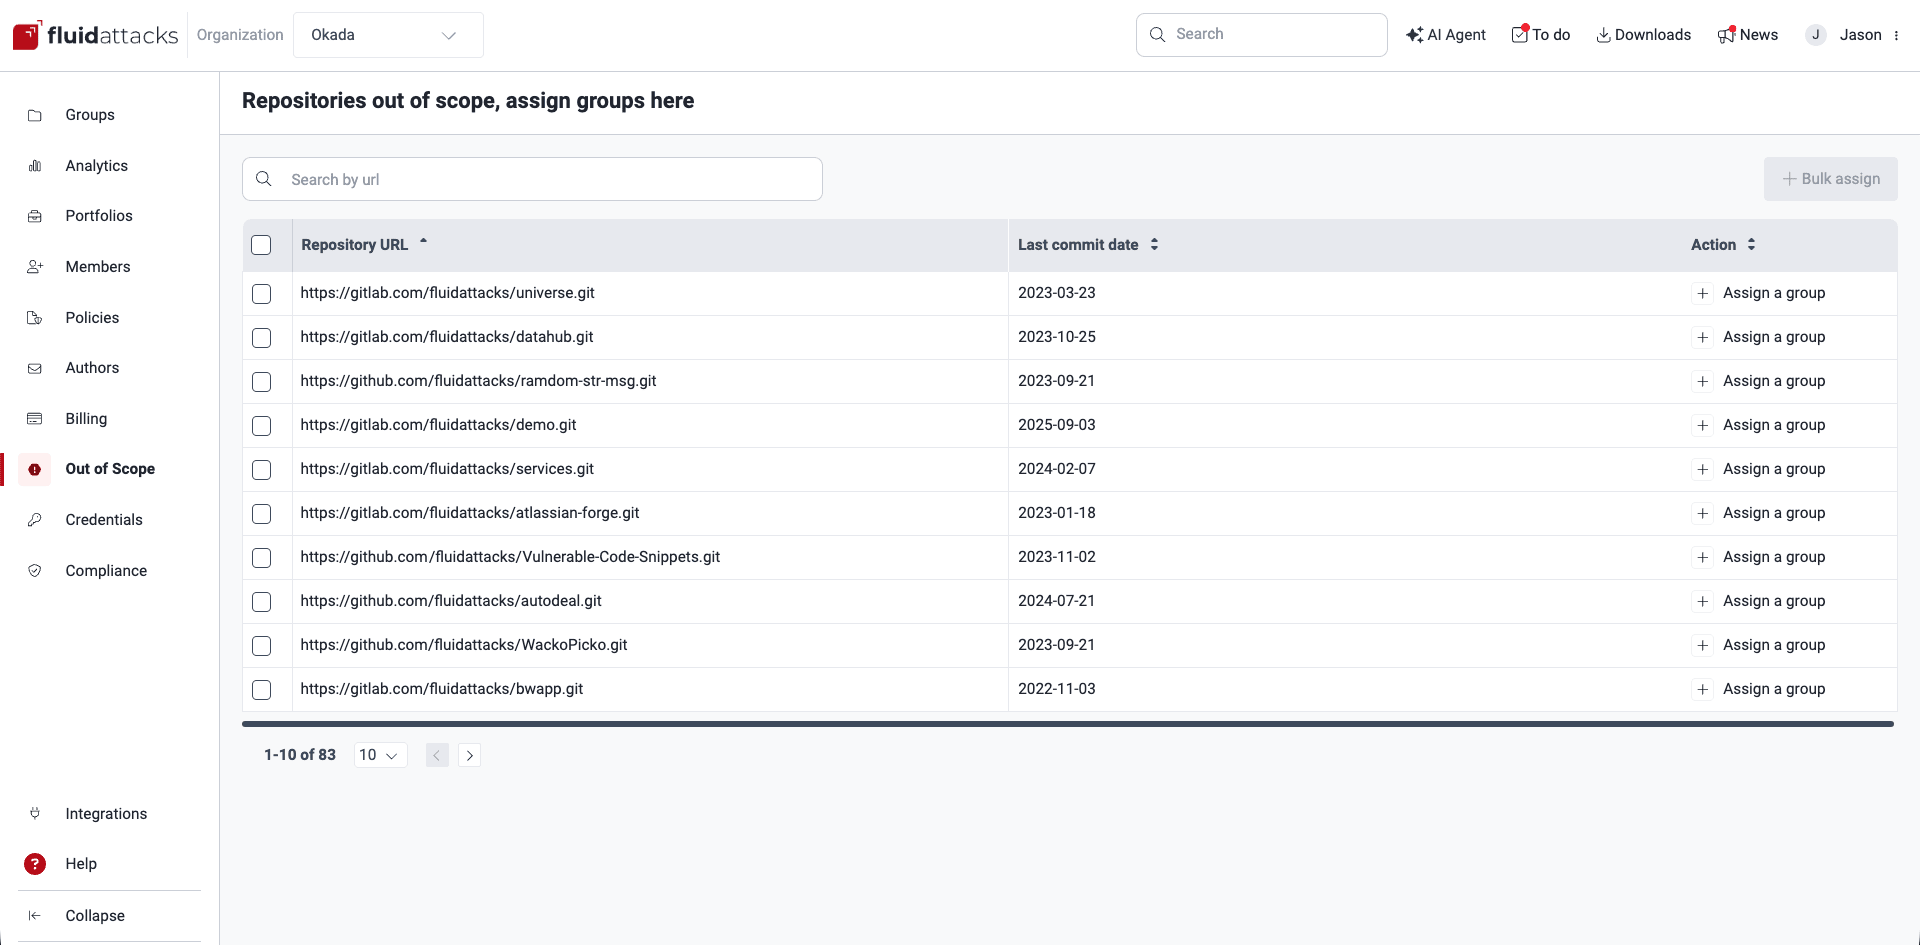
It may take approximately 30 minutes to 1 hour for the table in Out of Scope to populate after you enable the new connection.
Organization members with the Organization Manager role can select the repositories to add to the platform for security testing. They assign the repositories to groups.
You can add repositories one by one or in bulk. For detailed instructions, read "Import repositories fast and safely with OAuth".
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Import repositories with OAuth
Learn to import Git repositories on the Fluid Attacks platform using Open Authorization to start security testing.
ToE and SBOM
The Fluid Attacks platform has detailed information about the attack surface of your software, showing the status of assets and allowing you to generate SBOMs.