CVSS score adjustment
Last updated: Nov 4, 2026
Software composition analysis (SCA) detects when open-source components and dependencies in your software project have related CVE entries. An attacker can exploit these vulnerabilities only in special conditions. Your application possibly does not have them.
To show their possible impact accurately, Fluid Attacks adjusts the CVSS score of vulnerabilities found with SCA scans. Fluid Attacks gets the original CVSS score from the CVE-reporting source. When the source has no CVSS v4.0 vector, Fluid Attacks calculates the v4.0 base metrics. Then Fluid Attacks calculates a CVSS v4.0 score with the base metrics and the threat metrics (CVSS-BT). Fluid Attacks specifies the Exploit Maturity (E) metric as "Unreported" (U) for all the vulnerabilities that SCA scans find, also when there are public exploits or reports of attacks. The CVE-reporting source possibly does not specify this value.
Because of this value, the CVSS scores that Fluid Attacks' SCA reports are lower than the scores that the CVE-reporting sources calculate. To see if attackers exploit a vulnerability, examine its KEV and EPSS values.
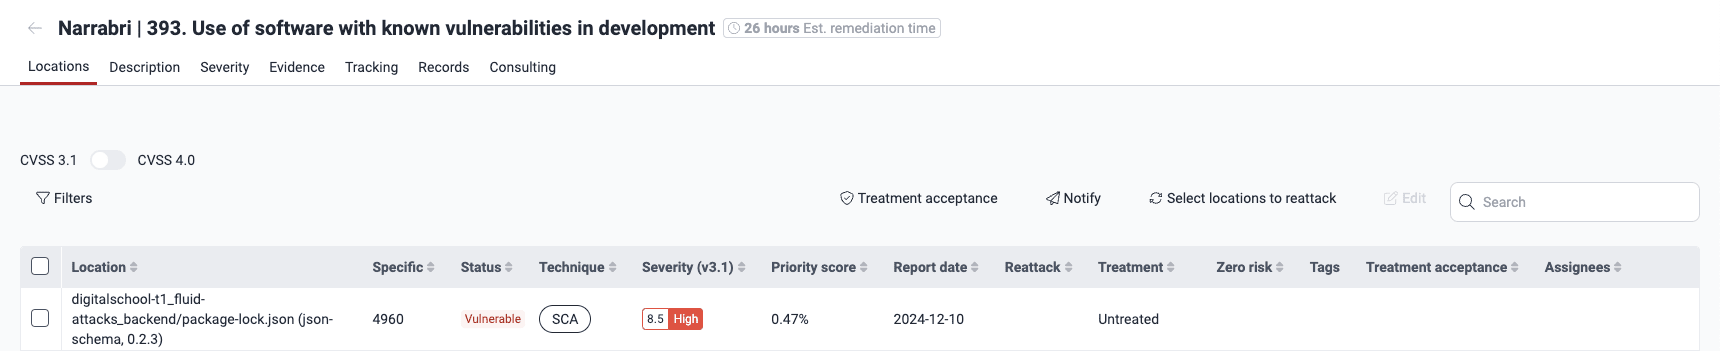
This example shows a vulnerability that Fluid Attacks' SCA reported. The CVE-reporting sources frequently calculate only CVSS v3.1 scores. Thus, the example compares the v3.1 score of the source with the v4.0 score of Fluid Attacks.
-
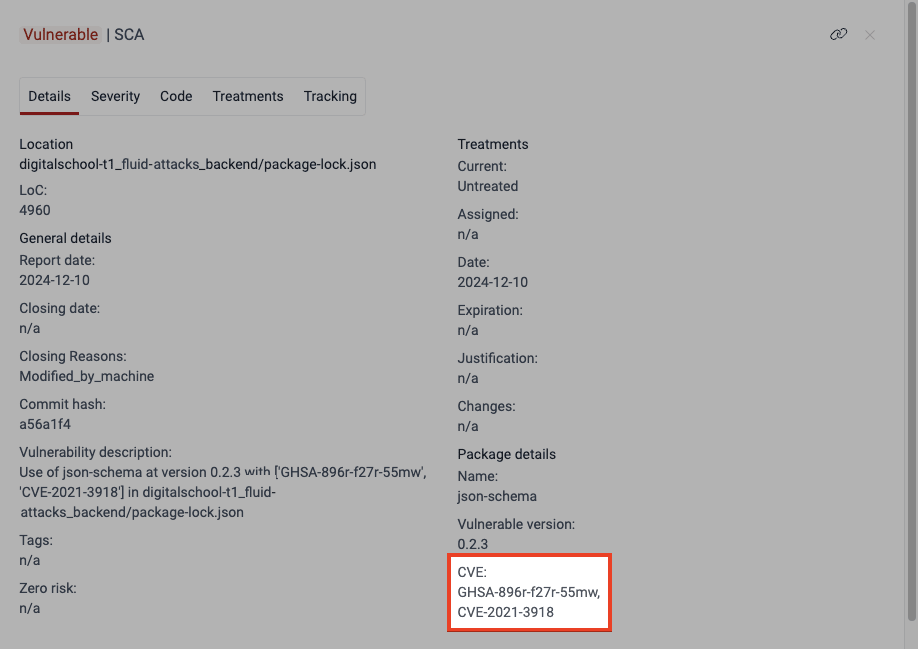
Click the location of the vulnerability. The Details tab shows the CVE.
-
Go to the Severity tab. This tab shows the CVSS v4.0 vector string that Fluid Attacks assigned (CVSS-BT score: 8.1).
-
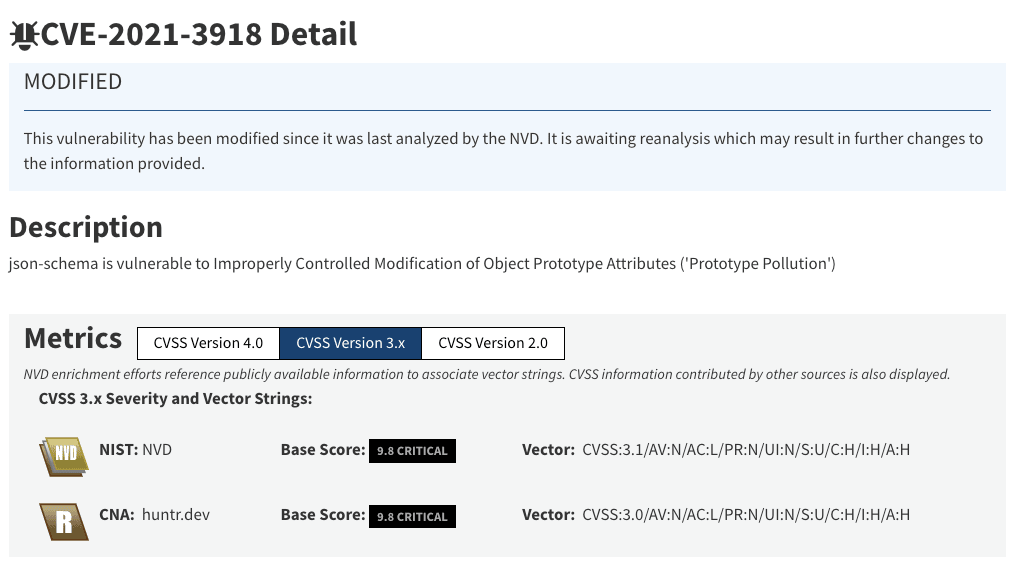
Examine the advisory of NIST and the responsible CNA. The advisory shows the CVSS vector string that they assigned (CVSS v3.1 score: 9.8).
-
Compare the two vector strings.
Source (CVSS v3.1): CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
Fluid Attacks (CVSS v4.0): CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:U
Without the E metric, the v4.0 score is 9.3 (Critical). Fluid Attacks specified E as "Unreported" (U). Thus, the score is 8.1 (High). The difference from the score of the source is 1.7 units. In the qualitative severity rating, the difference is one level.
Compare the scores in the Fluid Attacks Database
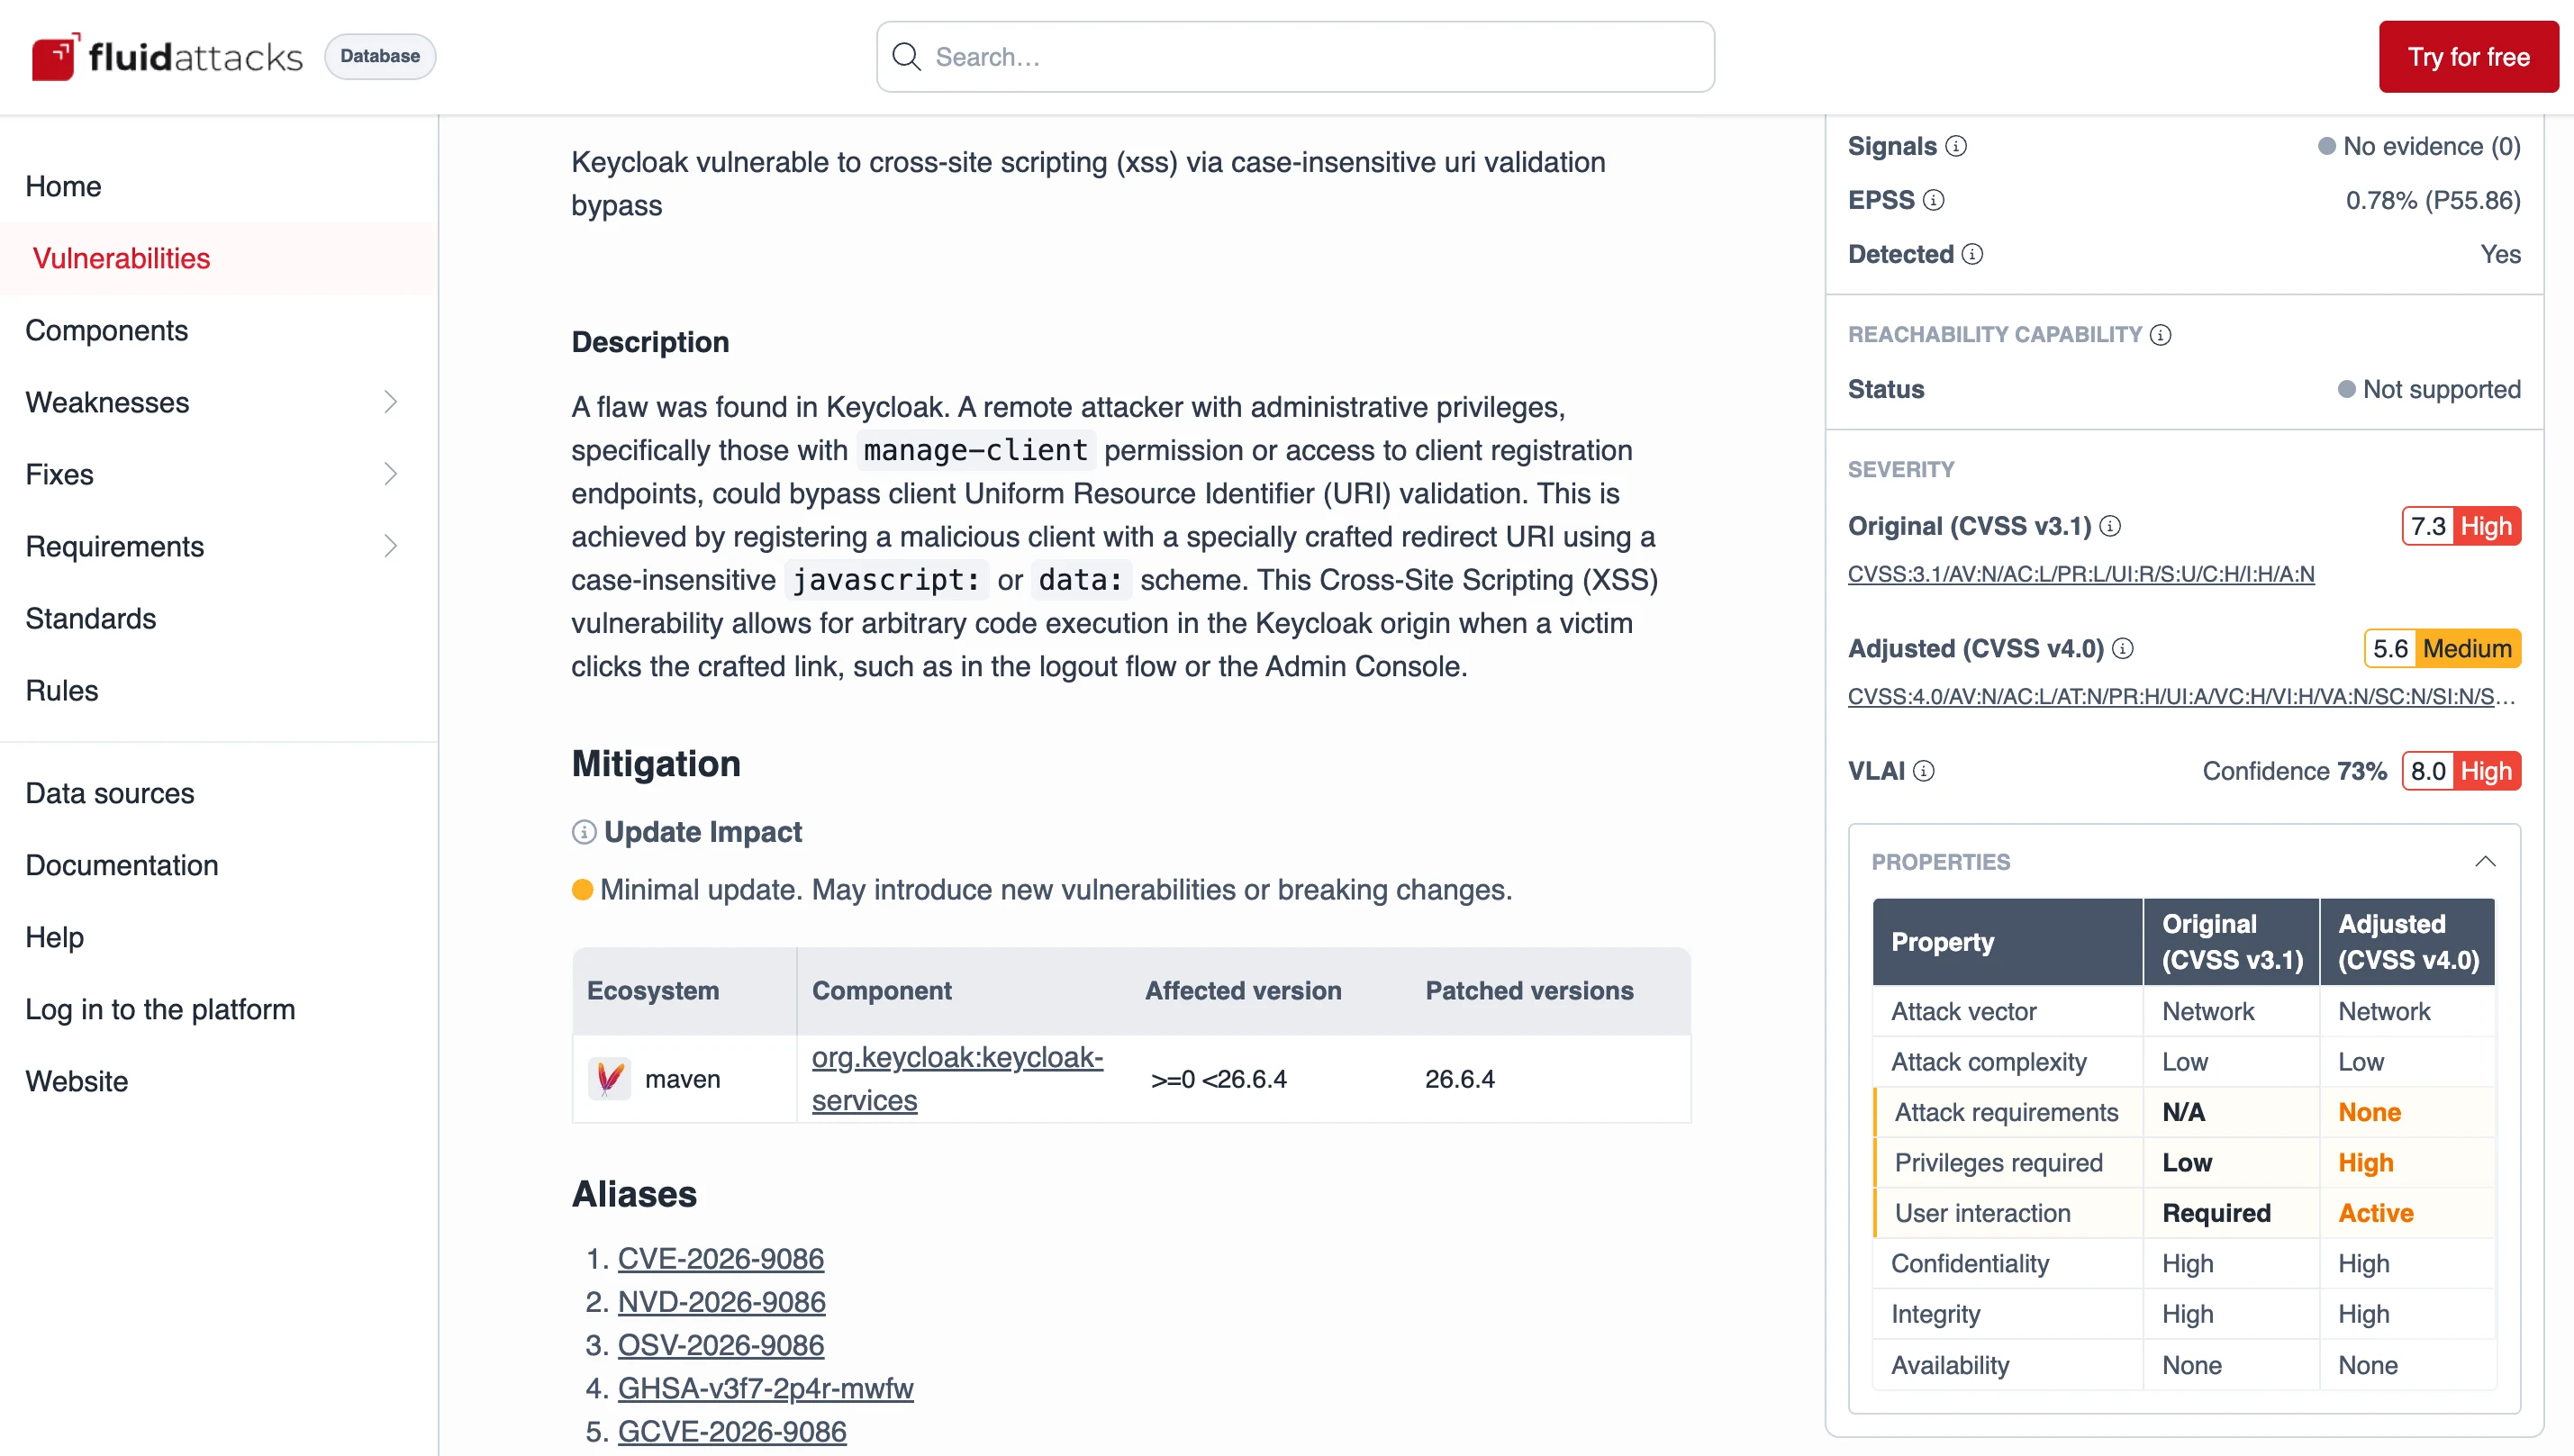
The Fluid Attacks Database shows the original and adjusted scores of each vulnerability together. Open a vulnerability, for example FLAT-SMS1C. The Severity section shows these scores, for example:
- Original (CVSS v3.1): The score that the CVE-reporting source calculated (7.3, High)
- Adjusted (CVSS v4.0): The score that Fluid Attacks calculated (5.6, Medium)
Below each score, the vector string has a link to the FIRST CVSS calculator.
Expand Properties.
The Properties table compares the base metrics of the two scores
and identifies the metrics that are different.
The table does not show E.
The last metric of the adjusted vector string is E:U.
The difference between the two scores can have these causes:
- A different CVSS version, if the source has only a CVSS v3.x score
- The E (Exploit Maturity) metric, which Fluid Attacks specifies as "Unreported" (U)
- Base metrics that Fluid Attacks calculates, if the source has no CVSS v4.0 score
Fluid Attacks specifies E:U for all vulnerabilities,
also when the KEV or Exploit fields show that attackers exploit the vulnerability.
Examine these fields before you use the adjusted score to set priorities.
If Fluid Attacks' pentesting team performs a review of a vulnerability reported by SCA scans and can prove that the vulnerability is exploitable, the CVSS score is adjusted to reflect this.
Vulnerability signature update
Learn about the Fluid Attacks vulnerability signature management for software composition analysis SCA scans.
Correlate threat models
Discover the correlation between your threat model and vulnerabilities reported by Fluid Attacks. Then, prioritize remediation based on your business risks.