False positive requests
Last updated: Oct 26, 2026
Role required: User, Vulnerability Manager or Group Manager
False positive requests generated by members with the User role must be approved by a Vulnerability Manager or Group Manager before they are considered by Fluid Attacks. Without this member's approval, the reported vulnerability will break the build when Users attempt to deploy the system version containing it.
You can request a treatment for a reported vulnerability if your organization analyzes it carefully and finds that it is not a threat. This treatment shows as "False positive request" in the treatment options on the Fluid Attacks platform.
You can send your request from the information window of the vulnerability or from the window to edit vulnerabilities. With the window to edit vulnerabilities, you can request the treatment for more than one vulnerability.
To use the "False positive request" option from the information window, follow these steps:
-
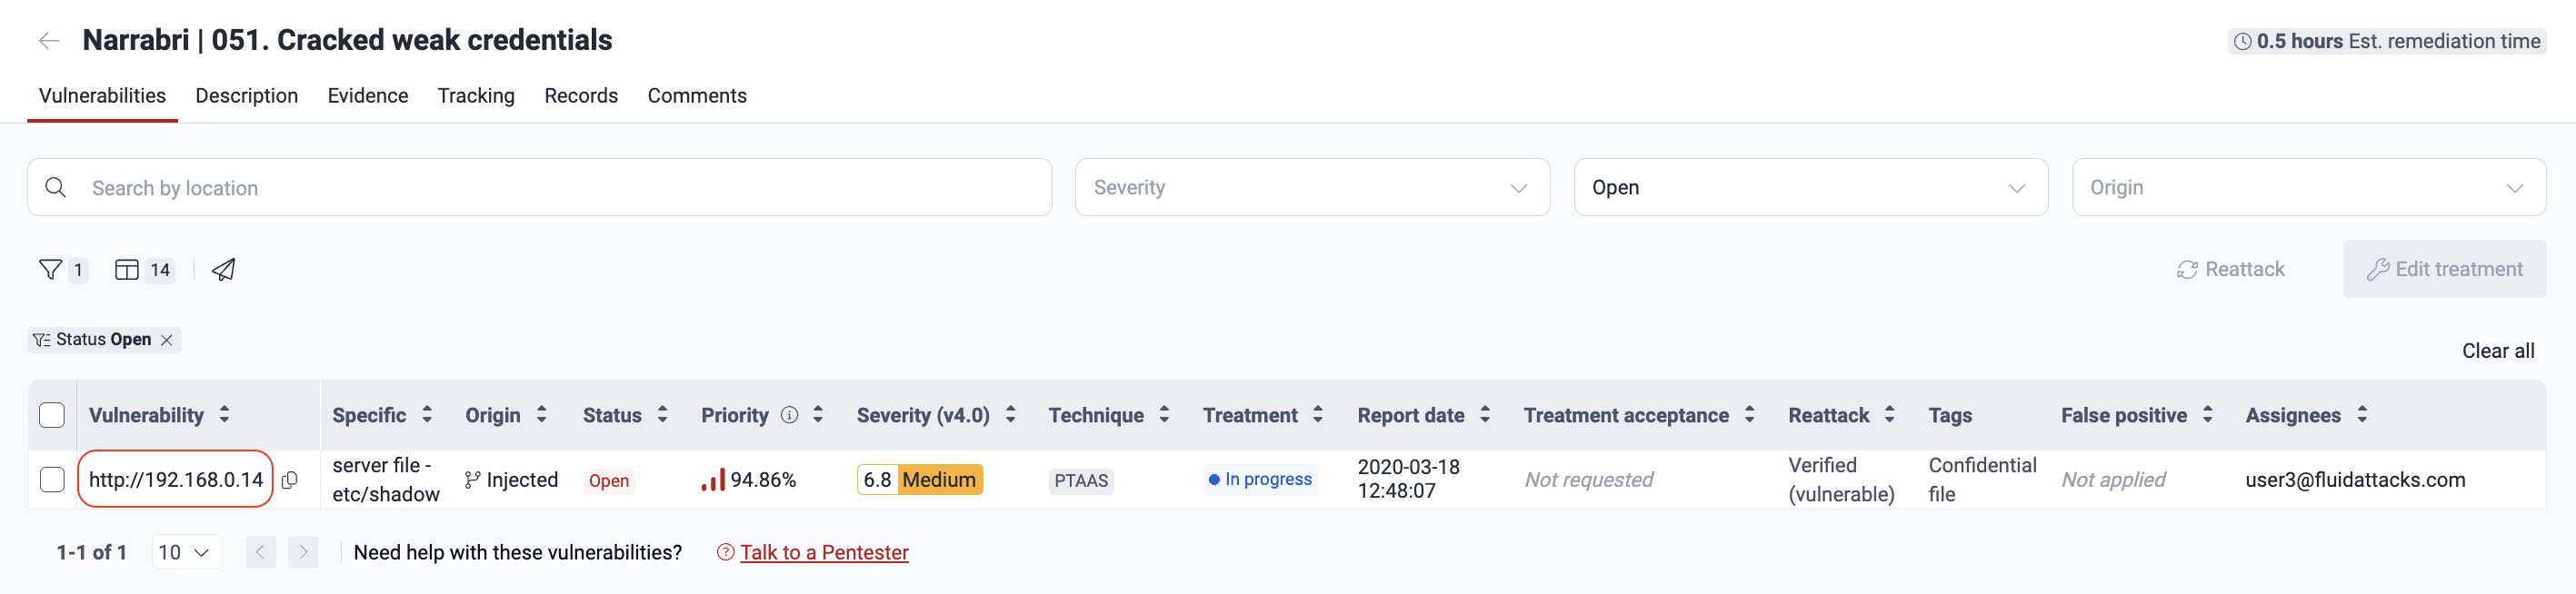
In the Vulnerabilities section, click the weakness to see its related vulnerabilities.
-
Click the vulnerability.
-
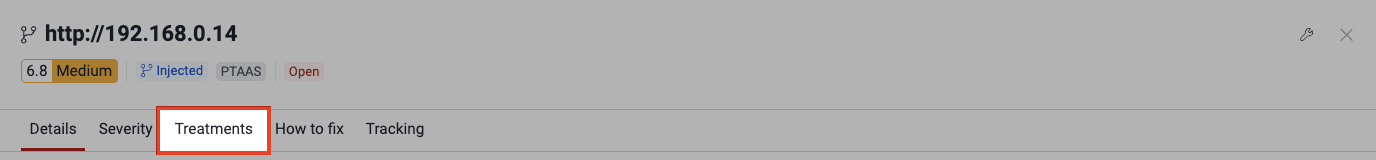
In the information window, click the Treatments tab.
-
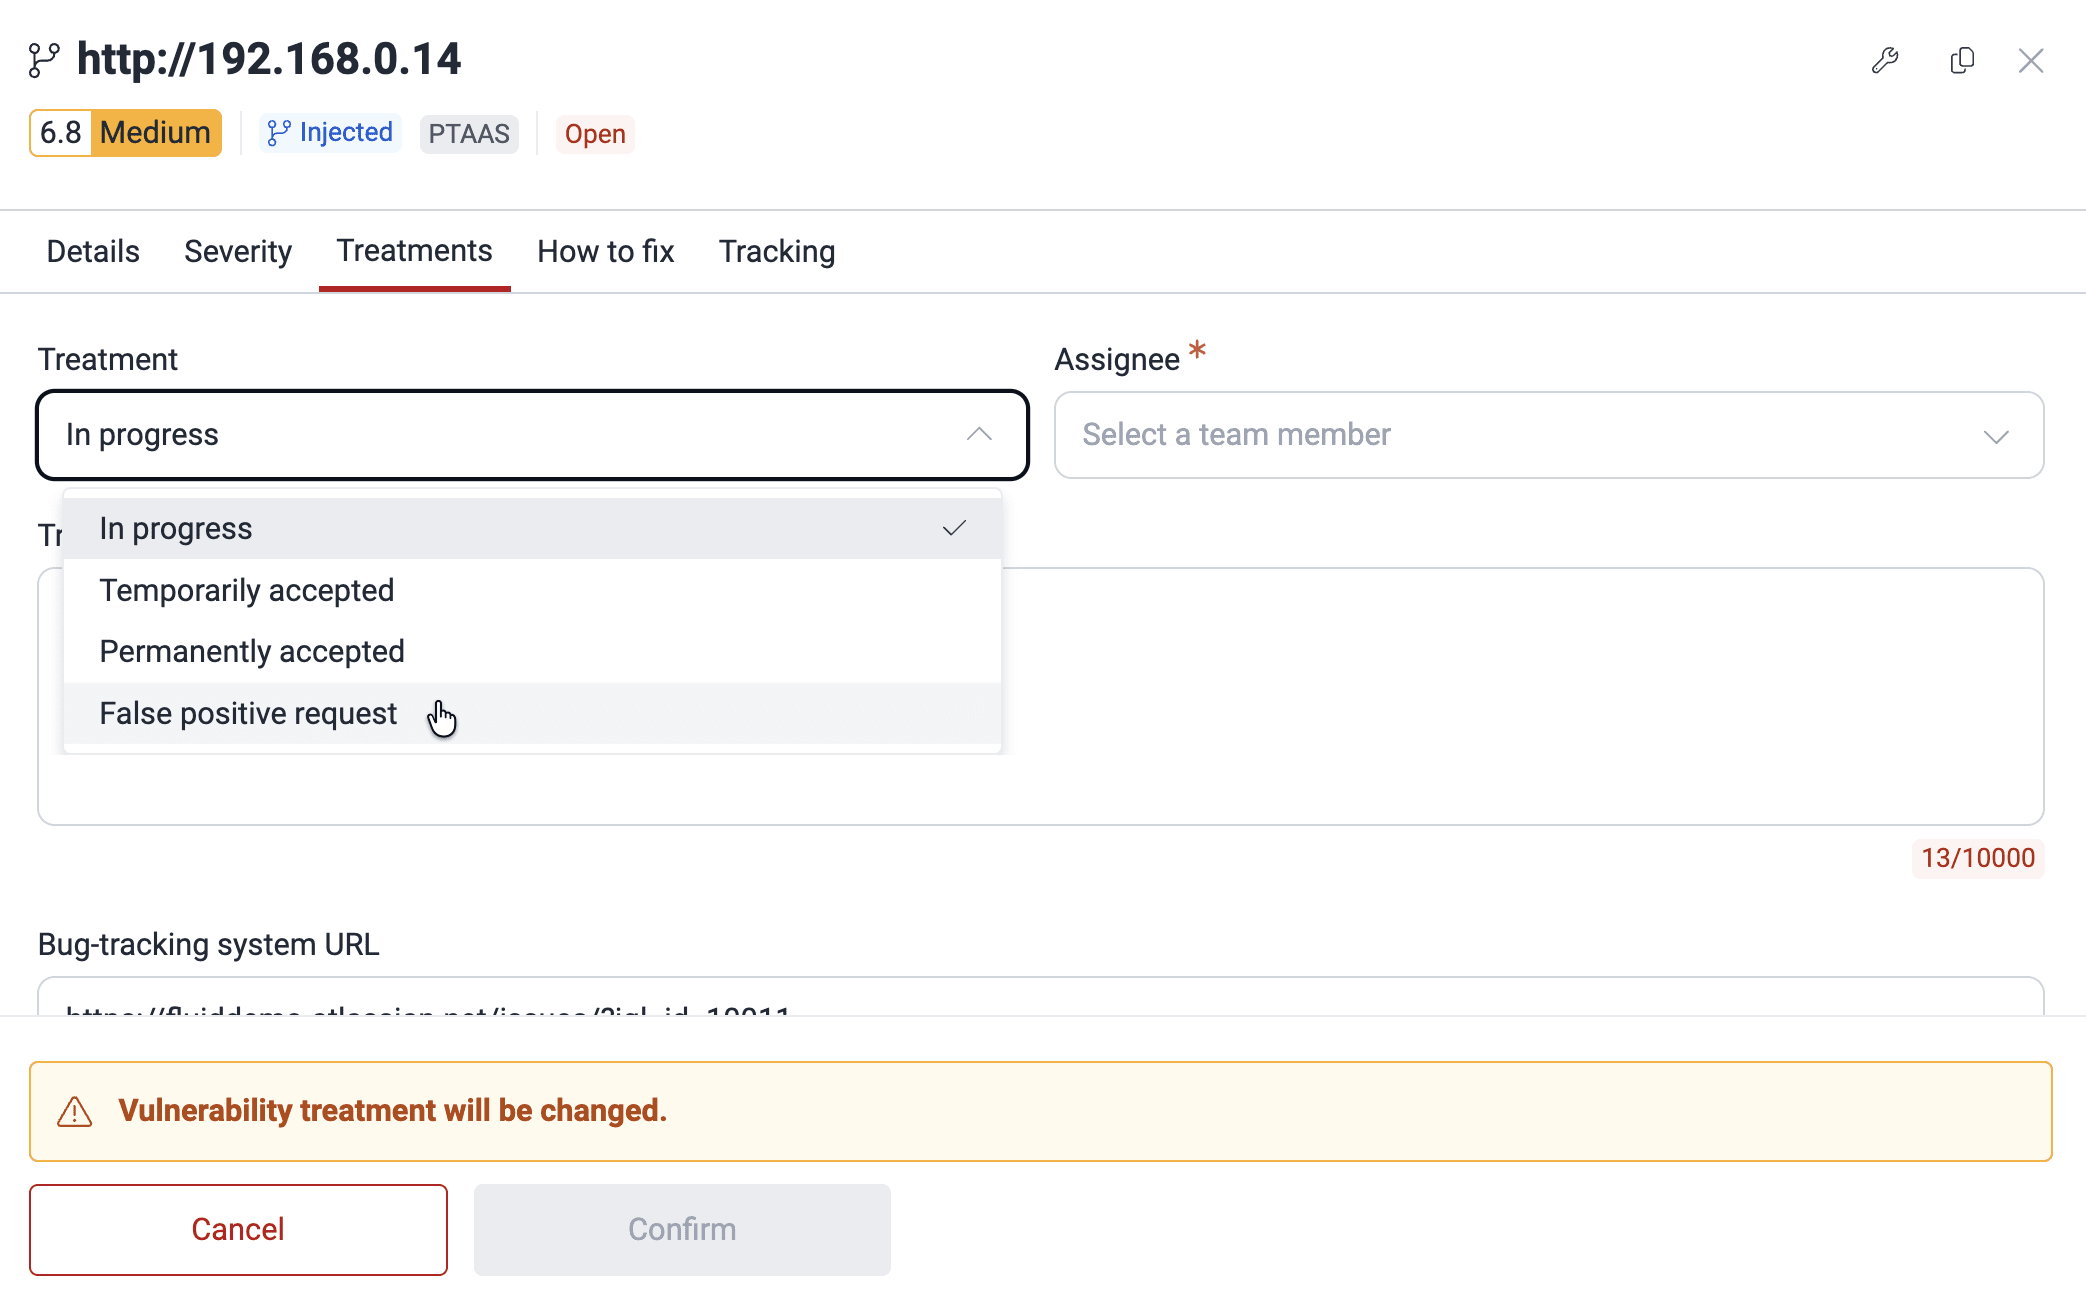
Select False positive request from the Treatment dropdown menu.
-
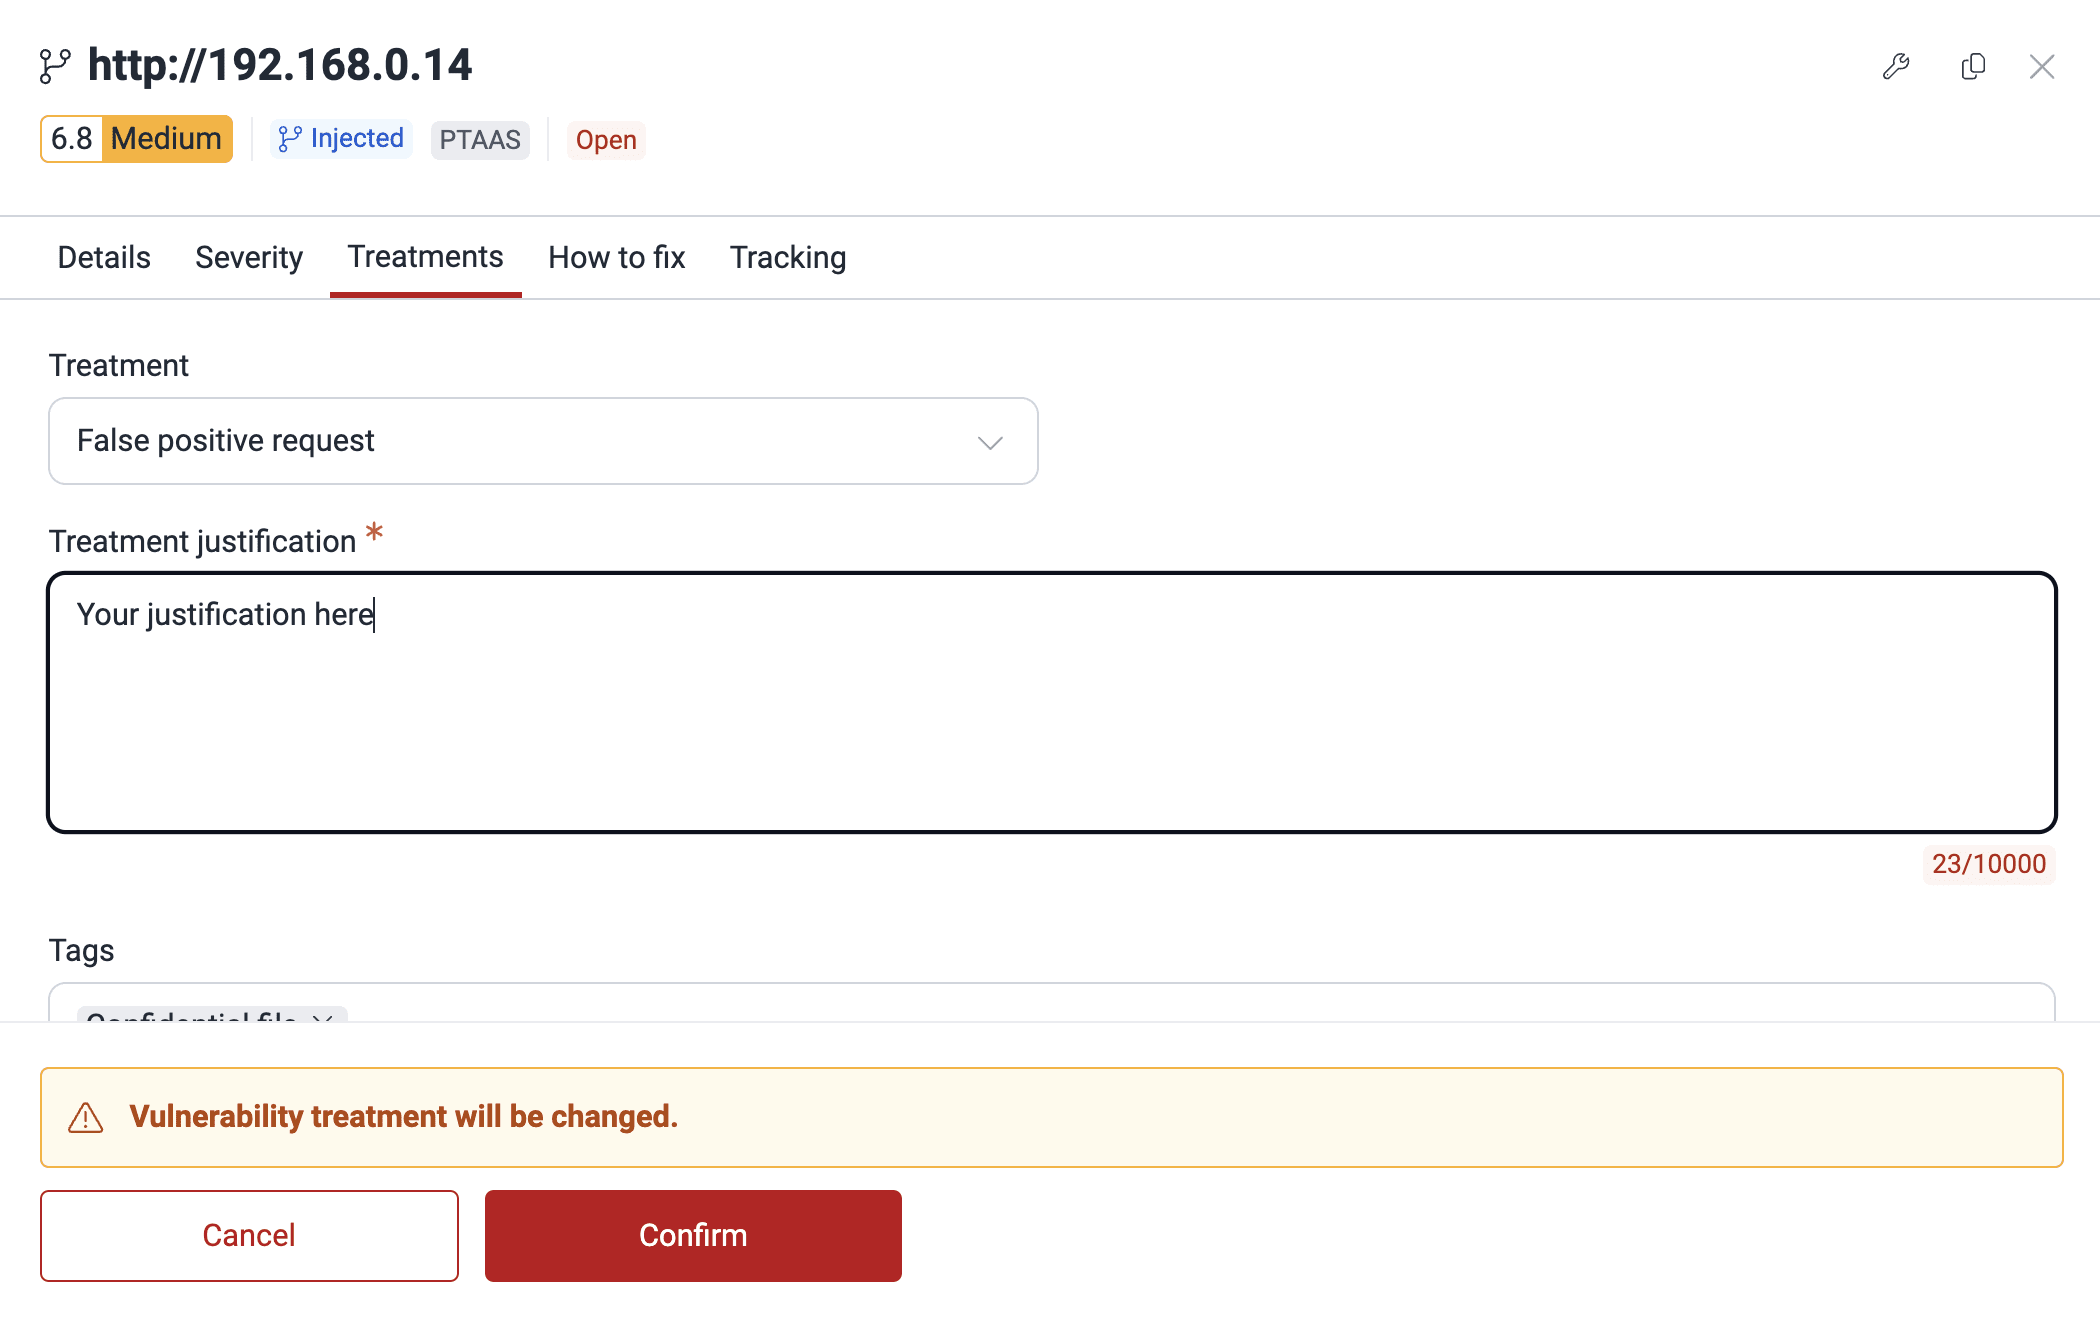
Write a justification for your request. If you want, add or remove tags.
-
Click the Confirm button.
Fluid Attacks reads your justification to examine if the vulnerability is a threat. If it is not a threat, Fluid Attacks removes it from the Vulnerabilities table. But, if Fluid Attacks finds that the vulnerability is a risk, the vulnerability stays in the report.
To request the treatment from the Manage treatments window, follow these steps:
-
In the Vulnerabilities section, click the weakness to see its related vulnerabilities.
-
Select the checkbox next to the vulnerability that you want to assign the treatment to. Then, click Edit treatment.
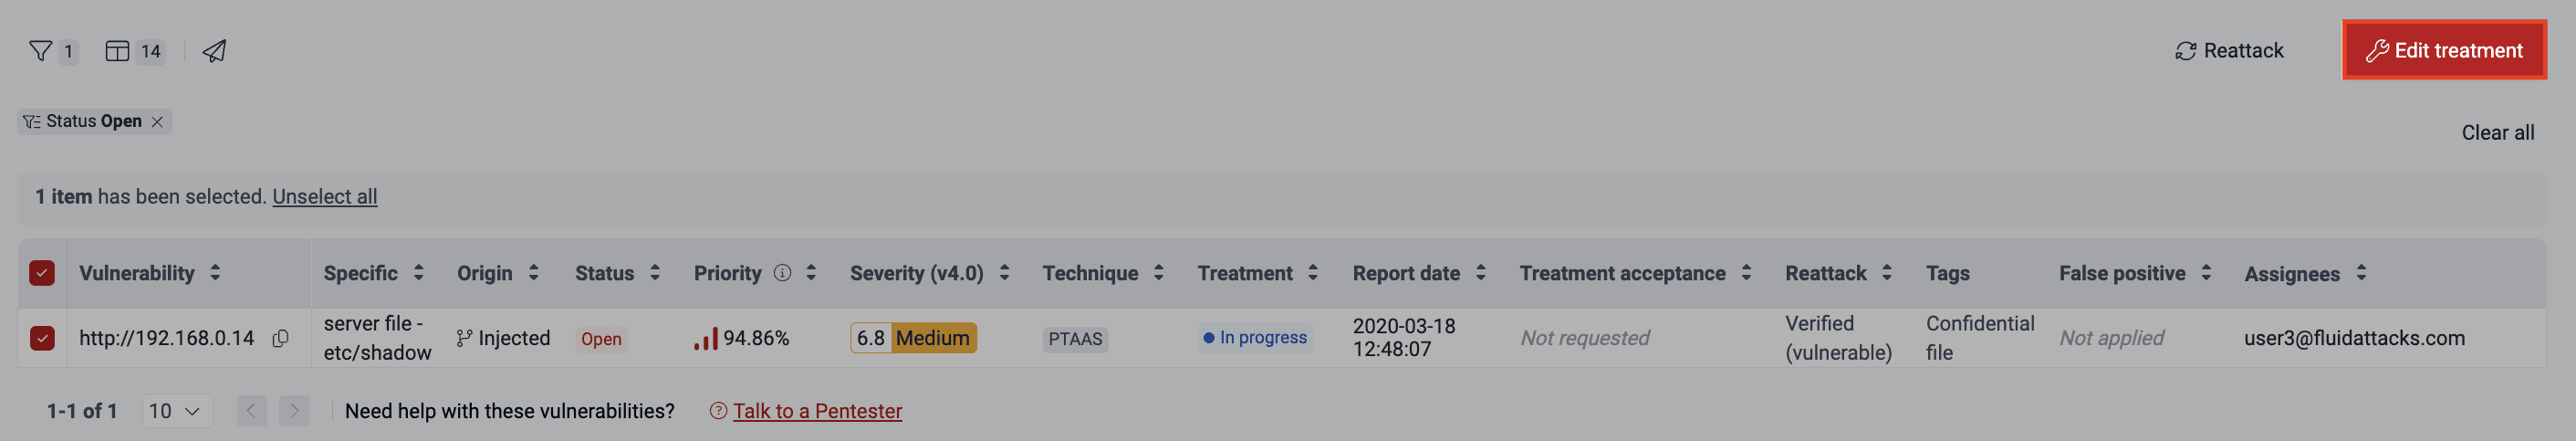
If you want to assign the treatment "False positive request" to more than one vulnerability, tick their corresponding checkboxes and click the Edit button.
-
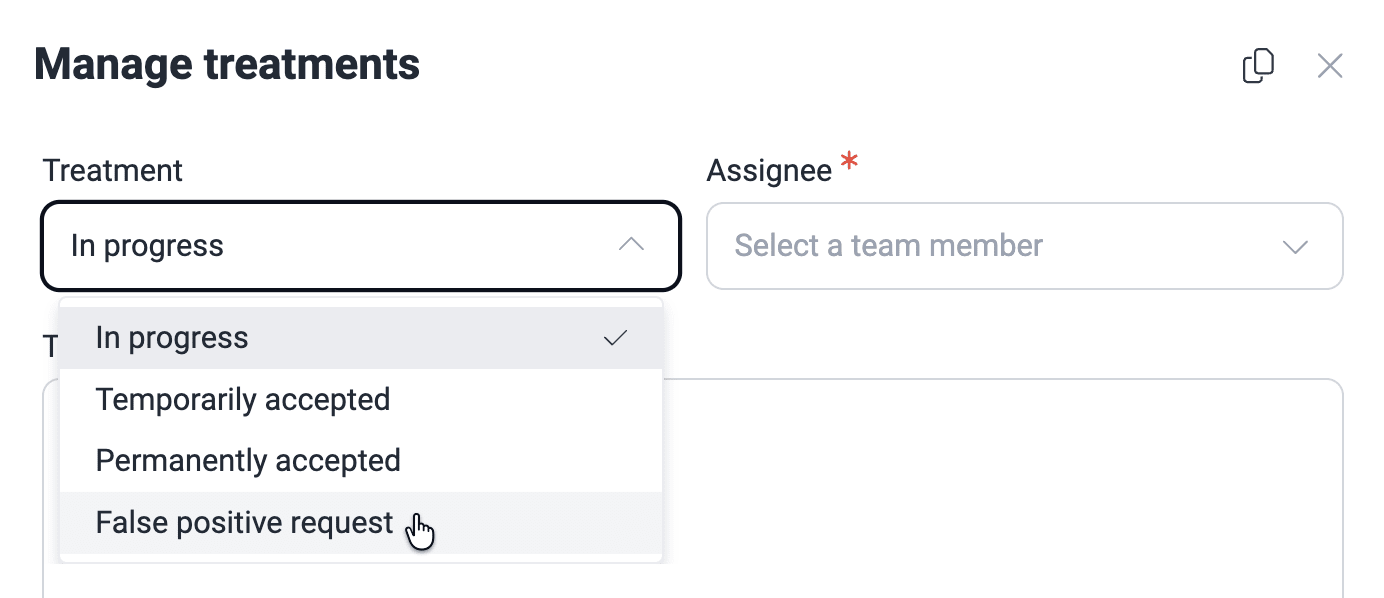
Select False positive request from the Treatment dropdown menu.
-
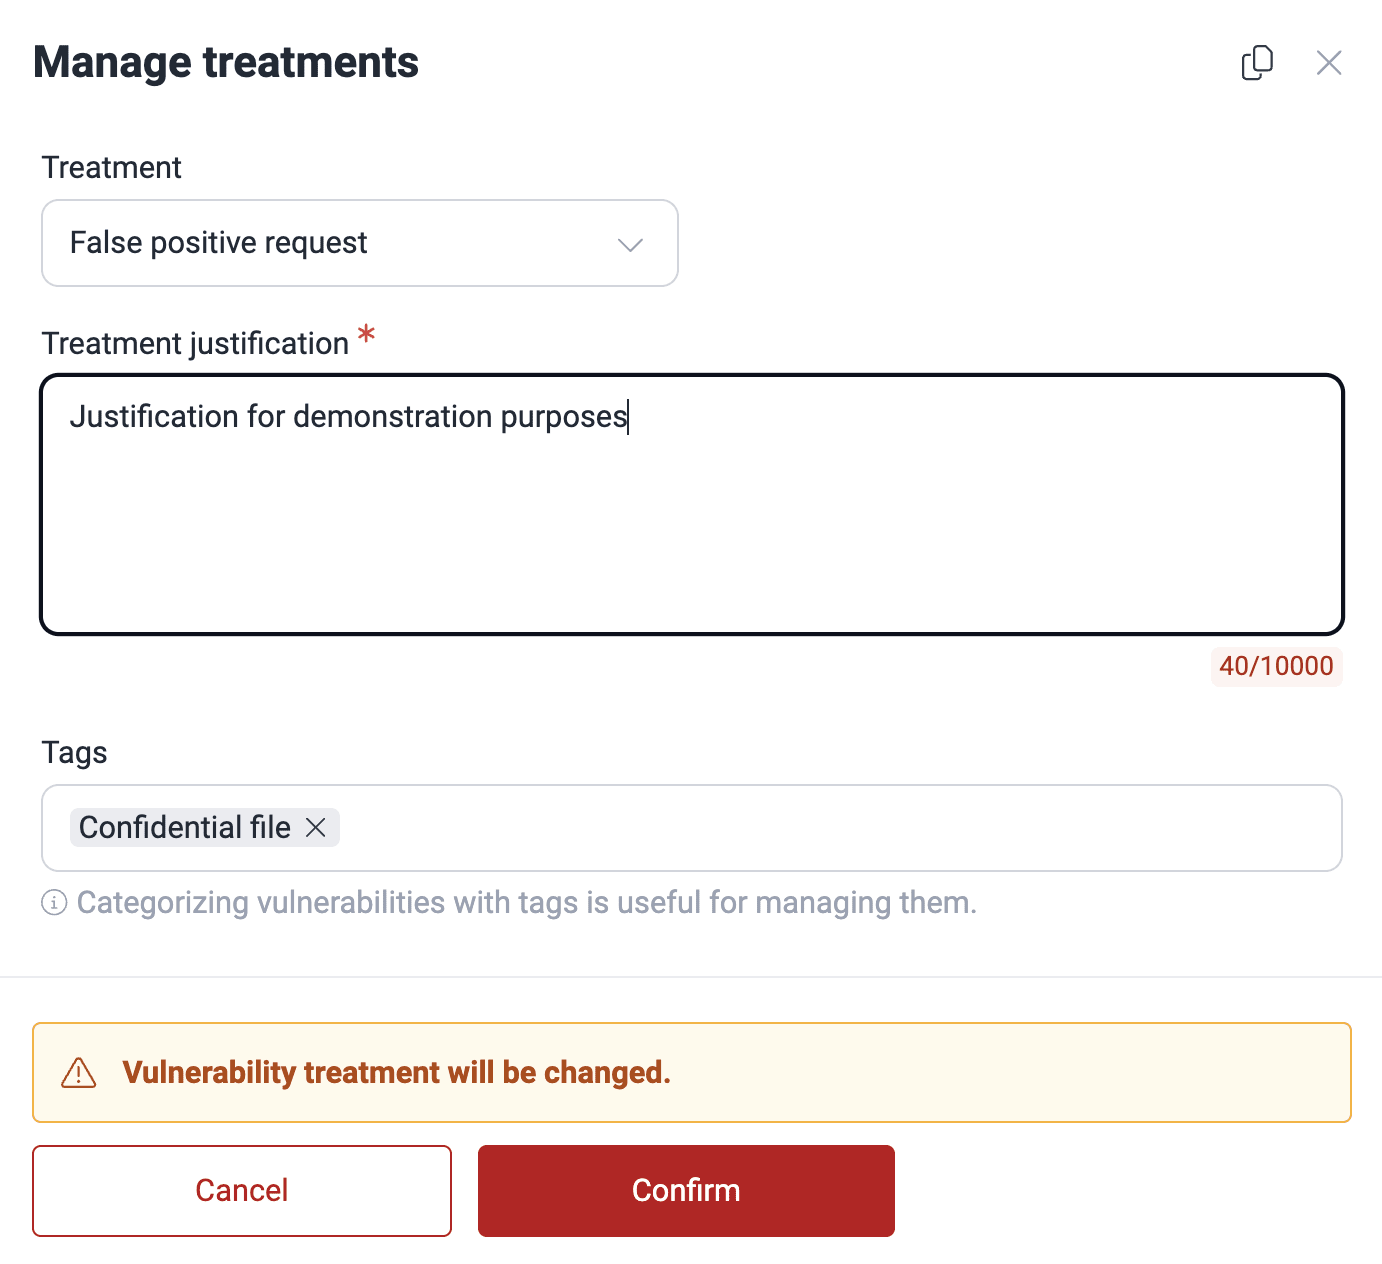
Write a justification for your request. If necessary, update the other fields.
-
Click Confirm.
The False positive column shows the decision of Fluid Attacks about your request.

Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Verify fixes with reattacks
Request reattacks on the Fluid Attacks platform to test the success of fixes addressing vulnerabilities. Understand reattack outcomes and troubleshoot errors.
Fraud risk center
See how your organization's open vulnerabilities map to fraud categories in the Fraud risk center, and request priority remediation.