Examine evidence
Last updated: Oct 26, 2026
Role required: User, Vulnerability Manager or Group Manager
The Evidence section of the Fluid Attacks platform gives proof that a type of vulnerability is in your software. If applicable, the pentesters also show in this section how they exploit the security issue. To see the evidence, follow these steps:
-
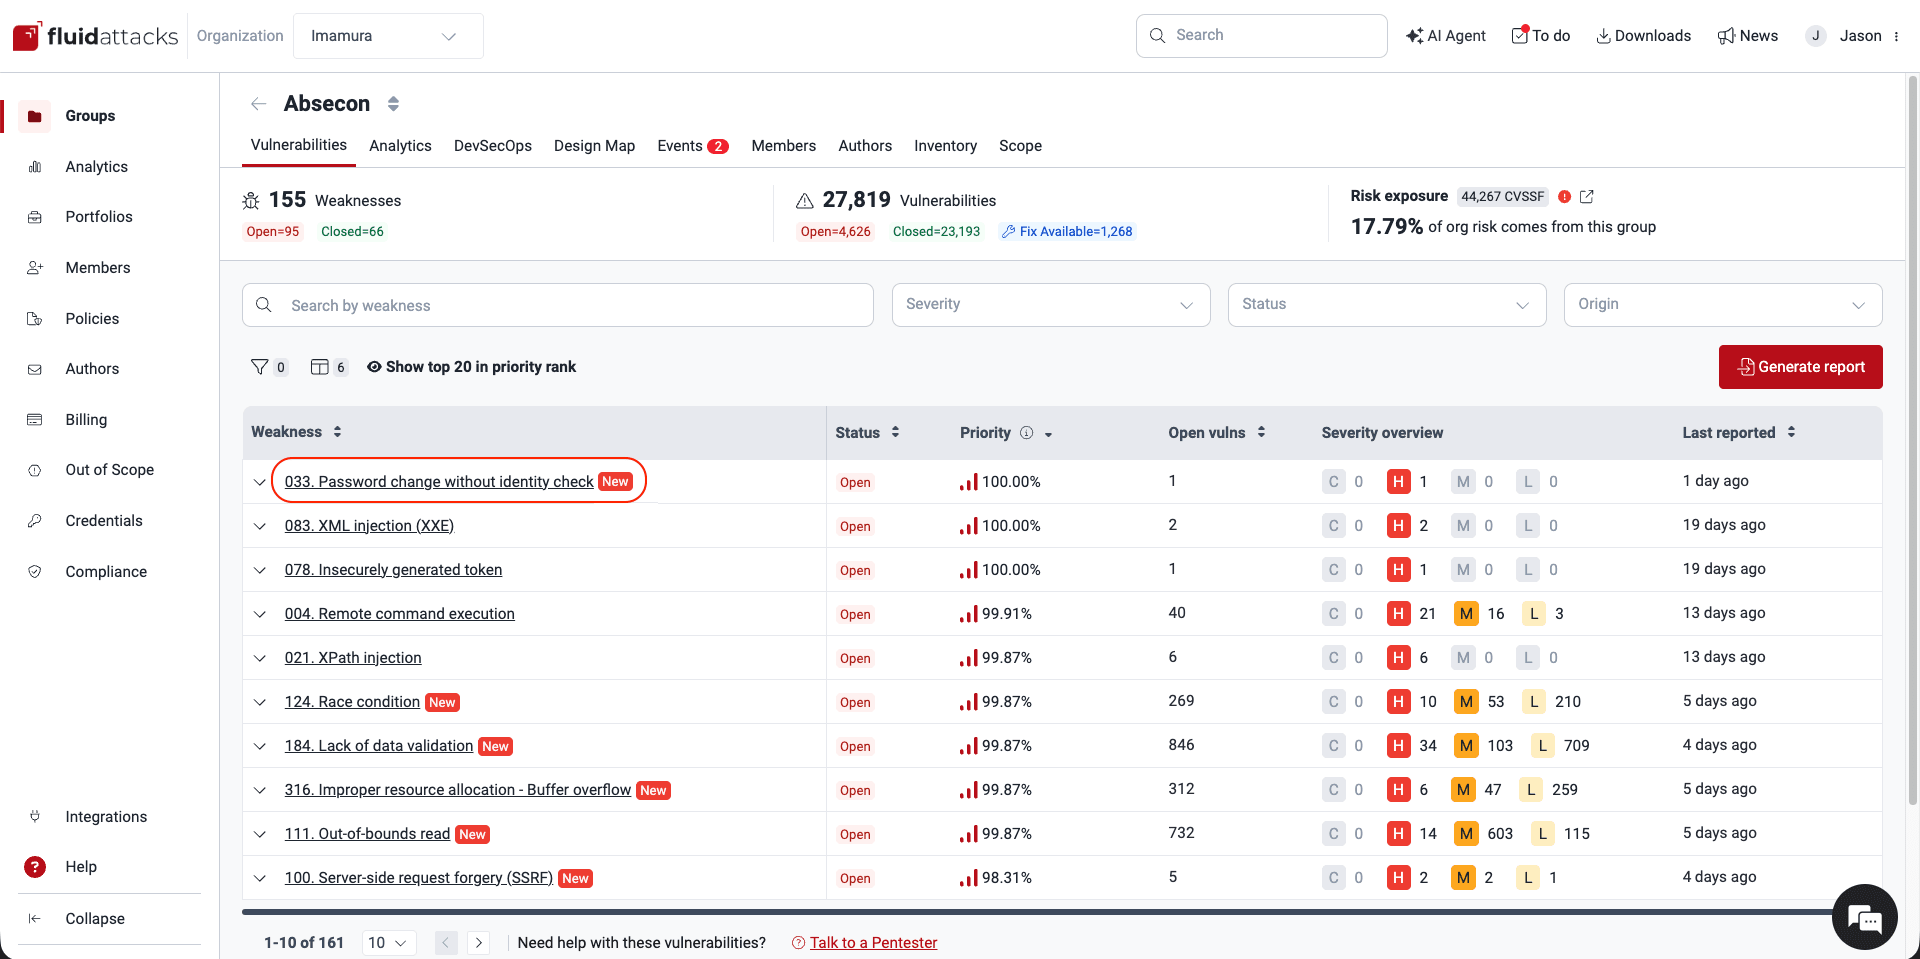
Go to the group where Fluid Attacks reported the weakness.
-
In Vulnerabilities, click the name of the weakness.
-
Go to the Evidence tab.
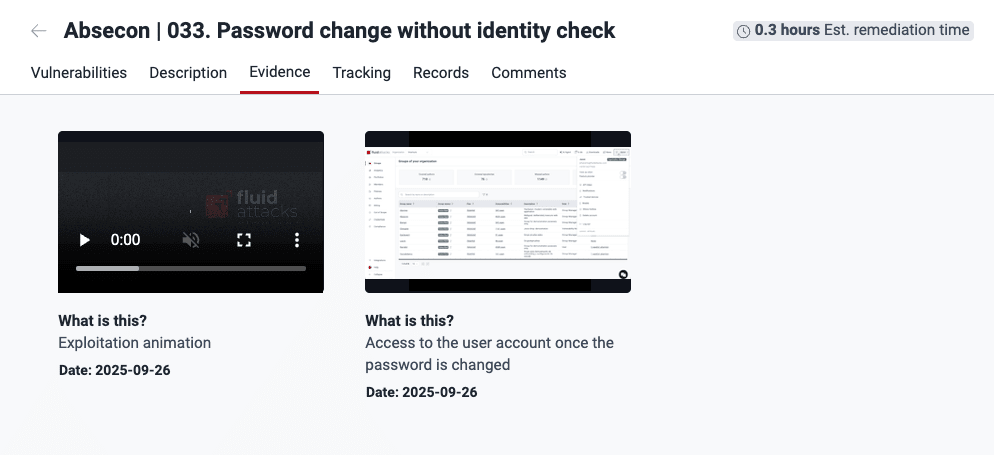
Click on a resource to enlarge it, and then you can download it.
Fluid Attacks gives the evidence as pictures (with the .png and .jpg extensions) and videos (with the .webm extension). The evidence shows that the vulnerability is in your system. If applicable, it also shows the real threat to the information in your system.
These are important points about the evidence:
- The evidence can change each time that Fluid Attacks does a reattack to examine if your fix removed the weakness.
- The maximum number of evidence items is twenty.
- Fluid Attacks can update the items if you request it in the Comments section.
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Vulnerabilities section guide
See information about reported vulnerabilities, like description, severity, vulnerable code, treatments, and fix recommendations on the Fluid Attacks platform.
Supply chain analysis
The Fluid Attacks platform allows you to track the security of software dependencies in your app, learn the reachability analysis results and download SBOMs.