Assign treatments
Last updated: Oct 26, 2026
A treatment is the decision that your organization makes about a vulnerability. This page shows how to apply treatments to reported vulnerabilities on the Fluid Attacks platform.
Define a treatment for a vulnerability
Role required: User, Vulnerability Manager or Group Manager (Users submitting acceptance treatments must have them approved by a Vulnerability Manager or Group Manager)
To define the treatment of a detected vulnerability, follow these steps:
-
Go to the group where Fluid Attacks reported the vulnerability.
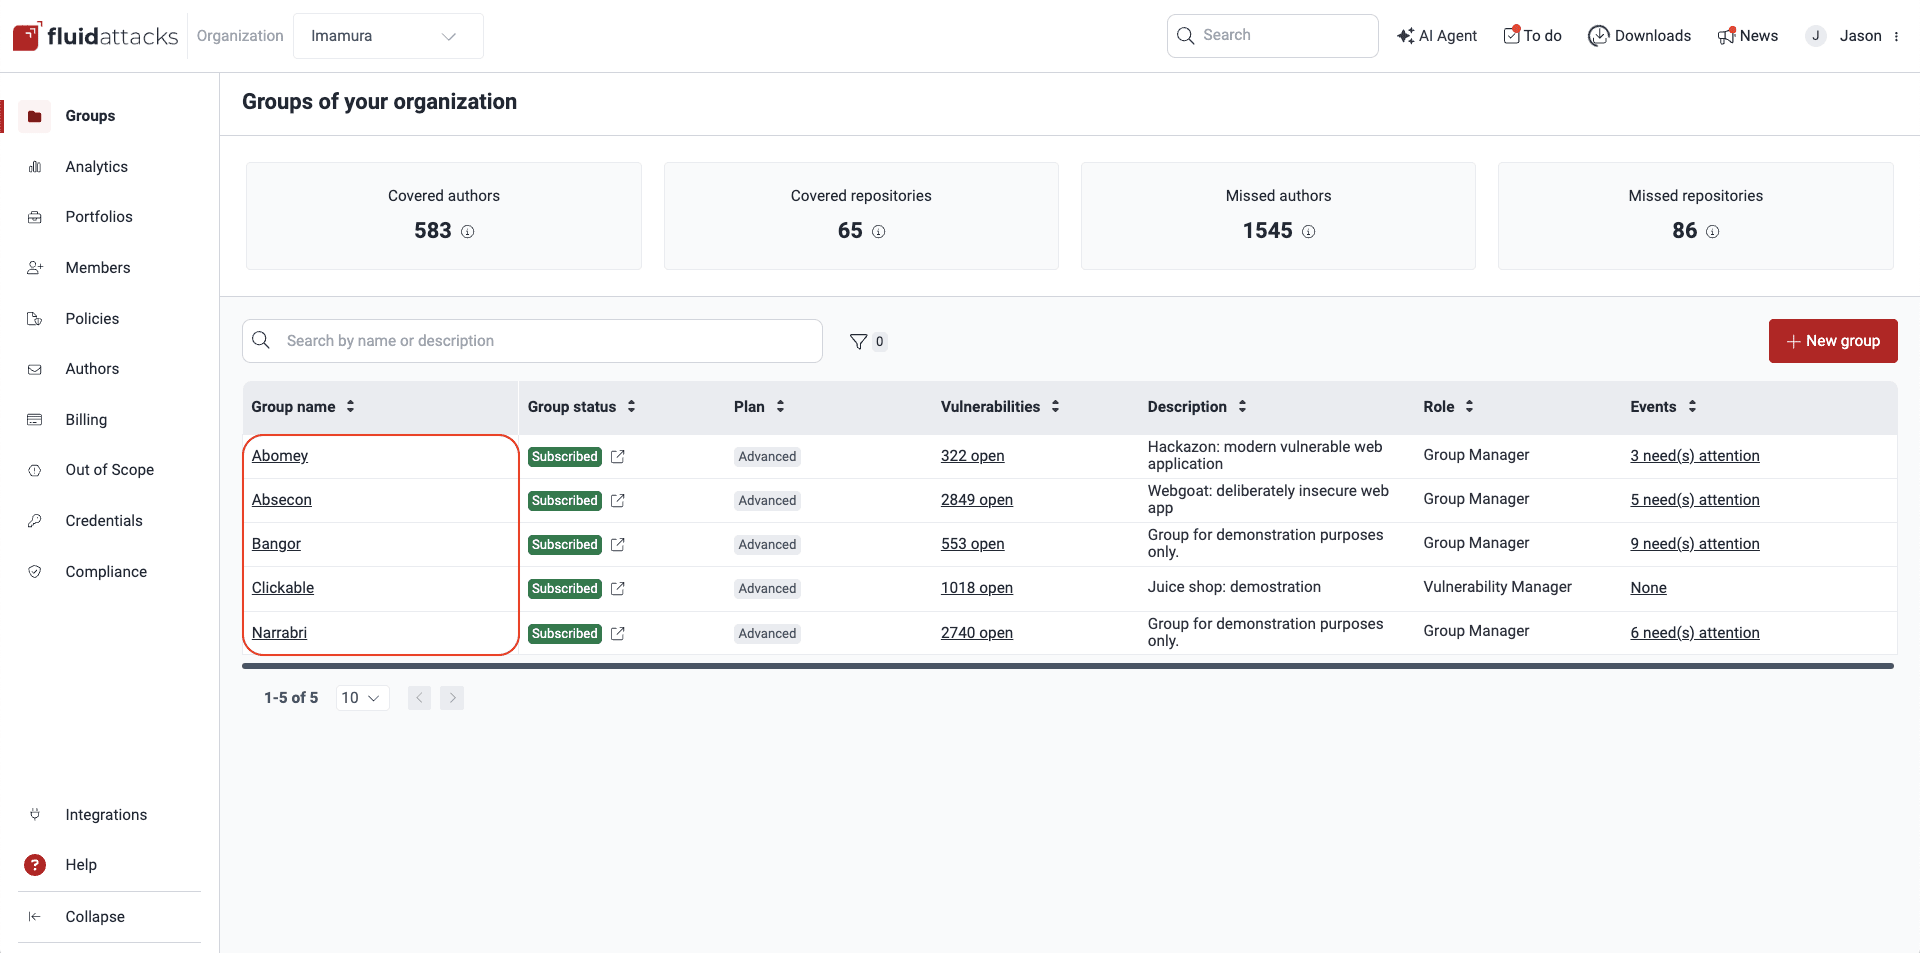
-
In the group's Vulnerabilities section, select the weakness. If you received a notification about the vulnerability, you can also go to Vulnerabilities directly from the email link.
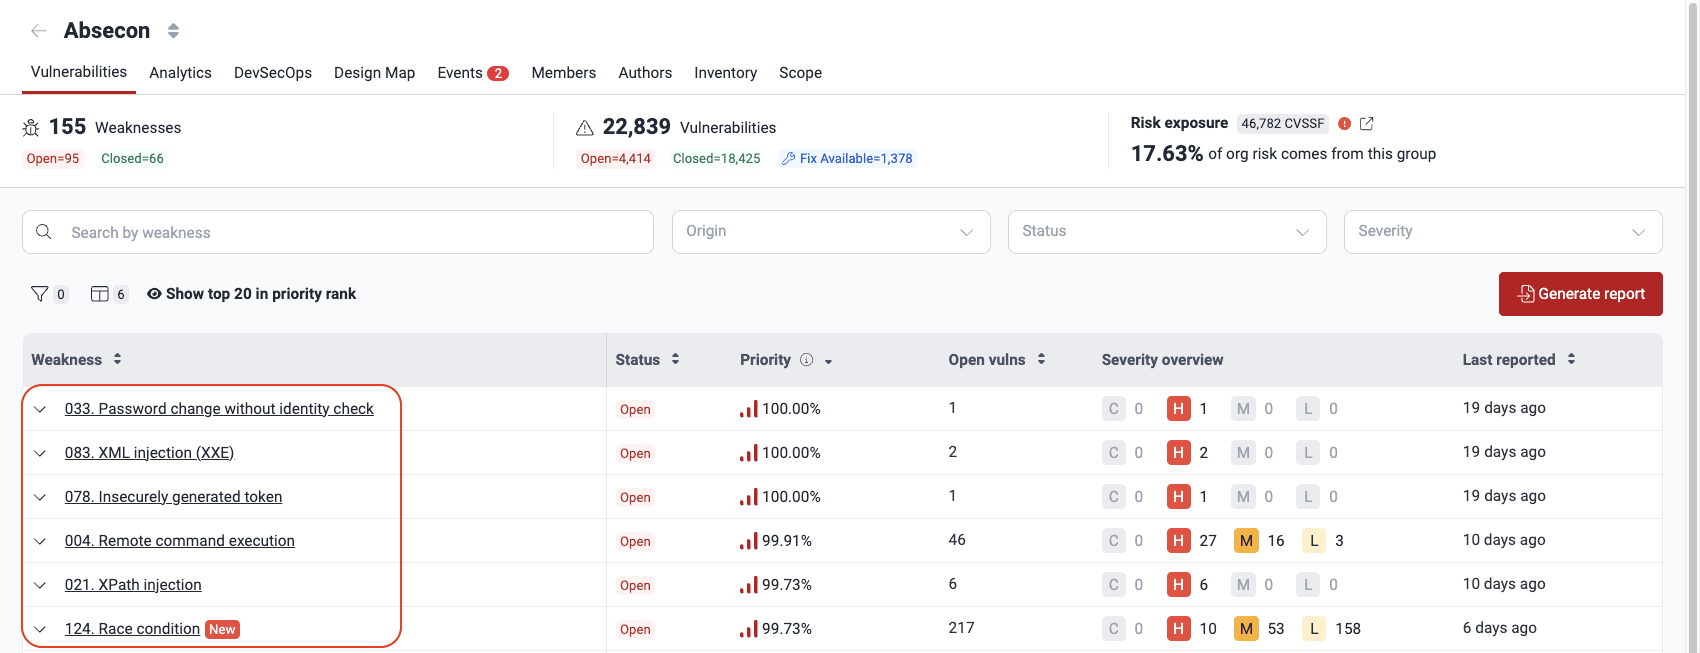
-
Find the vulnerability that you want to define a treatment for. Select the checkbox next to it. Then, click Edit treatment.
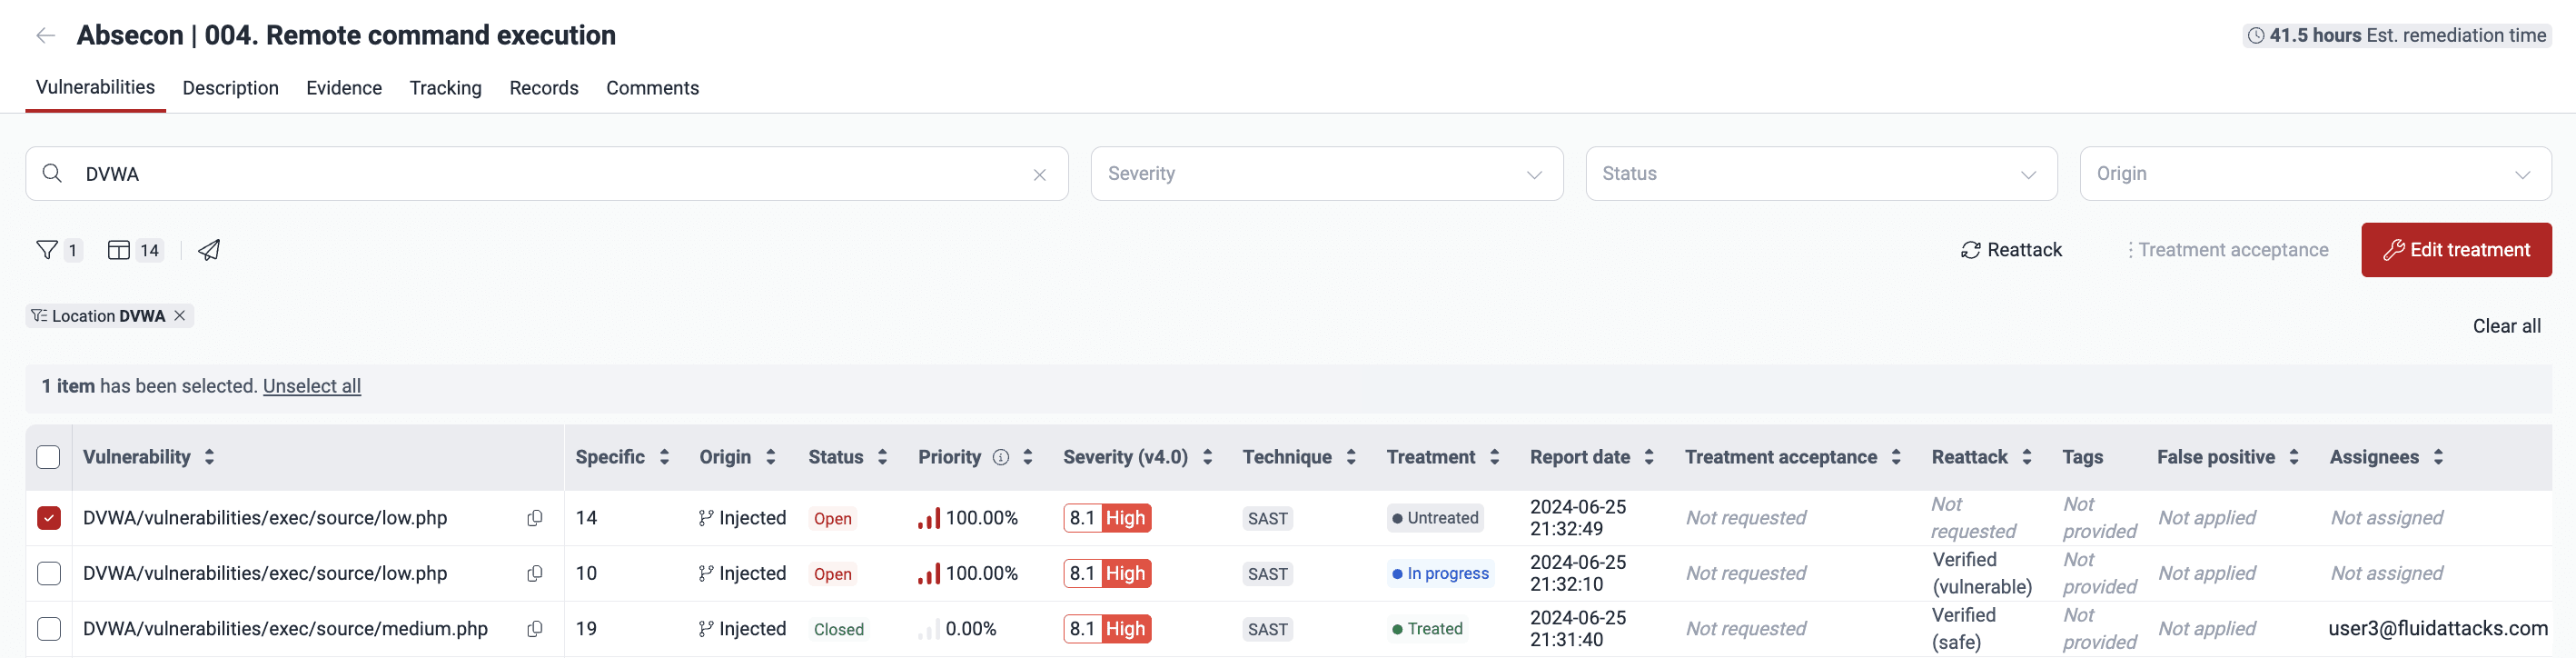
If assigning the same treatment to multiple vulnerabilities, you can select them and then click Edit treatment.
-
In the pop-up window, select the treatment for the vulnerability.
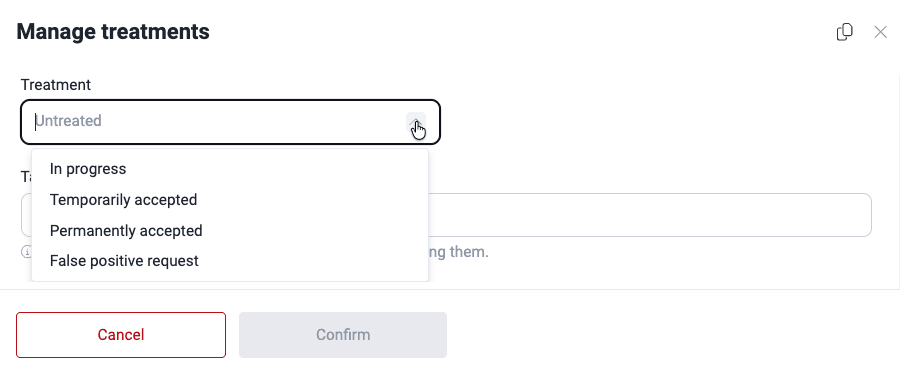
The Fluid Attacks platform has these treatments:
- In progress: Your organization agrees with the report and assigns the vulnerability to a member with the User role for remediation. After you assign the treatment, the member sees this vulnerability in their To do section.
- Temporarily accepted: Your organization accepts the vulnerability and its risks for a defined period. (You must specify a treatment date.)
- Permanently accepted: Your organization accepts the vulnerability and its risks with no end date. At any time, you can change a vulnerability with this treatment to 'In progress'.
- False positive request: Use this treatment when your organization finds that the vulnerability is not a threat. The platform sends a request to Fluid Attacks to remove the vulnerability from the report. If Fluid Attacks does not agree, the vulnerability stays in the report.
If you have the User role and select any of the acceptance treatments, your edit is handled as a request which has to undergo consideration by a member with the Vulnerability Manager or Group Manager role. Read further to learn how to approve treatments with these roles.
-
Complete the form with the necessary information.
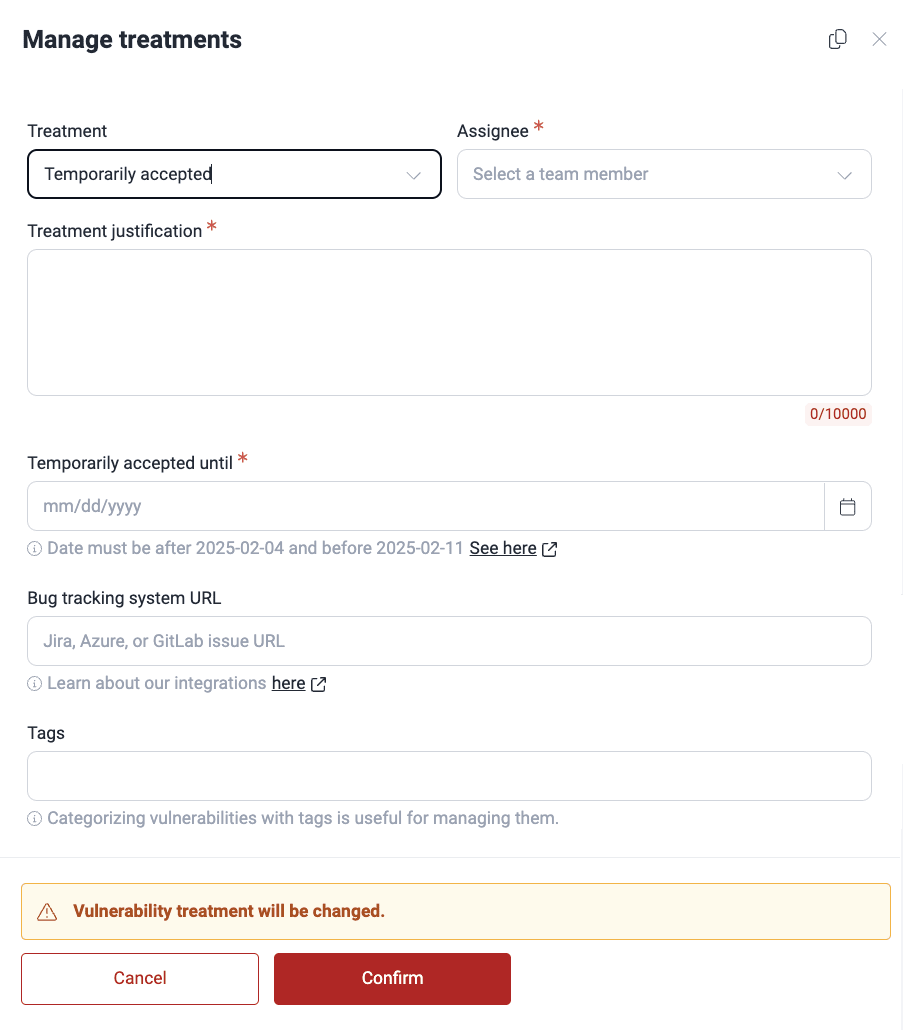
These are the descriptions of the other fields:
- Assignee: The member who must remediate the vulnerability (not shown when 'False positive request' is selected)
- Treatment justification: The reason for the treatment that you select
- Temporarily accepted until: The last date of the 'Temporarily accepted' treatment (shown only when you select this treatment)
- Tags:
Labels that help you put the vulnerability in a category and manage it (optional)
You can use tags to facilitate searching for vulnerabilities reported in the Locations table. Moreover, you can go to Analytics to see the number of vulnerabilities for each of the tags you or other team members have created.
- Bug-tracking system URL: URL of the issue in your bug-tracking system (BTS) related to this vulnerability (not shown when 'False positive request' is selected)
- Click Confirm.
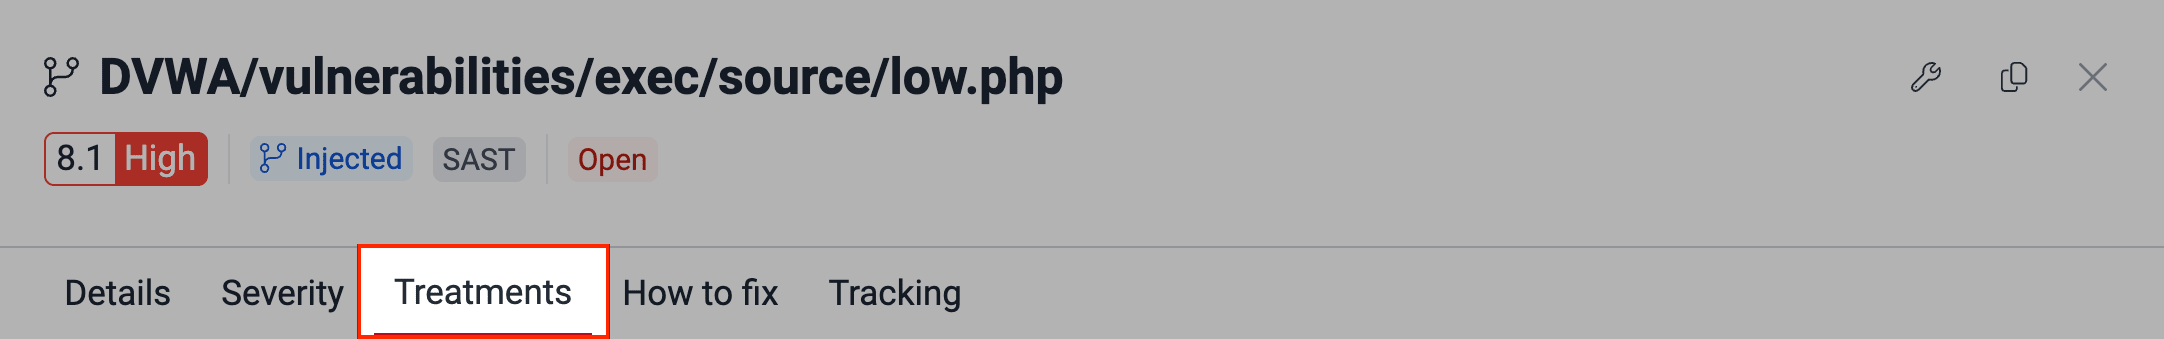
As an alternative for step 3, you can click the location of the vulnerability. Then, in the pop-up window, go to the Treatments tab and continue with step 4.
Assign fix work to members
Role required: Vulnerability Manager or Group Manager (members with the User role can only assign fix work to themselves)
To manage vulnerabilities, assign fix work to members. Thus, each vulnerability has a member who must remediate it, and your team remediates the identified vulnerabilities on time. To assign fix work on the Fluid Attacks platform, follow these steps:
-
Go to your group's Vulnerabilities section.
-
Select the weakness. If you received a notification about it, you can also go to the weakness directly from the email link.
-
In the Vulnerabilities section of the weakness, select the vulnerability that you want to assign to yourself or to a team member.
To do this, you can either (a) click the check box next to the vulnerability and then the Edit button or (b) click on the vulnerability's location and then, in the pop-up window, switch to the Treatments tab.
-
Select the 'In progress' treatment and choose the assignee.

-
In Treatment justification, write the necessary instructions or the reason for the assignment.
-
If necessary, change other values (read the descriptions above).
-
Click Confirm to apply the treatment.
- Only Fluid Attacks staff can assign vulnerabilities to other staff members.
- Vulnerability Managers and Group Managers can assign vulnerabilities to any group member except for Fluid Attacks staff.
- The Assigned dropdown list will only show valid options for assignment.
- You can assign 'Untreated' vulnerabilities for remediation choosing 'In progress', reassign 'In progress' vulnerabilities, and even assign ‘Temporarily accepted’ and ‘Permanently accepted’ vulnerabilities.
The newly assigned member receives an email notification that tells them which vulnerability they must remediate and the group where it is. The members who subscribed to treatment updates notifications also receive an email about the assignment. In the two cases, the email has a link to the related Vulnerabilities section.
The assigned member can find the new task in their To do section. To go to this section, use the menu at the top right. A red dot on the icon of this section shows that remediation work is pending. To learn how to use this section, read See vulnerabilities assigned to you.

Approve or reject vulnerability acceptance treatments
Role required: Vulnerability Manager or Group Manager
On the Fluid Attacks platform, you can accept vulnerabilities temporarily or permanently. This means that your team does no fix work on them for a defined period or with no end date. You receive emails about the acceptance requests of your team when these conditions are true:
- You have the Vulnerability Manager or Group Manager role.
- The Treatment updates notification is on.
You have a deadline of five days to approve or reject each request. If you do not respond, the vulnerability's treatment changes back to 'Untreated' or 'In progress', the treatment that it had before the request. To respond to acceptance requests, follow these steps:
-
Find the vulnerability. Use the link in the email, or go to the Vulnerabilities section of your group and open the Vulnerabilities section of the weakness.
-
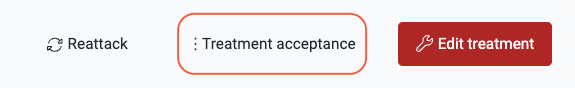
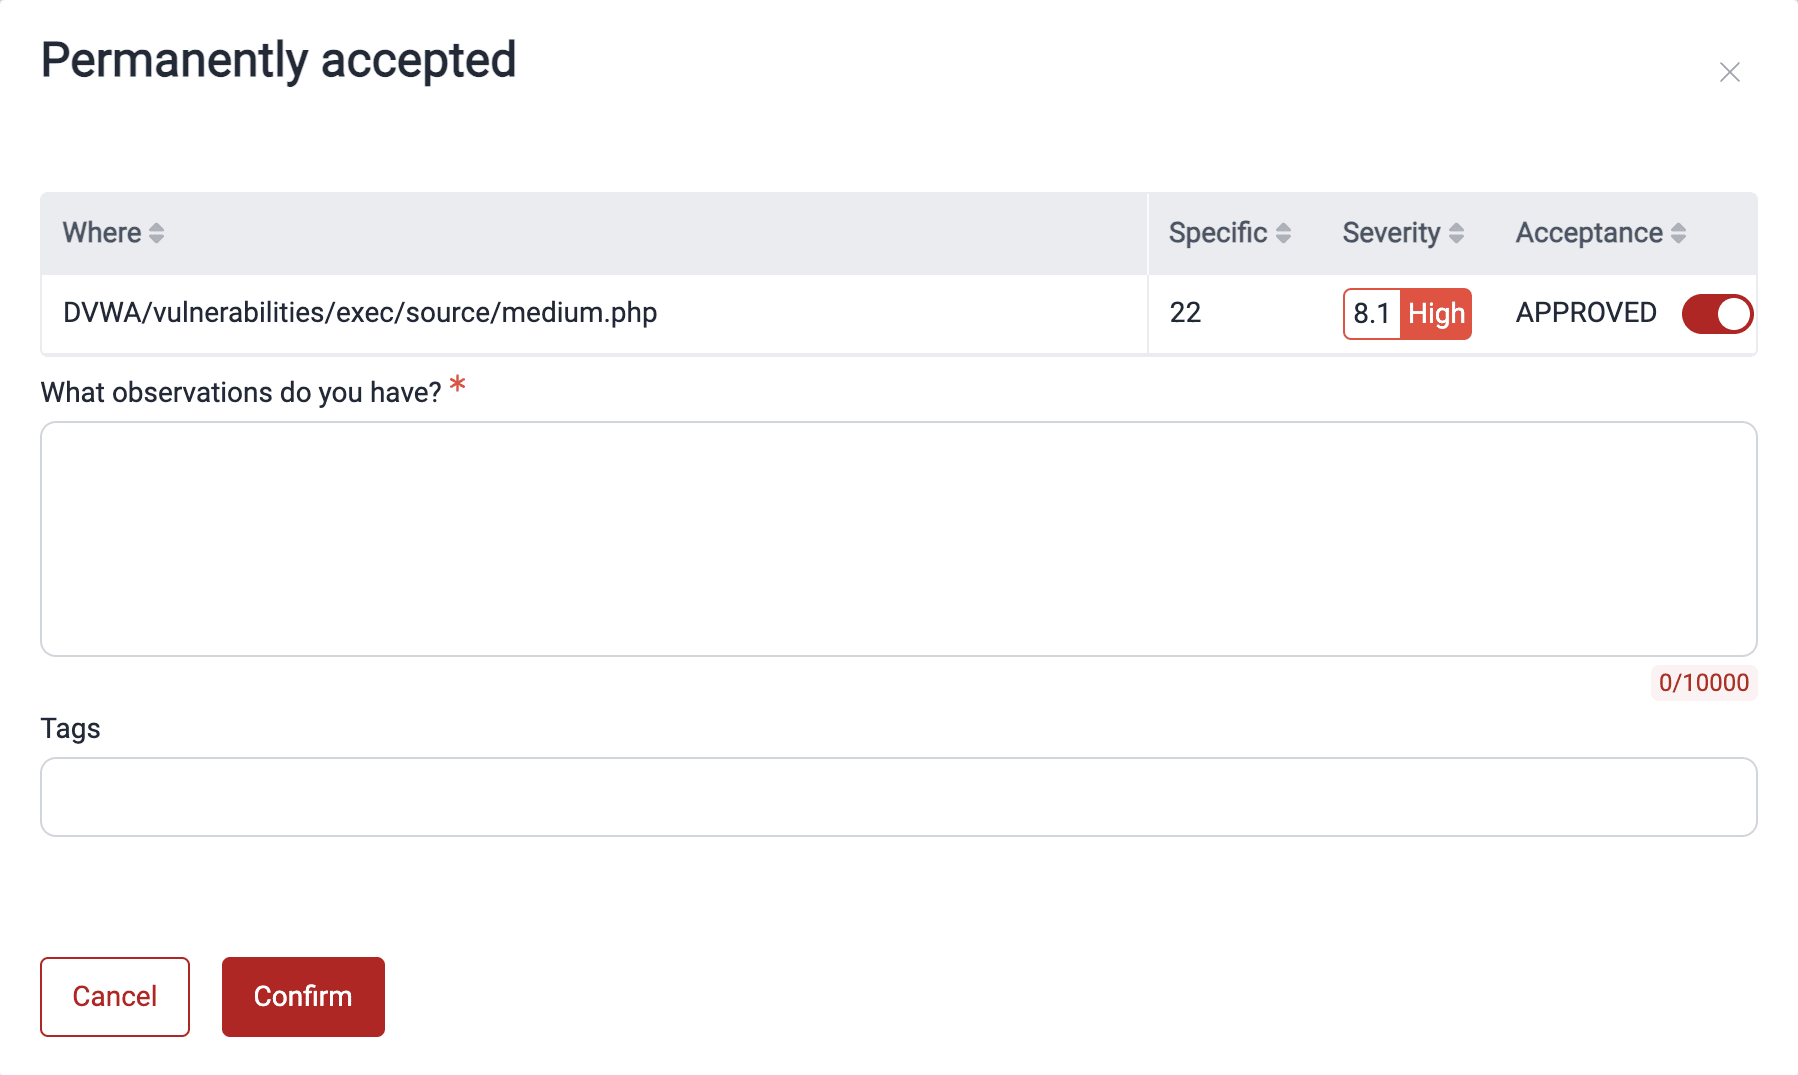
Click the Treatment acceptance option.
-
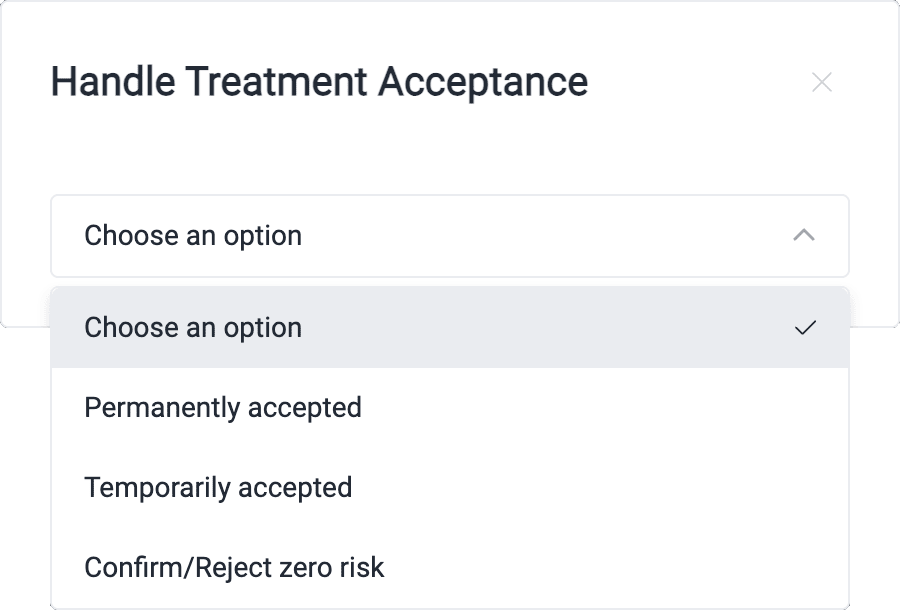
In the pop-up window, select the treatment request.
-
Use the toggle to approve or reject the request. Then, write your feedback.
-
To apply your decision, click Confirm.
If you reject the request, the treatment of the vulnerability changes back to 'In progress' or 'Untreated', the treatment that it had before the request.
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Correlate threat models
Discover the correlation between your threat model and vulnerabilities reported by Fluid Attacks. Then, prioritize remediation based on your business risks.
Assigned to you
The To do section on the Fluid Attacks platform enables users to visualize vulnerabilities assigned to them, change treatments and request reattacks.