Reachability analysis
Last updated: Oct 26, 2026
Fluid Attacks' static code scans detect third-party dependencies used in your software. The scans also check if your software uses the vulnerable functions of the dependencies. With the Reachability feature of Fluid Attacks, you can know if threat actors can reach the detected dependency vulnerabilities.
Know which dependencies have vulnerabilities
Fluid Attacks helps you understand your software supply chain. It identifies the dependencies in your software and shows which of them have vulnerability advisories.
On the platform, the Packages section shows this information. It also shows details such as the location of the dependency in your projects and if it contains malware.
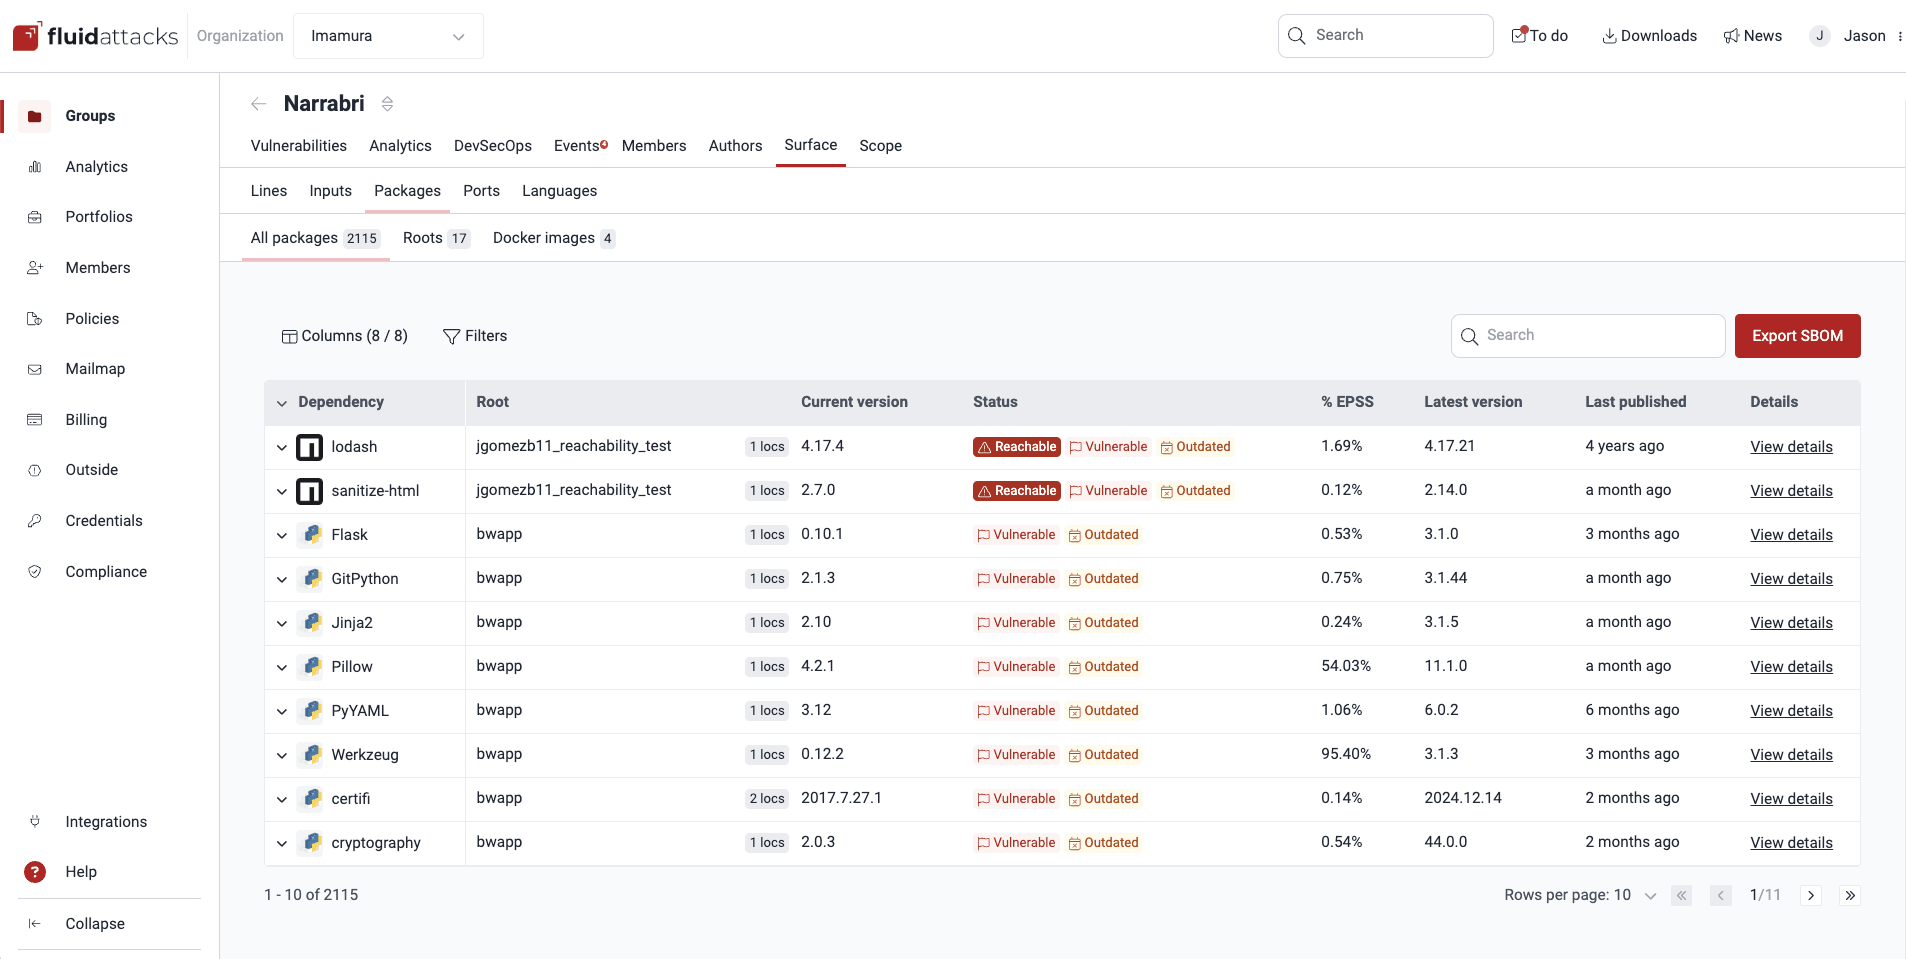
This section shows the dependencies with related advisories as "Vulnerable". It also shows which of them are "Reachable". To find the reachable dependencies, Fluid Attacks identifies if your application calls a function or a different code element related to the vulnerability. If it does, there is a higher risk that the vulnerability is exploitable in the context of your application.
Know reachable dependency vulnerabilities
With the Reachability feature, Fluid Attacks' scans find where your software uses the vulnerable functions of the third-party dependencies. If the scans show that these dependencies put your software at risk, you get the related vulnerability reports. On the platform, Fluid Attacks reports each reachable vulnerability
- in the Packages section with the tag "Reachable"
- in the Vulnerabilities section, in its weakness.
From the Packages section, to find where the vulnerability is in your project, follow these steps:
-
Expand the row.
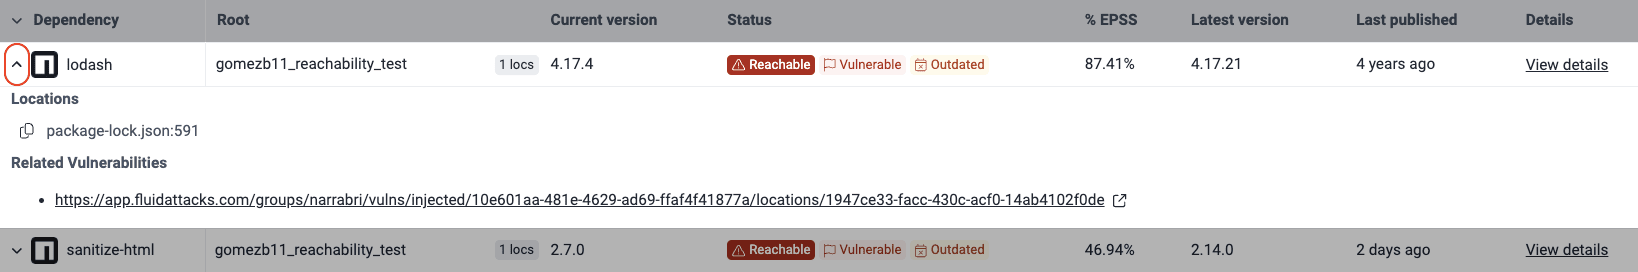
-
Click the link in Related Vulnerabilities.
-
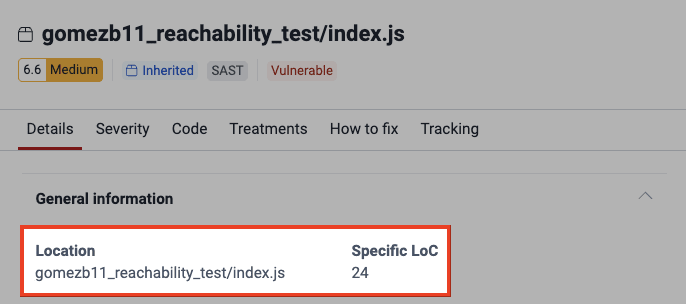
Identify the file path and line of code (LoC) that calls or leads to the vulnerable function.
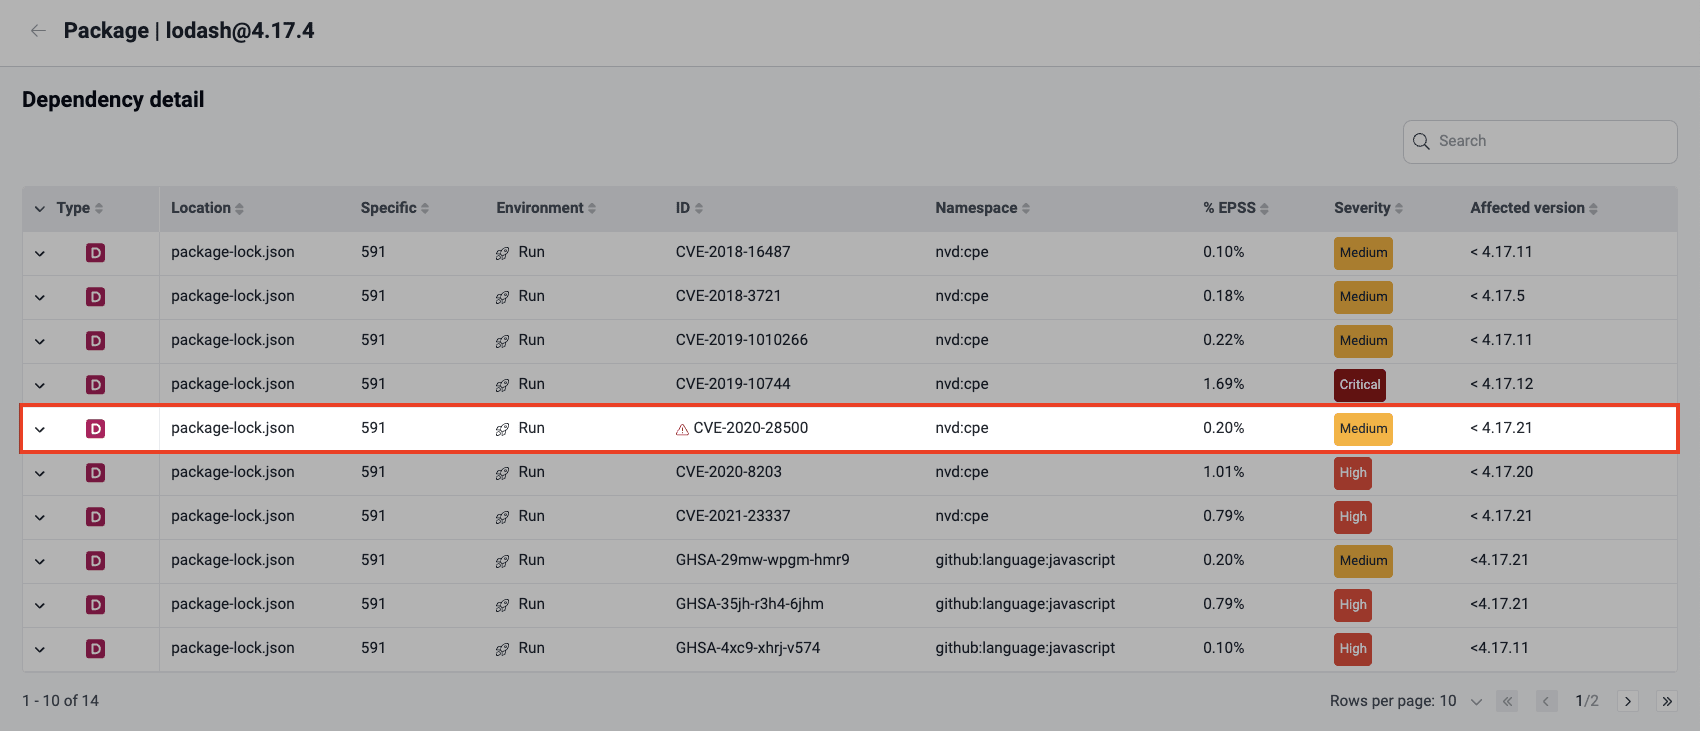
In the Packages section, if you click View details, you can see the reachable dependency vulnerability. A warning sign shows next to its CVE ID.
From the Vulnerabilities section, to identify a reachable dependency vulnerability, follow these steps:
-
Select a weakness.
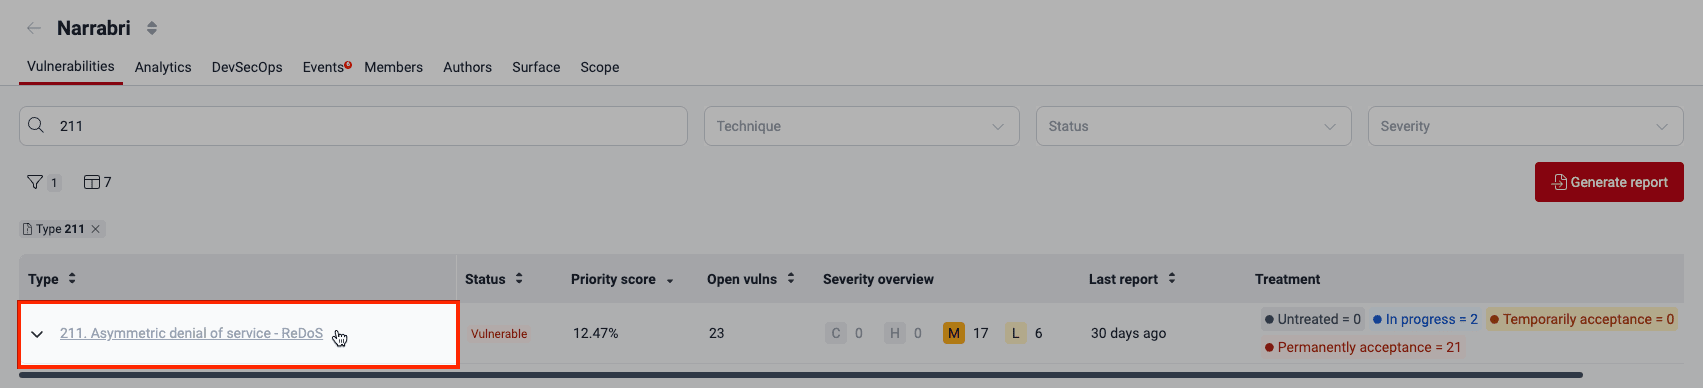
-
Select a vulnerability whose Origin is "Inherited".
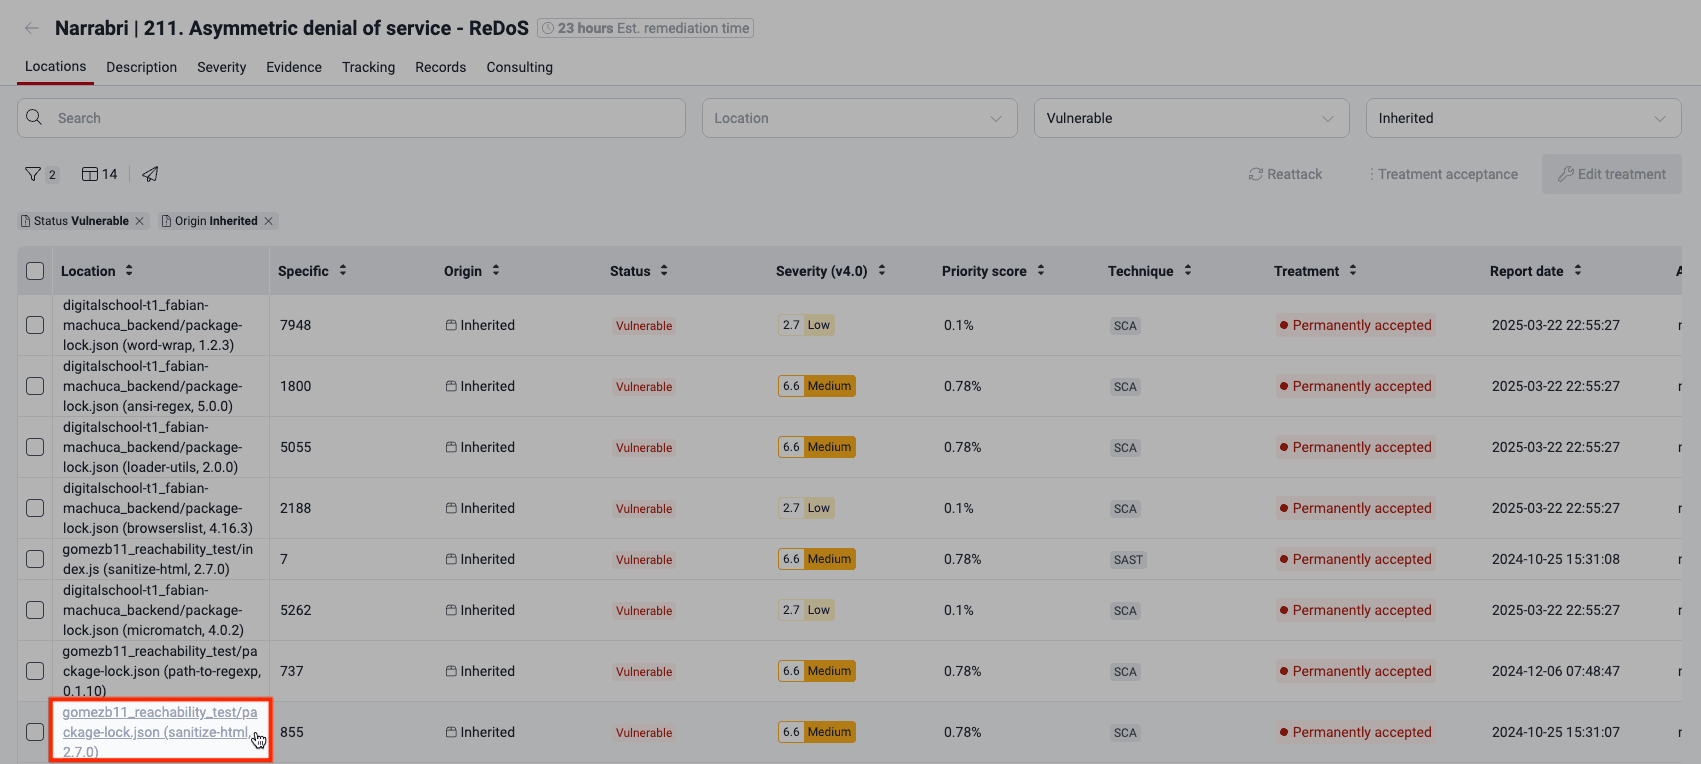
-
In Packages details, find the information about the vulnerable dependency version that you use and if its vulnerability is exploitable.
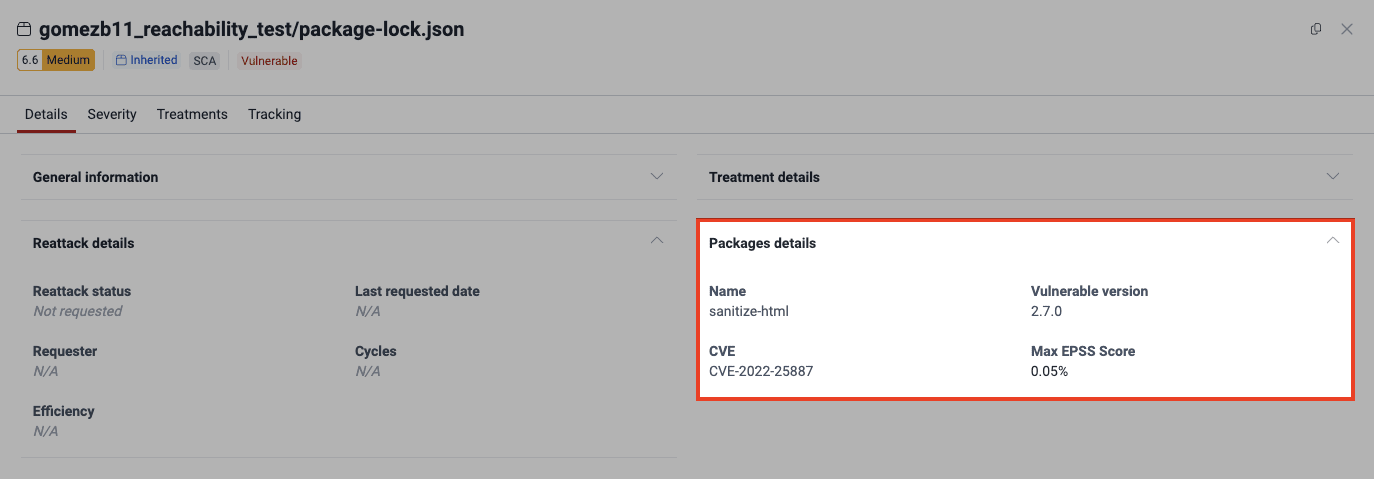
Also, in the Evidence section of the weakness, you can see a screenshot of your vulnerable code in context. The screenshot also shows the CVE ID reported for the dependency.
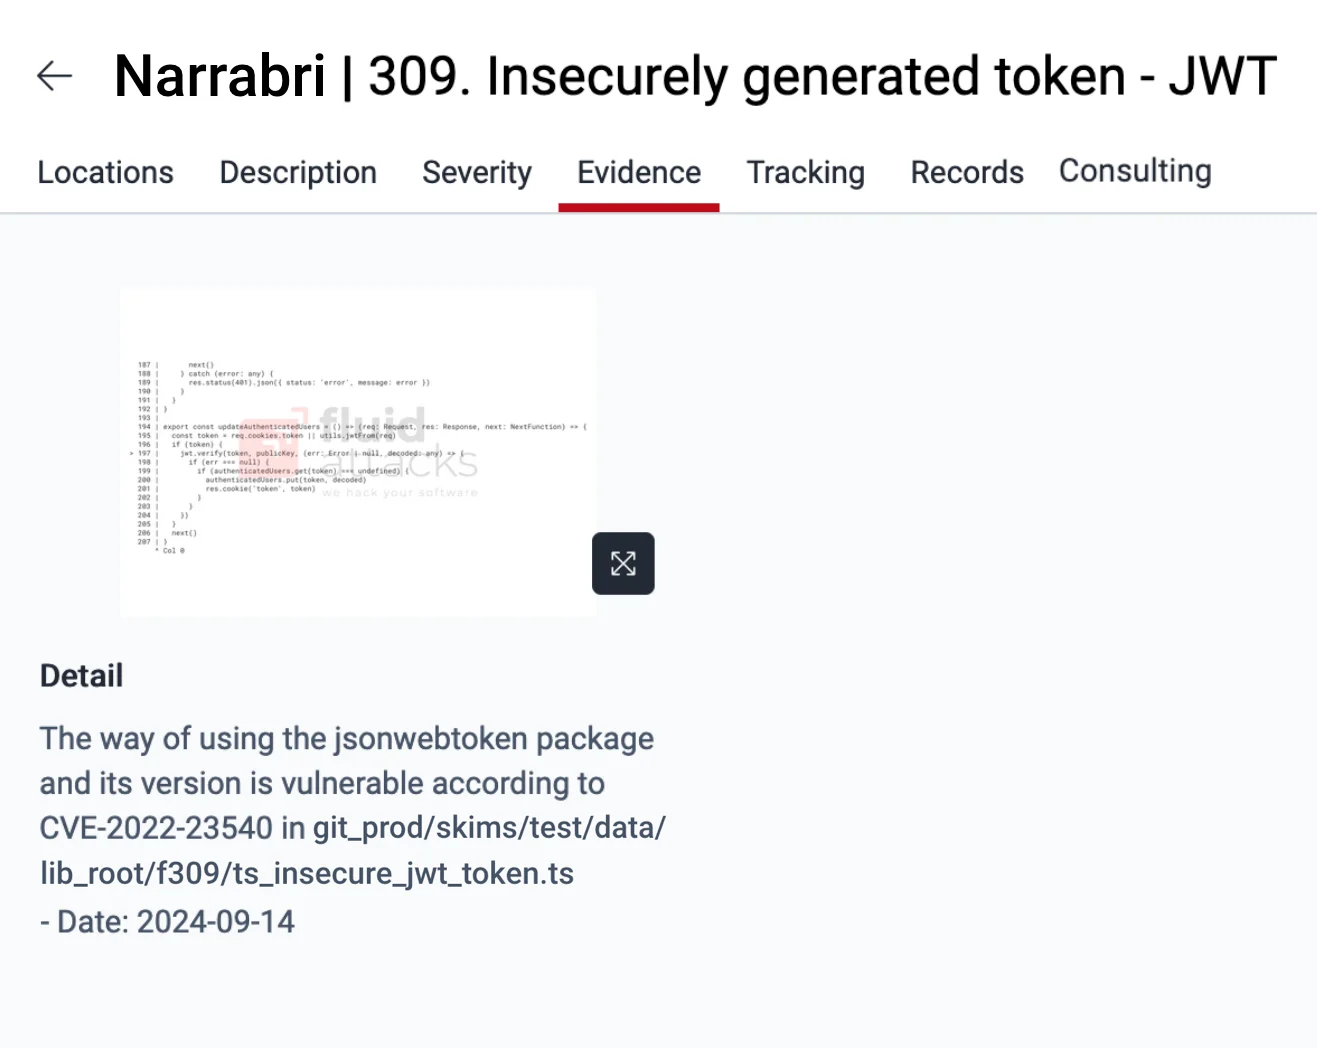
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Supply chain analysis
The Fluid Attacks platform allows you to track the security of software dependencies in your app, learn the reachability analysis results and download SBOMs.
Vulnerability signature update
Learn about the Fluid Attacks vulnerability signature management for software composition analysis SCA scans.