Request reattacks
Last updated: Oct 26, 2026
If you do not have the Jira integration, install it.
Permission required: To request reattacks from Jira issues, you must have permission to assign issues or to receive issue assignments.
With the Jira integration of Fluid Attacks, you can request reattacks from Jira issues. In a reattack, the tools or pentesters of Fluid Attacks examine your fixes to code or configurations to learn if the fixes removed the reported vulnerabilities.
Do these steps to request a reattack from a Jira issue.
-
In your Jira Cloud instance, open the project where Fluid Attacks reported the vulnerability to reattack.
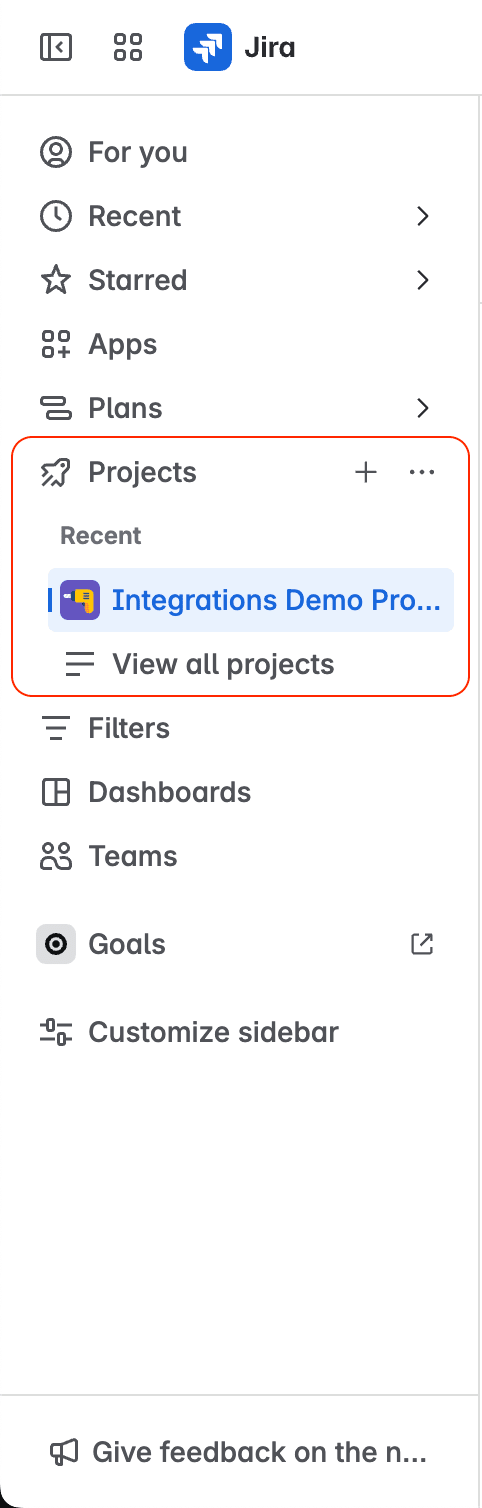
-
Click the Fluid Attacks option in the project menu.
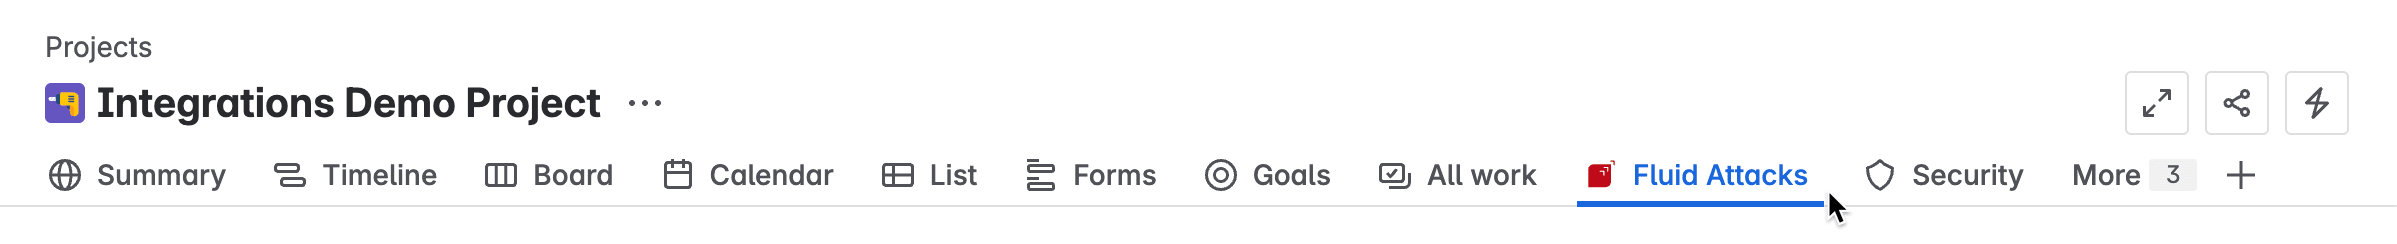
-
Find the vulnerability to reattack. Then click View.

-
Scroll down the section on the right side to find the Reattack button.

-
In the Justification field, write the solution that you applied to the vulnerability. Then click Reattack.

The status next to View on platform changes from 'Vulnerable' to 'Reattack requested'. If your fix is successful, the integration adds a comment to the issue. Jira then sends a notification to all persons who watch the issue.
The Fluid Attacks response service-level agreement applies to the reattacks that the Fluid Attacks pentesting team does. To learn about reattack results and what to do if an error occurs when you send your request, read Verify fixes with reattacks.
If the reattack result is not what you expected, learn how Fluid Attacks can help you fix your code.
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Vulnerability details in Jira
Use this Jira integration feature to access from an issue to the links to see evidence, locations and more details of vulnerabilities found by Fluid Attacks.
App help options
Use this Jira integration feature to access from an issue to the links to request help sessions with Fluid Attacks' ethical pentesters and create tickets.