Group analytics
Last updated: Oct 26, 2026
Analytics sections are updated daily at 1:00 a.m. (UTC) from Monday to Friday. The values shown depend on preprocessed data updated Tuesdays through Saturdays at 7:00 p.m. (UTC). Please note that there may be brief periods after the Analytics update time when the section may experience a slight delay in data reflection.
Role required: User, Vulnerability Manager or Group Manager
The Analytics sections of the Fluid Attacks platform show charts and figures about the status and characteristics of vulnerabilities and your remediation practices. This page describes the charts that give information at the group level.
Hover over charts to see available options.
Vulnerabilities closing reason
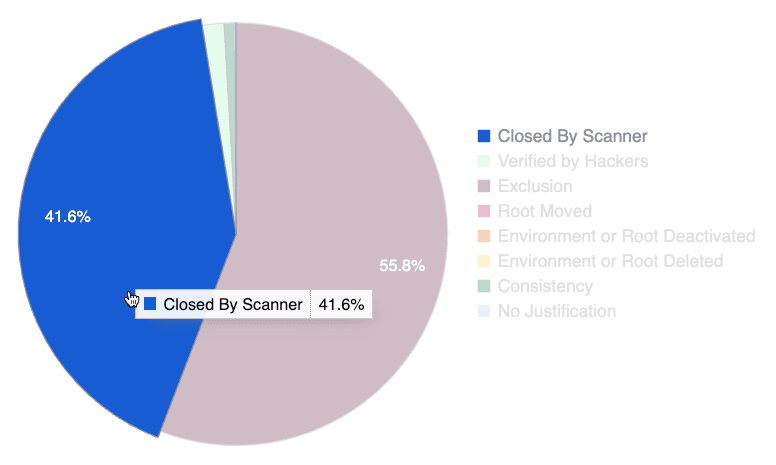
This chart shows the percentage of each reason that changed the status of vulnerabilities in the group from "Vulnerable" to "Safe." A vulnerability can close when a reattack of Fluid Attacks shows that your team fixed it. It can also close for other reasons, for example, when you deactivate or move a root.
You can use the chart in these ways:
- Hover over a slice to see the reason and percentage information.
- Hover over a chart legend to highlight the related slice in the chart.
- Click a chart legend to exclude the related reason from the percentage calculation.
Group availability time
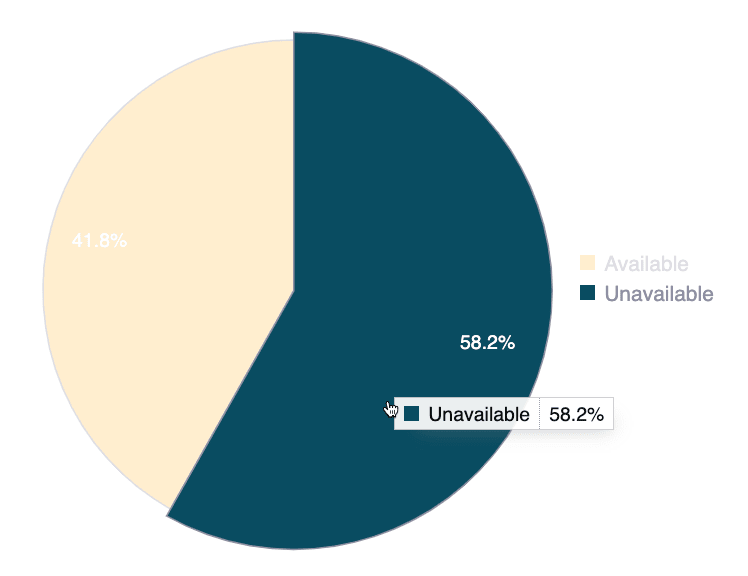
The group availability metric shows the percentage of time that the group had unresolved events since its creation. During an event, the tool or the pentesters of Fluid Attacks cannot test part or all of the scope of the group.
This information shows how quickly the group makes complete assessments possible.
You can use the chart in these ways:
- Hover over a slice to see the status and percentage information.
- Hover over a chart legend to highlight the related slice in the chart.
- Click a chart legend to exclude the related status from the percentage calculation.
Total exclusions
This figure is the total number of detected vulnerabilities that you told Fluid Attacks to exclude from reports. To learn the strategies to make these exclusions, read Exclude findings from scan reports.
Exclusions by repository
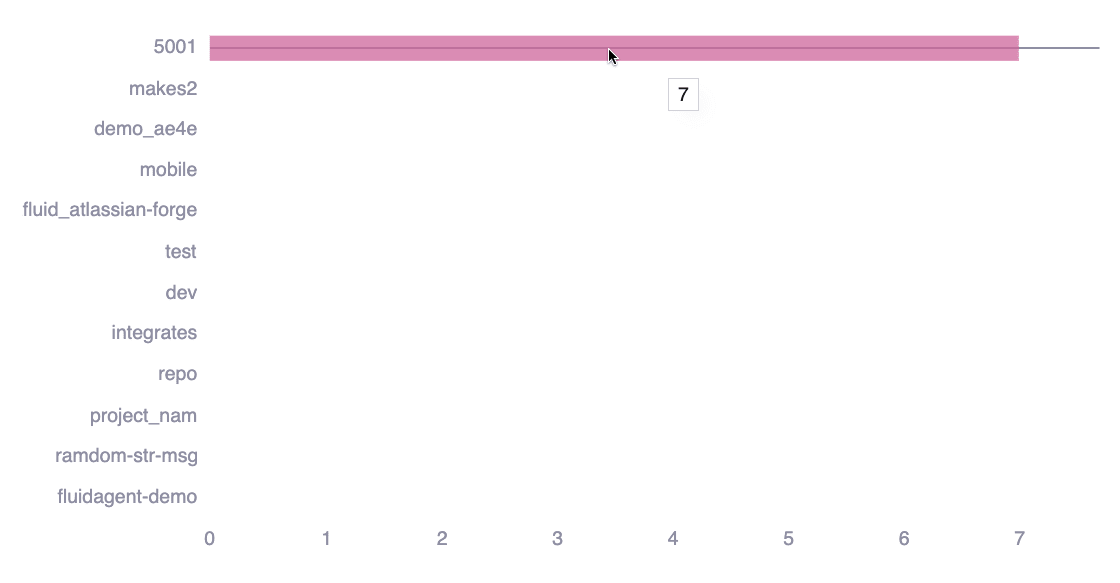
This chart shows the number of vulnerabilities excluded from reports for each of the Git repositories of your group.
Hover over a bar to see the exact number of exclusions.
Days since group is failing
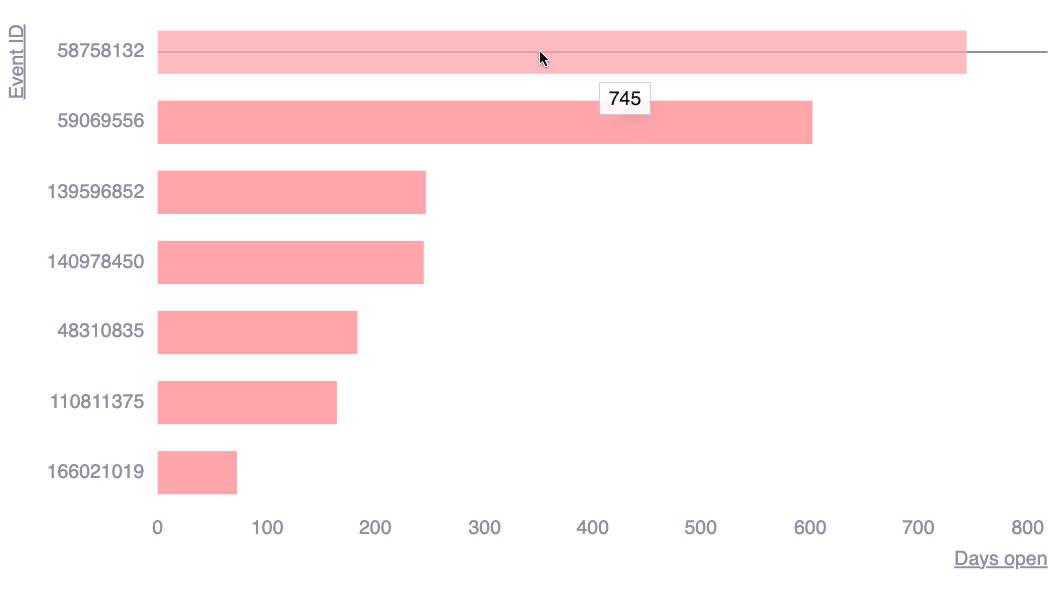
This chart shows the number of days that each event in your group is unresolved. This information helps you prioritize issues that are open for a long time.
Hover over a bar to see the precise number of events.
Weaknesses by tags
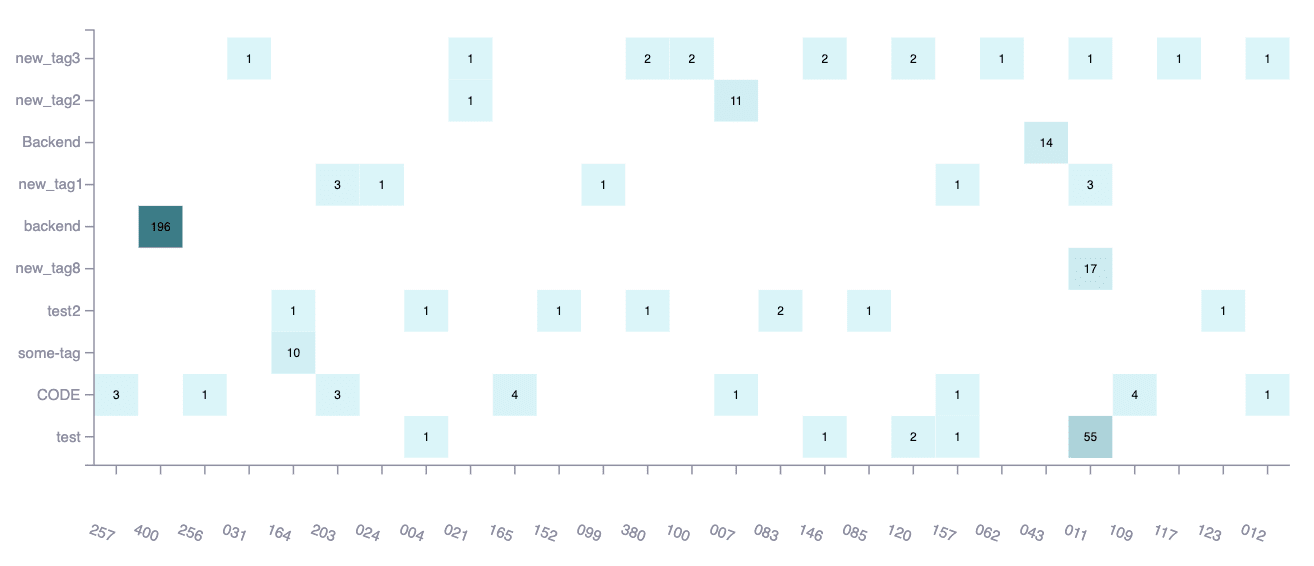
This chart shows how many times each of your tags is used in the reported types of vulnerabilities. You can see vulnerability tags in the Vulnerabilities section and add them when you edit vulnerabilities. This helps you analyze security issues in your group with categories that are important for your team.
A type of vulnerability refers to the category into which a detected security issue most likely falls.
CI Gate-related analytics
When you enable CI Gate, you can verify the status of security vulnerabilities in your system. You can put this application, which is a Docker container, in your continuous integration system. It gives you these benefits:
- You run fast and automatic scans on your new code.
- If you want, you can set CI Gate to break the build if it finds noncompliance with your organization policies or group-specific policies. You can customize this strict mode with severity thresholds and grace periods that your team sets.
- Statistics from over a hundred different systems show that when CI Gate breaks the build, it increases the remediation ratio and speed. This helps you build a safer system and decrease remediation costs in all the stages of your software security development lifecycle (SDLC).
Service status
This shows if Fluid Attacks' CI Gate is Active or Inactive.
Service usage
This figure is the number of times that your team ran CI Gate to check the status of vulnerabilities in your builds.
Repositories and branches
This figure is the number of repositories and branches that you check with CI Gate.
Your commitment towards security
The primary objective of CI Gate is to control the deployments of your team. Your team is responsible for important vulnerability management settings that change how CI Gate works, such as these:
- CI Gate's strict mode: The strict mode is enabled by default. If CI Gate detects vulnerabilities that are not fixed, it stops builds or deployments. This helps to make sure that vulnerable code does not go into your system.
- Vulnerability acceptance: CI Gate always ignores vulnerabilities that your team accepted on the Fluid Attacks platform, also in strict mode. Thus, your team controls if CI Gate continues with builds or deployments.
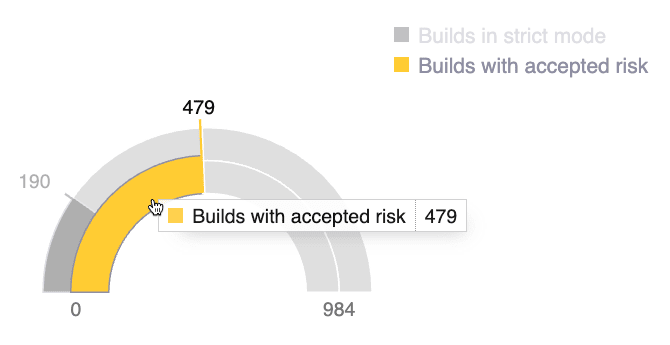
This chart shows the number of CI Gate executions with strict mode enabled and the number of executions that found accepted vulnerabilities. With this information, your team can set goals to keep the accepted risk low and the use of strict mode high.
You can use the chart in these ways:
- Hover over a part to see the status and number information.
- Hover over a chart legend to highlight the related part of the chart.
- Click a chart legend to hide the related status from the visual comparison.
Builds risk
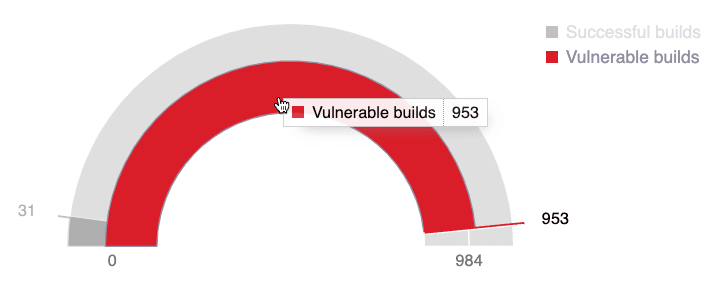
This chart shows the number of CI Gate executions that found vulnerabilities and the number that found no vulnerabilities. The DevSecOps section of the group shows the details. This information helps you understand how well your team prevents risky deployments.
You can use the chart in these ways:
- Hover over a part to see the status and number information.
- Hover over a chart legend to highlight the related part of the chart.
- Click a chart legend to hide the related status from the visual comparison.
Want advice based on Analytics? Try asking Fluid Attacks' AI Agent!
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Organization analytics
Consult analytics on the Fluid Attacks platform to gain insights into the status of vulnerabilities and remediation practices of your organization.
Portfolio analytics
Gain insights into the security posture of your portfolios on the Fluid Attacks platform through detailed analytics.