Egress connection
Last updated: Sep 30, 2026
This page describes the architecture of the Egress connection. Fluid Attacks uses this connection to access the resources in the tests. The page also gives the minimum requirements and the limitations. The connection uses dedicated Cloudflare egress IPs.
High-level architecture
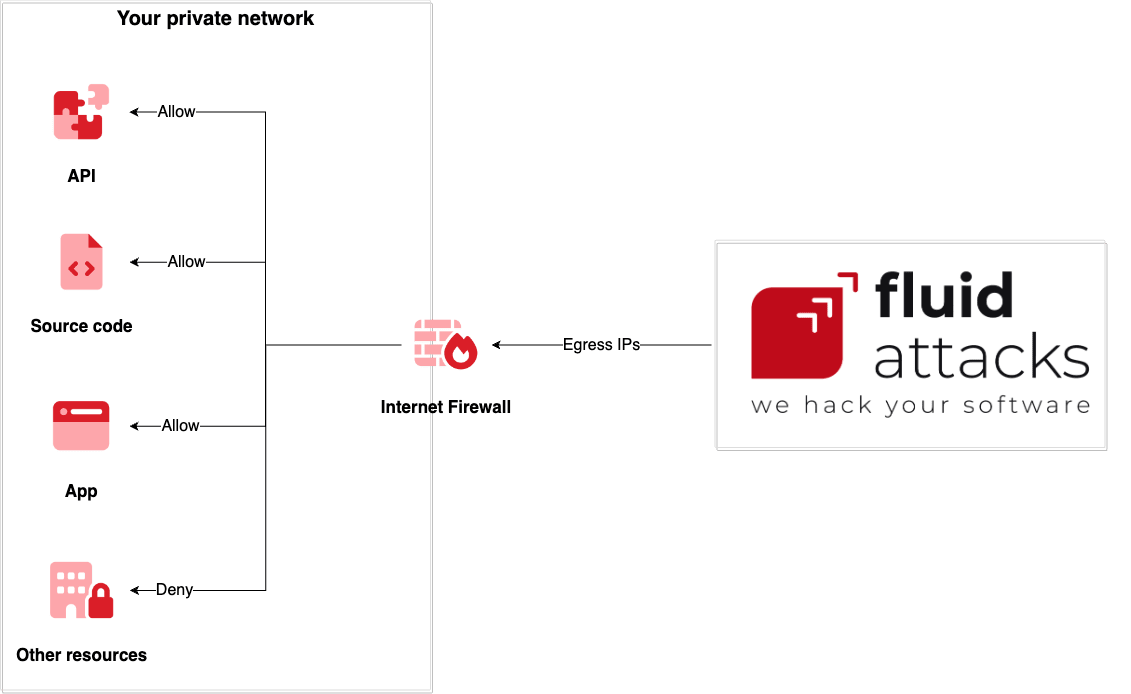
In this option, Fluid Attacks accesses your resources from public egress IP addresses. These addresses are static. They do not change. This keeps the access the same each time and reliable.
To give Fluid Attacks access to the resources in your network, whitelist the egress IP addresses on your firewall. Fluid Attacks and your resources then connect through the Internet in a secure channel.
This diagram shows how the Egress scheme works:
Minimum requirements
To use the Egress connection, make sure of these conditions:
- Public IP requirement: Your resources must have a public IP address, or an external route must connect to them. If not, Fluid Attacks cannot connect. For resources behind a NAT or a private network, more configuration can be necessary. One solution is Port Address Translation (PAT), also called NAT overload. PAT lets many devices in a private network share one public IP address. It translates the IP addresses and also the port numbers.
- Firewall configuration: Whitelist the egress IP addresses of Fluid Attacks in your firewall rules. Open only the necessary ports and protocols.
- Connection form: Complete and send the connection form with the correct configuration details. Fluid Attacks makes the connection in eight business hours after you send the form.
Egress IP addresses
IPv4
- Primary IP: 104.30.132.78
- Backup IP: 104.30.134.27
IPv6
- Primary IP: 2a09:bac0:1000:252::/64
- Backup IP: 2a09:bac0:1001:1cb::/64
The primary IP addresses are the points of egress for most traffic: 104.30.132.78 for IPv4 and 2a09:bac0:1000:252::/64 for IPv6. Most outbound requests use them. If you can whitelist only one IP, select the primary IP.
Limiting access
Fluid Attacks needs access to your resources through the egress IP addresses. Keep the remaining part of your environment secure. Apply the principle of least privilege: configure your firewall rules to expose only the resources necessary for the security testing. This limits the access to sensitive information and systems and reduces the risk.
Service limitations
If your sites use self-signed SSL certificates, the connection does not examine the HTTPS traffic. The logs then contain less information. The cause is the Cloudflare network. The connection runs on it, and it needs certificates from trusted Certificate Authorities (CAs) for full validation and logging. Use SSL certificates from an approved CA to get complete navigation logs.
Authentication
This connection supports these authentication mechanisms:
| OAuth | SSH | HTTPS |
| ❌ | ✅ | ✅ |
Frequently asked questions
What is the purpose of the Egress connection?
The Egress connection gives Fluid Attacks secure access to your resources for security testing. It uses dedicated Cloudflare Egress IPs.
Do my resources need a public IP?
Yes. See Minimum requirements for the details and for the NAT and PAT options.
Why are a wait and a form necessary for Egress if it is only a public IP?
Fluid Attacks uses the form and the processing time to configure its automated cloning service. The service must use the Egress connection to access your resources.
What IP addresses should I whitelist?
Whitelist these egress IP addresses:
- IPv4: 104.30.132.78 (primary) and 104.30.134.27 (backup)
- IPv6: 2a09:bac0:1000:252::/64 (primary) and 2a09:bac0:1001:1cb::/64 (backup)
Must I configure a public DNS for my resources?
No, a public DNS is not mandatory. It makes the access easier, thus we recommend it. Other methods can resolve the hostnames internally.
Cloud connection
Fluid Attacks works over secure and efficient cloud connection with HTTPS and SSH encryption. Requires Internet. Supports OAuth, SSH and HTTPS authentication.
Connector connection
Securely connect Fluid Attacks to your private network for vulnerability assessments using Connector. Learn how to set up and configure ZTNA.