Automatic remediation
Last updated: Nov 13, 2026
Always examine the accuracy of the remediation suggestions from the AI.
With the Autofix feature of Fluid Attacks, you remediate vulnerabilities in your source code fast. Autofix uses generative AI. It suggests custom changes that make your vulnerable code secure. The feature is at this time available in the Fluid Attacks extensions for VS Code, Cursor, and IntelliJ.
Below is a short explanation of how Autofix works and how to use it.
How Autofix works
Autofix is part of the Fluid Attacks extensions for VS Code, Cursor, and IntelliJ. The extensions get the vulnerability reports from the Fluid Attacks platform. They show the vulnerable lines of code in the IDE.
Autofix uses Claude Sonnet 4.6, an AI model from Anthropic, for code analysis and code generation. The model finds the vulnerability and produces a targeted fix. This saves you time and work in the remediation.
Autofix sends all of the vulnerable file from your IDE to Fluid Attacks. Fluid Attacks sends the function that has the vulnerability, the import statements of the file, and the vulnerable line to the model. For a configuration or infrastructure file, it sends a part of the file near the vulnerable line. If it cannot find the function, it sends the file, up to a size limit. For a vulnerability in a dependency, Autofix sends the dependency files of the project, for example, the manifest and the lock file. The model makes the actions that remediate the vulnerability. It returns the code with the fix applied. For details on how Fluid Attacks uses Claude and protects your data, read the IDE extension FAQ.
Use Autofix
Autofix uses Claude to fix vulnerable code automatically. Before you start, install the Fluid Attacks VS Code extension, Cursor extension, or IntelliJ plugin. Then follow these steps:
-
Click the Fluid Attacks extension in the activity bar of the IDE. Find the file with the vulnerability that you want to fix.
-
Click the Autofix icon next to that file. The icon is a hammer and wrench on VS Code and Cursor, and a wrench on IntelliJ.
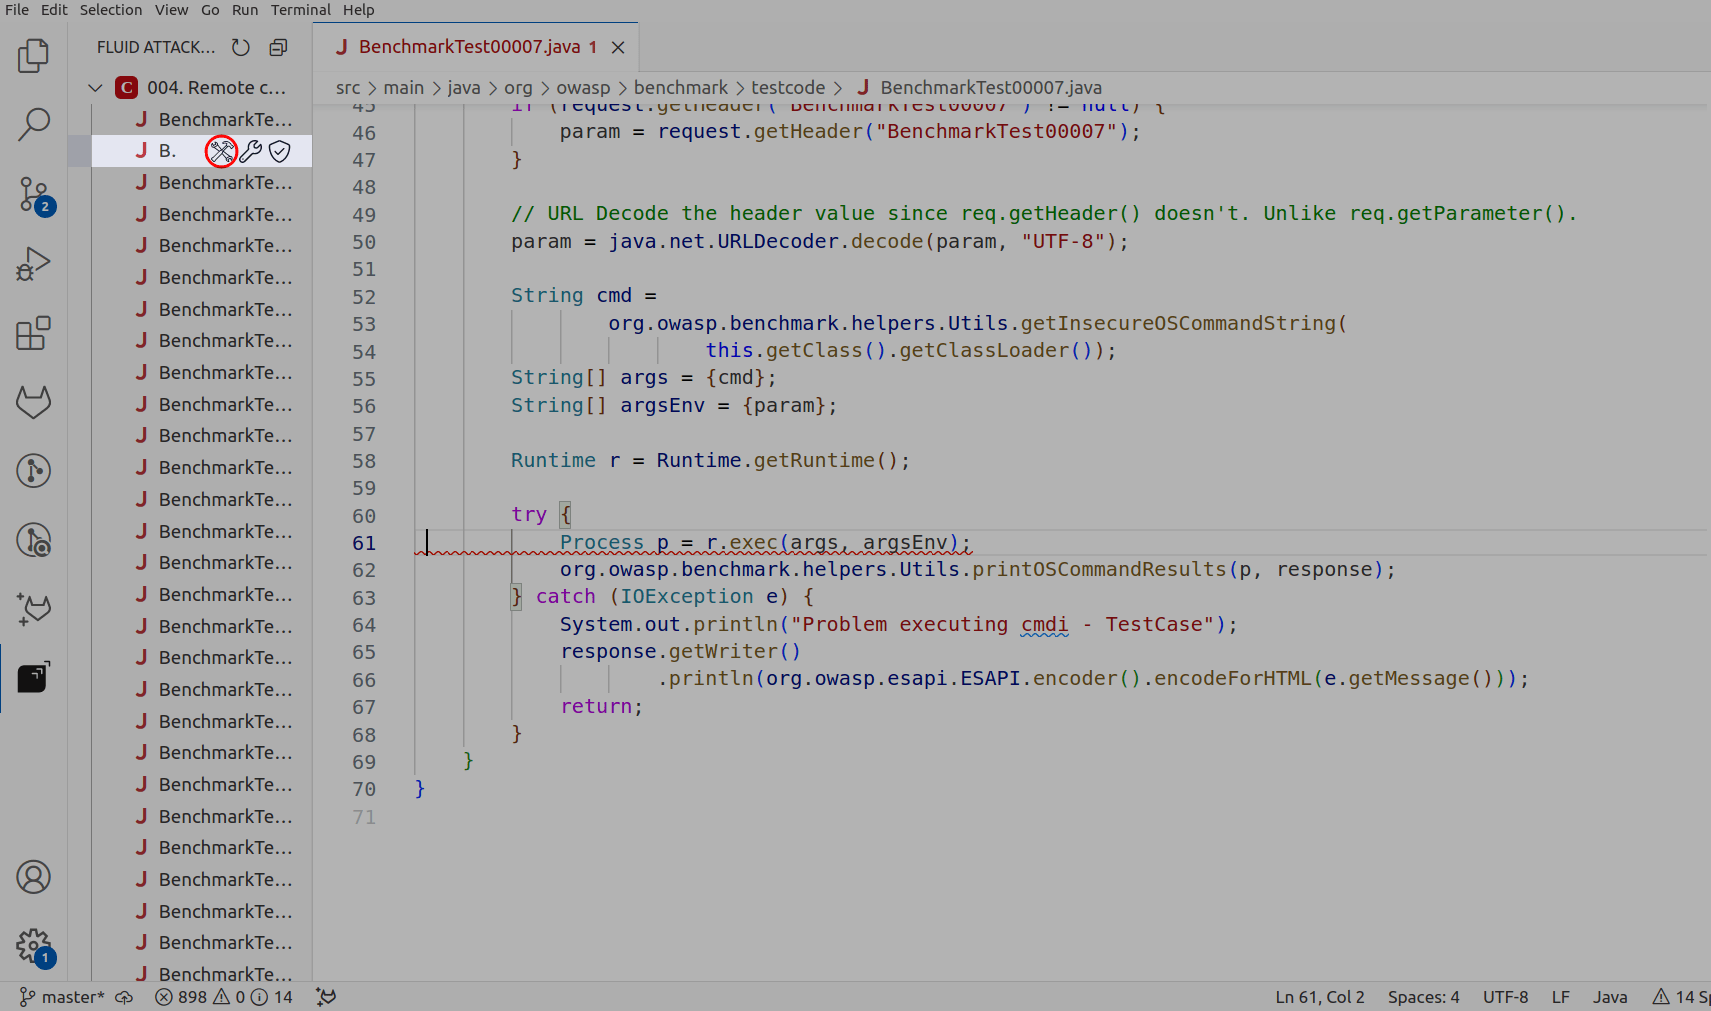
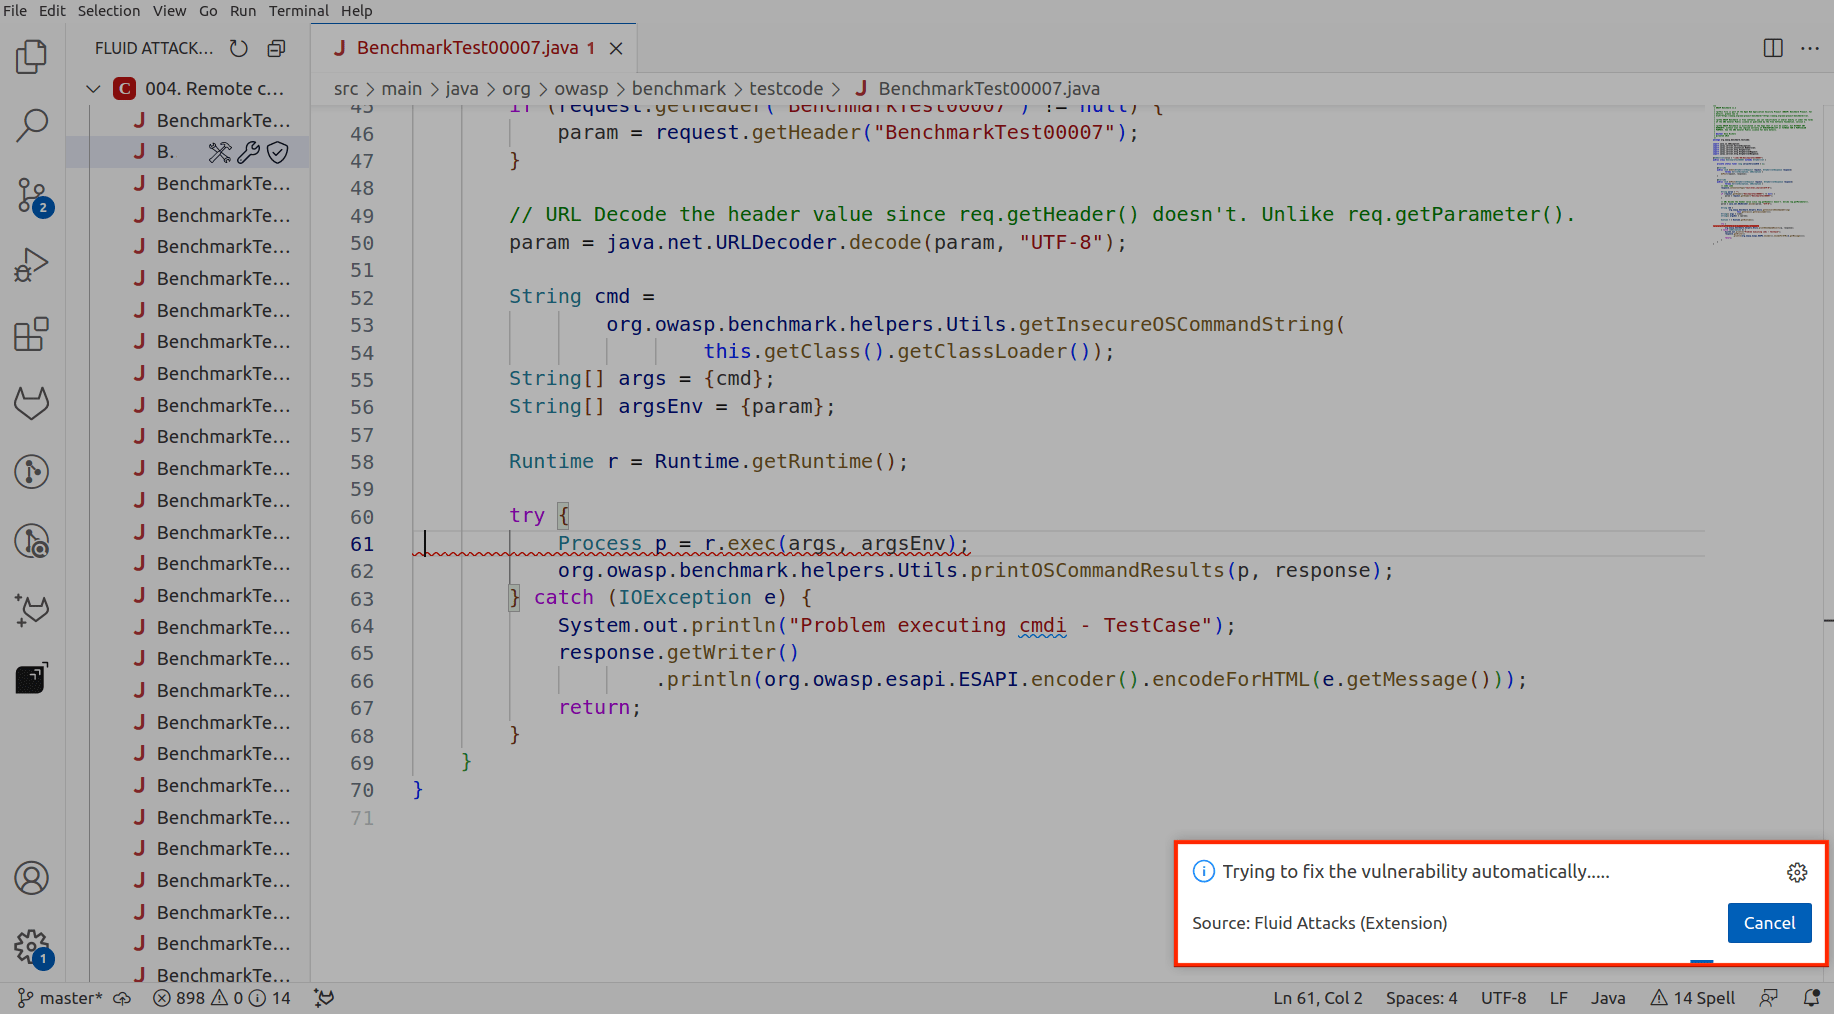
Autofix connects to the Claude AI model. The model analyzes the code and makes the fix. During this procedure, you see the message "Trying to fix the vulnerability automatically."
-
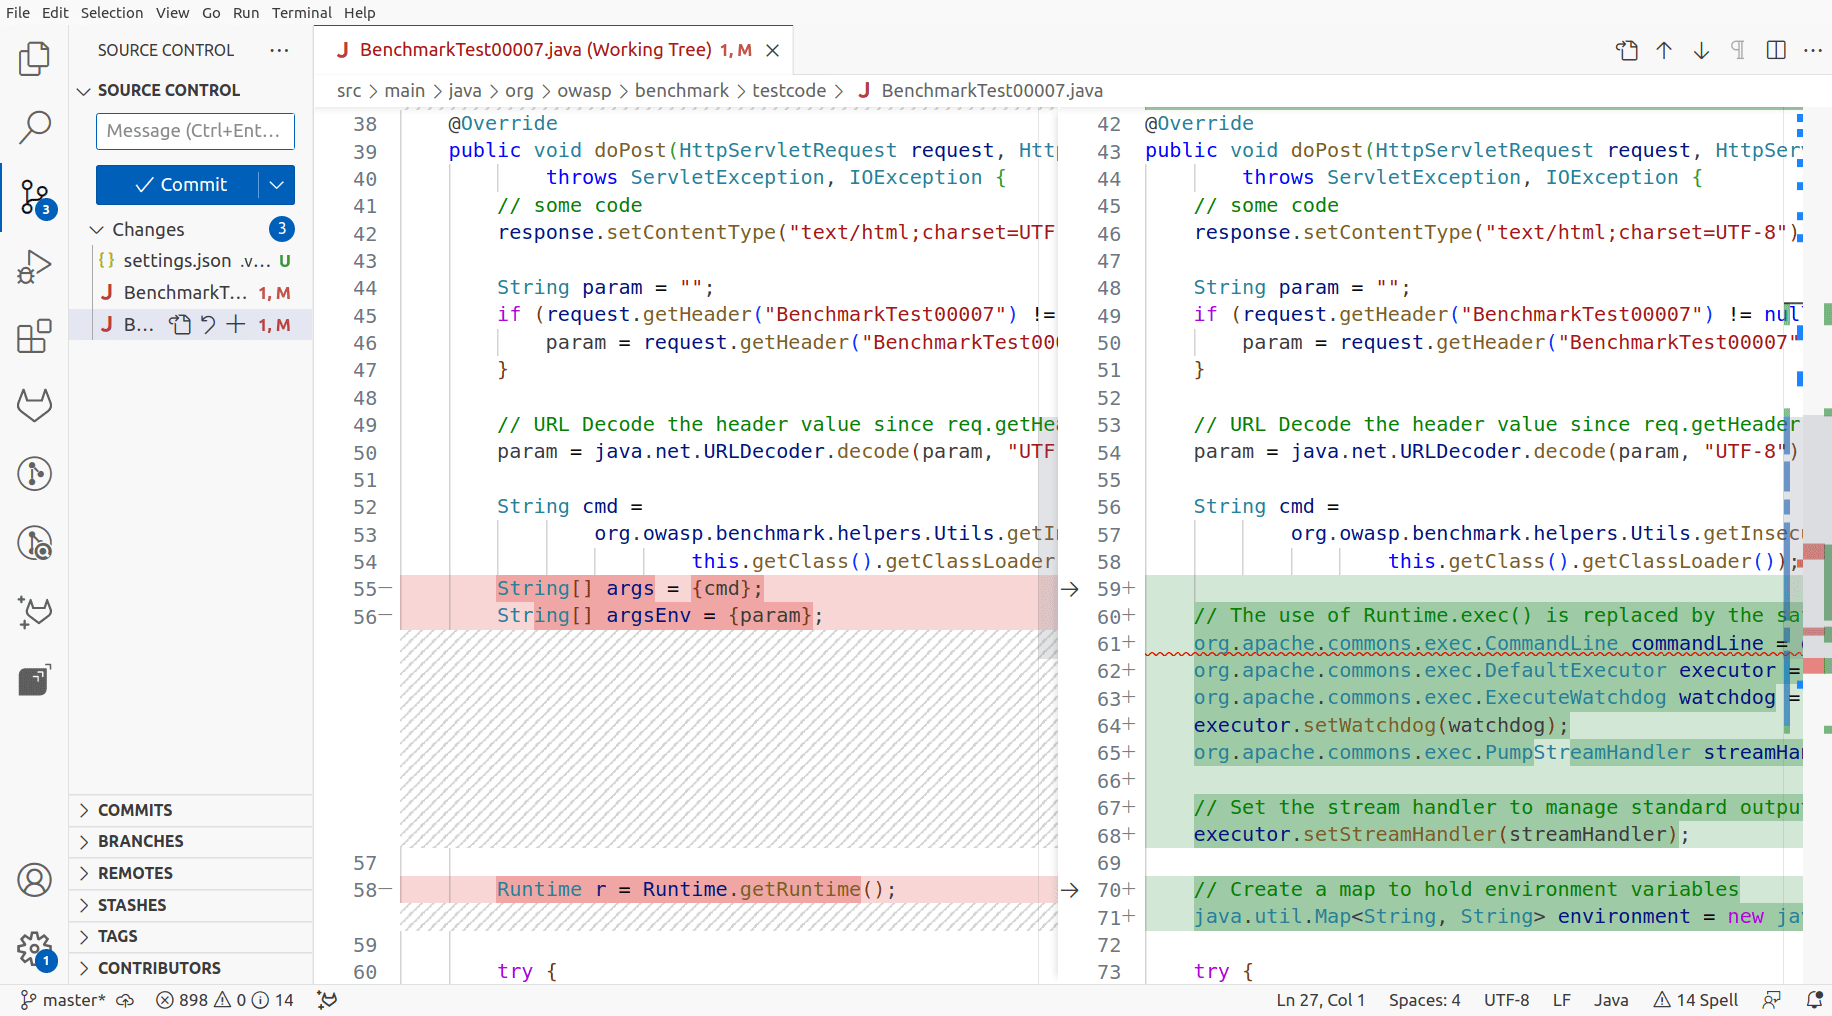
After some seconds, Autofix changes the code. Examine the suggested fix. Continue only after you make sure that the code is secure.
The Fluid Attacks GenAI uses the Fixes documentation. It covers languages, infrastructure as code (IaC), and configuration files, such as Android, Azure, CloudFormation, Docker, Docker Compose, Helm, JavaScript, Kotlin, and Terraform.
Search for vulnerabilities in your apps for free with Fluid Attacks' automated security testing! Start your 21-day free trial and discover the benefits of the Essential plan. If you prefer the Advanced plan, which includes the expertise of Fluid Attacks' pentesting team, complete this contact form.
Secure Context
Learn how a developer writes new code with Fluid Attacks Secure Context, what the feature does, and what its limits are.
Custom remediation guides
Learn to use the generative artificial intelligence integrated with the Fluid Attacks VS Code extension to receive specific vulnerability remediation guidance.