Update dependencies
Last updated: Oct 26, 2026
Role required: User, Vulnerability Manager or Group Manager
Fluid Attacks identifies vulnerable dependencies in your environment and gives you upgrade paths. For each vulnerability, you get three options. Thus, you can select the best balance between security and stability.
How to access recommendations
-
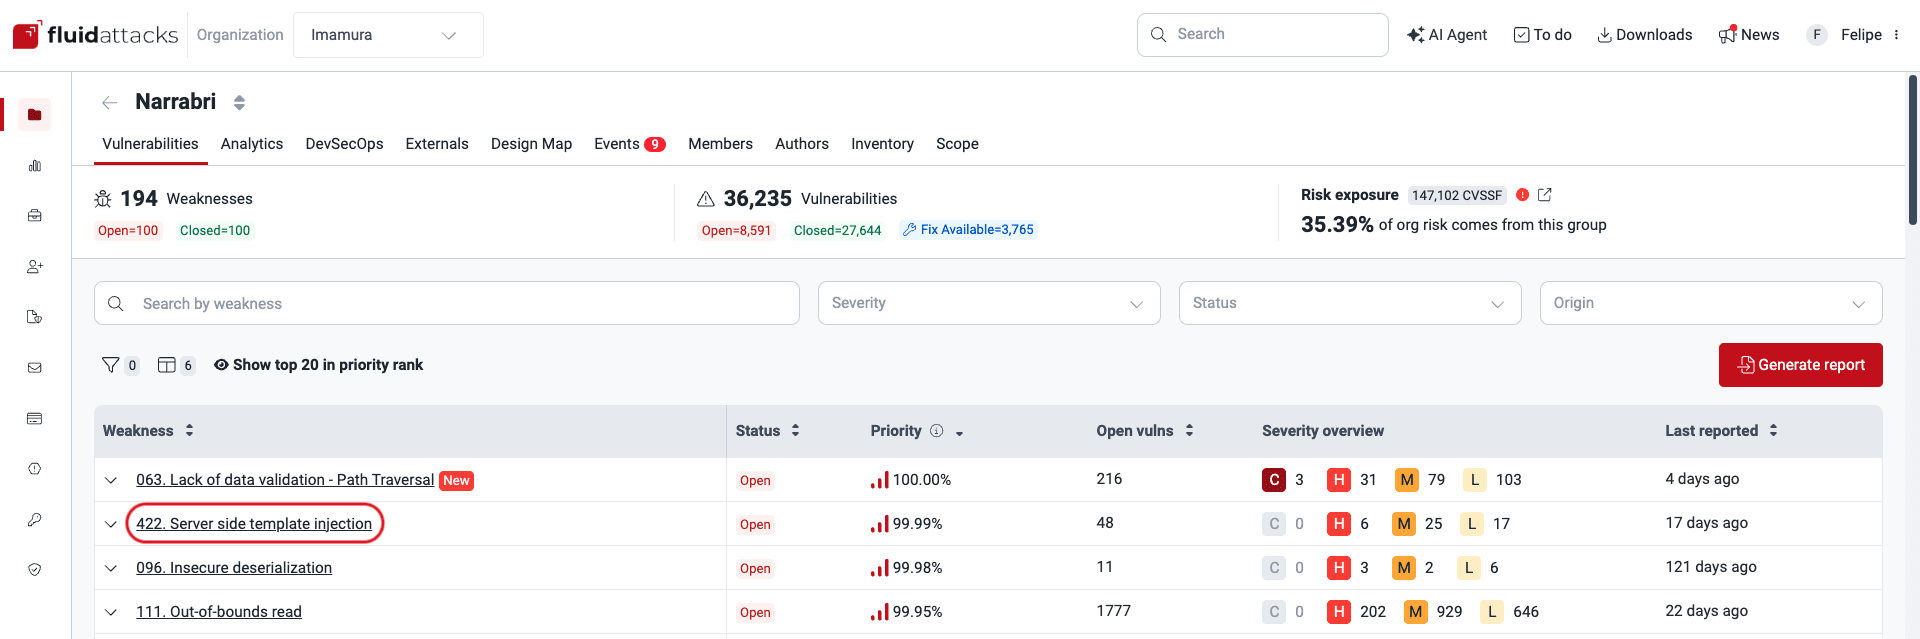
Go to the group that has the vulnerability. Then click the weakness name.
-
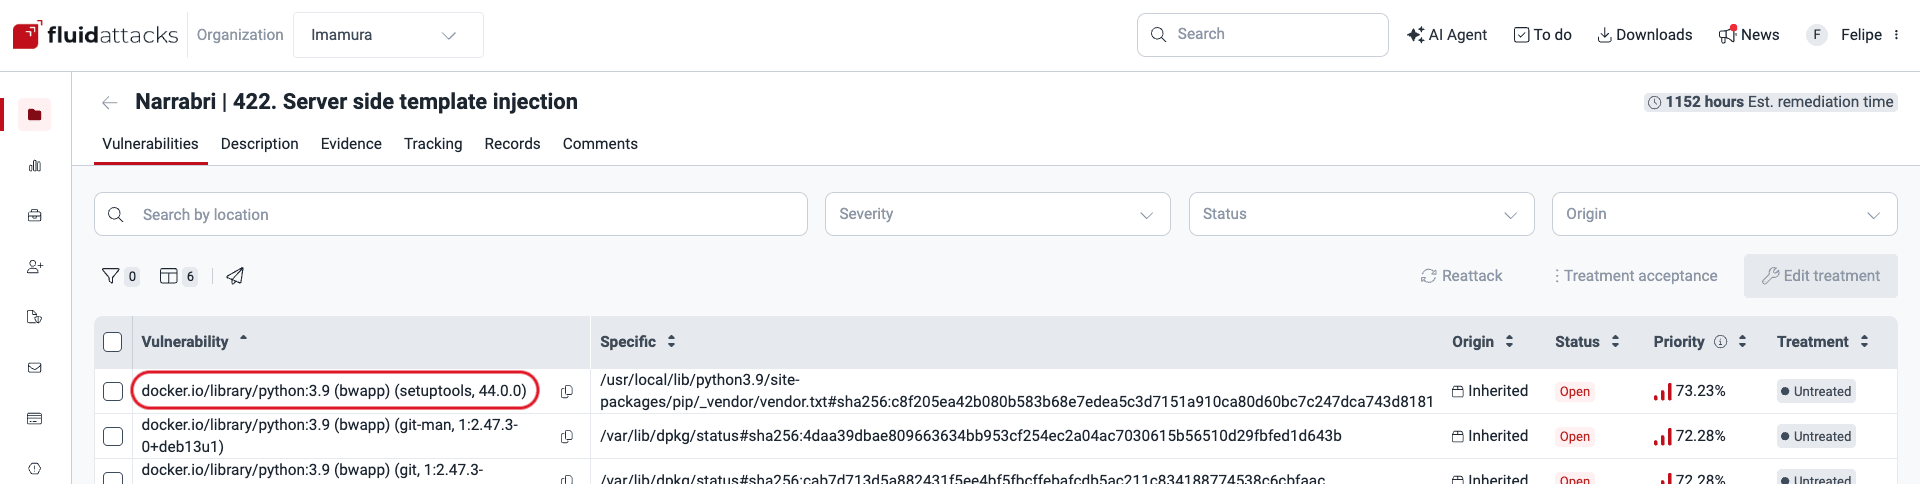
In the vulnerabilities table, click the third-party software vulnerability that you want to examine.
-
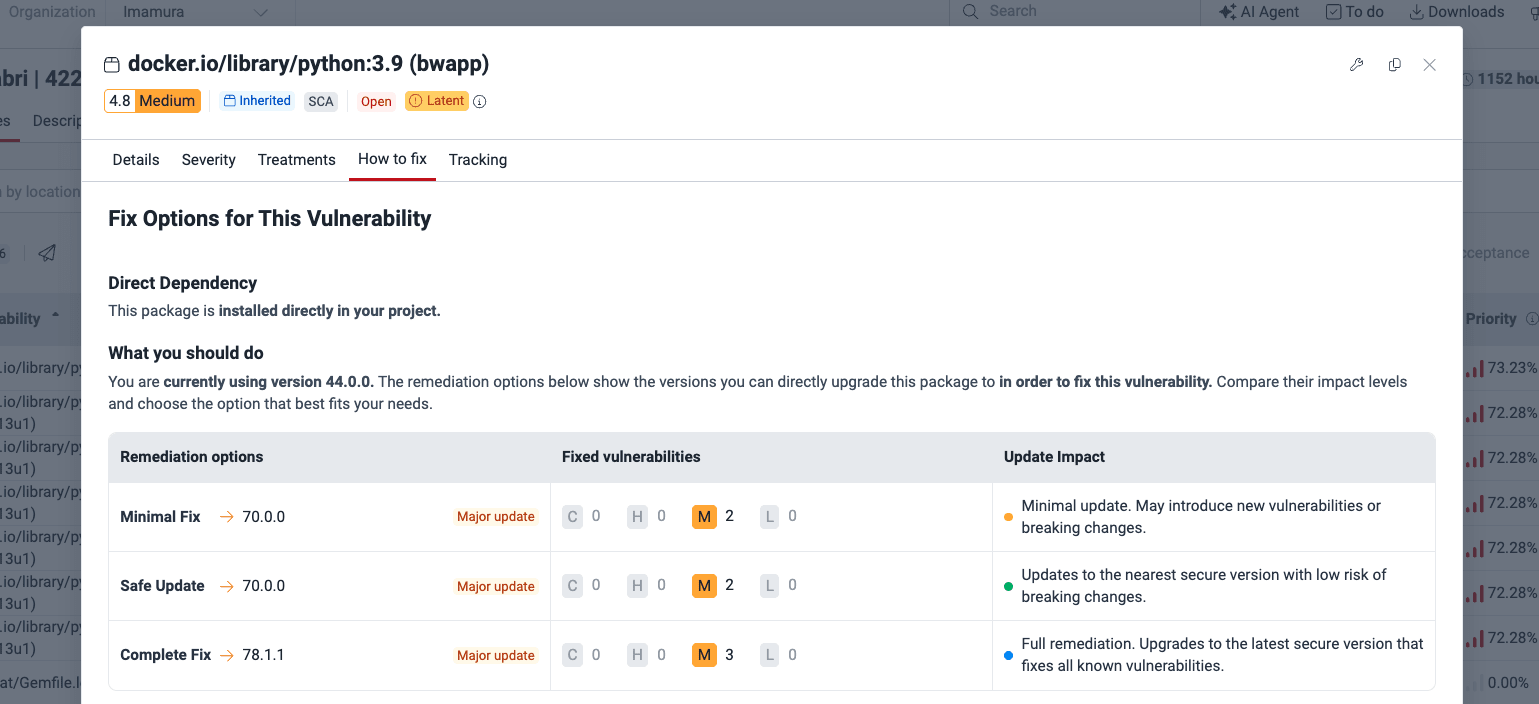
In the pop-up window, go to the How to fix tab.
Understanding the three update options
For each vulnerability, Fluid Attacks examines the dependency tree and gives three remediation paths:
- Minimal fix: Fixes the reported vulnerability, but it can add new vulnerabilities.
- Safe update: Fixes the reported vulnerability and does not add new ones.
- Complete fix: Updates to the latest version that has no known vulnerabilities.
Direct dependencies
If the vulnerability is in a package that you manage directly, you see the versions available for a direct upgrade.
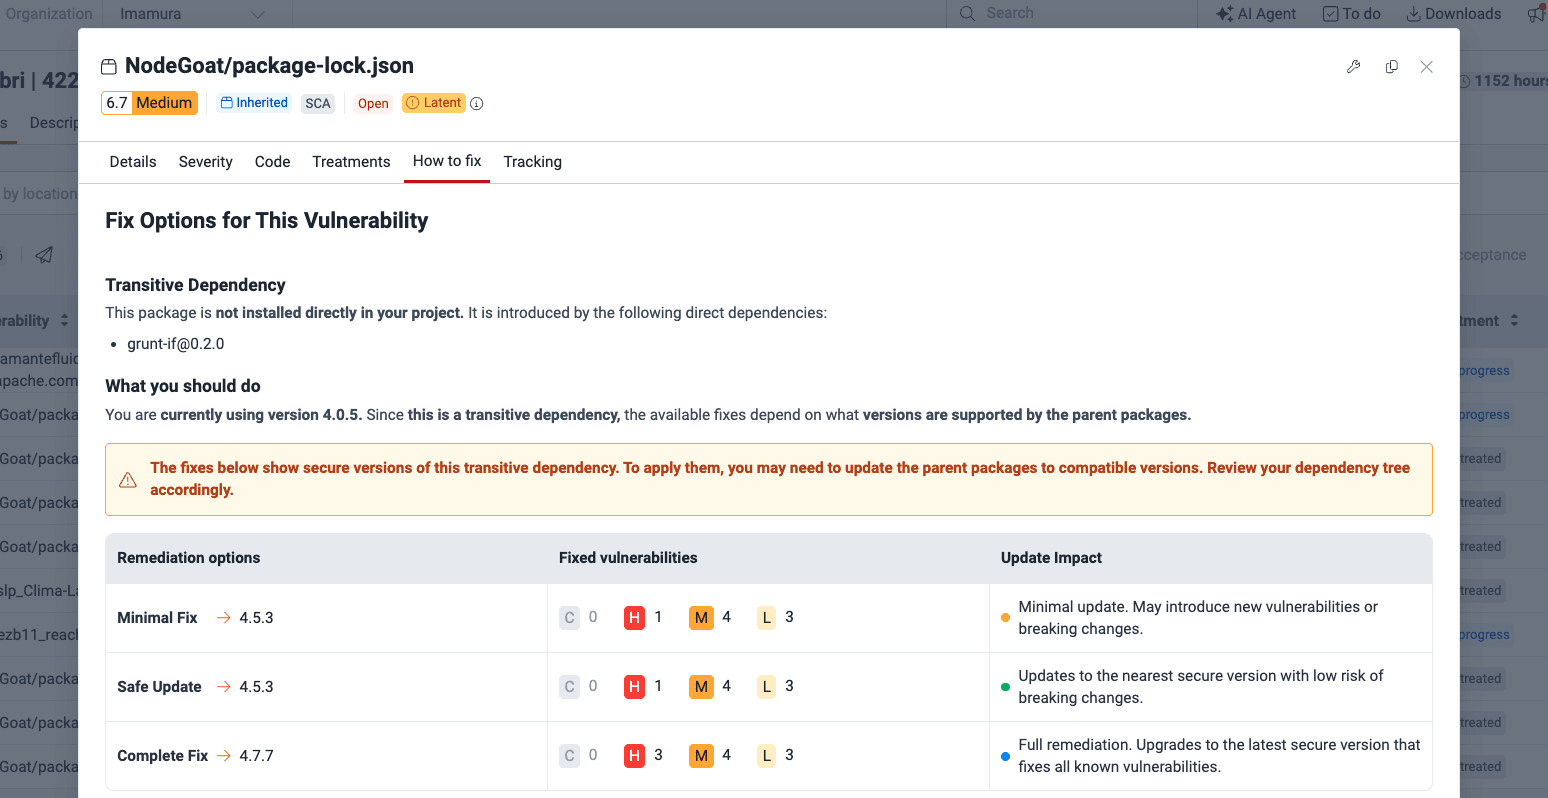
Transitive dependencies
For vulnerabilities that come from sub-dependencies, the platform identifies the direct package that includes the vulnerable code. Fluid Attacks gives the three remediation versions for the transitive dependency. Thus, you can make sure that the parent package is compatible, or update it to the minimum supported version.
Next steps
When you upgrade your dependencies to a recommended, safe version, run a reattack. The reattack examines the fix. If the fix works, the reattack closes the vulnerability.